mirror of
https://github.com/tuxdotrs/nix-config.git
synced 2026-09-19 16:49:04 +05:30
Compare commits
66 Commits
7614a68027
...
main
| Author | SHA1 | Date | |
|---|---|---|---|
8a6ac1a533

|
|||
|
c009f2be73
|
|||
|
8ef160a991
|
|||
|
c179b45ac1
|
|||
|
ac750098b1
|
|||
|
75ecf511e6
|
|||
|
e48e2903ac
|
|||
|
69882de18a
|
|||
|
e1632cb506
|
|||
|
43b3be09e5
|
|||
|
f960a5eb04
|
|||
|
23dfd5b998
|
|||
|
2b3e4661b3
|
|||
|
cdce741599
|
|||
|
e520cf6767
|
|||
|
30e33cb768
|
|||
|
dc750c6bfe
|
|||
|
80469632b1
|
|||
|
9bb2e1f11d
|
|||
|
3b9774a20d
|
|||
| 932bf56972 | |||
|
dedda22aea
|
|||
|
ef09a8a5d4
|
|||
|
51c6925364
|
|||
|
dbd2353273
|
|||
|
b6aa11fb56
|
|||
|
f08e67c36e
|
|||
|
bd977c0941
|
|||
|
e6ffe8698f
|
|||
|
ac3a0404bc
|
|||
|
cba375a888
|
|||
|
acb825e1db
|
|||
|
344d8bdd4a
|
|||
|
49a341d6b3
|
|||
|
9c77654697
|
|||
|
dacbe6bc24
|
|||
|
33a1e9da9c
|
|||
|
c6b12d6ff9
|
|||
|
3f6fb2e504
|
|||
| 8026816b8f | |||
|
060ecbe7da
|
|||
|
a01bd43ec9
|
|||
|
54049a60ec
|
|||
|
30929f3a7b
|
|||
|
9f190436e9
|
|||
|
884dd188c3
|
|||
|
ea526e6f88
|
|||
|
edb3678ddd
|
|||
|
b87e0889e0
|
|||
|
7a7ba68016
|
|||
|
4f5db036b6
|
|||
|
85fa1f78d0
|
|||
|
b578e3b462
|
|||
|
d0c1416f16
|
|||
|
91942539d7
|
|||
|
40276742bb
|
|||
|
915c30c804
|
|||
|
7f0d55c597
|
|||
|
ba22699df3
|
|||
|
c9a56d4a22
|
|||
|
42e073ea63
|
|||
|
033007490f
|
|||
|
9e2559b1b7
|
|||
|
8c755a5aa1
|
|||
|
69c2254f00
|
|||
|
31f4218115
|

208
README.md
208
README.md
@@ -15,196 +15,48 @@
|
||||
## Table of Contents
|
||||
|
||||
- [Hosts](#hosts)
|
||||
- [Installation](#installation)
|
||||
- [Components](#components)
|
||||
- [Showcase](#showcase)
|
||||
- [Pain](#spent-weeks-on-this-system-configuration-)
|
||||
- [Pain](#spent-months-on-this-system-configuration-)
|
||||
|
||||
## Hosts
|
||||
|
||||
| | Hostname | Board | CPU | RAM | GPU | Purpose |
|
||||
| --- | ---------- | ----------------- | ------------------ | ----- | ------------------------- | -------------------------------------------------------------------------------- |
|
||||
| 🖥️ | `sirius` | MSI X570-A Pro | Ryzen 7 5700X3D | 64GB | RTX 3080 TI + RTX 3060 TI | Triple-monitor desktop running Windows Subsystem for Linux. |
|
||||
| 💻 | `canopus` | Asus Zephyrus G15 | Ryzen 9 5900HS | 16GB | RTX 3060 | Optimized for productivity on the go and some gaming. |
|
||||
| ☁️ | `homelab` | Minisforum MS-A1 | Ryzen 7 8700G | 32GB | Radeon 780M | WIP |
|
||||
| ☁️ | `arcturus` | KVM | 4 Core | 8GB | | Primary server responsible for exposing my homelab applications to the internet. |
|
||||
| ☁️ | `alpha` | KVM | 4 Core | 4GB | | Monitors uptime and health status of all services across the infrastructure. |
|
||||
| 🥔 | `vega` | Raspberry Pi 3B+ | Cortex A53 | 1GB | | Running AdGuard Home for network-wide ad blocking. |
|
||||
| 📱 | `capella` | Samsung S25 Ultra | Snapdragon 8 Elite | 12GB | Adreno 830 | Primary mobile for daily usage. (Locked) |
|
||||
| 📱 | `rigel` | Motorola Edge 30 | Snapdragon 778G+ | 8GB | Adreno 642L | Secondary mobile for some fun. (Rooted) |
|
||||
| ☁️ | `node` | ASRock B565D4 | Ryzen 9 5950X | 128GB | | Running Ethereum and BSC nodes. |
|
||||
|
||||
## Installation
|
||||
|
||||
> [!NOTE]
|
||||
> This will get your base system ready, but keep in mind that many things might not work correctly — such as monitor resolution, font size, and more.
|
||||
|
||||
### Prerequisites
|
||||
|
||||
Boot into the NixOS bootable USB before proceeding with the installation steps.
|
||||
|
||||
### Installation Steps
|
||||
|
||||
#### 1. Clone the repository
|
||||
|
||||
```bash
|
||||
git clone https://github.com/tuxdotrs/nix-config.git
|
||||
cd nix-config
|
||||
```
|
||||
|
||||
#### 2. Gain root privileges
|
||||
|
||||
```bash
|
||||
sudo su
|
||||
|
||||
```
|
||||
|
||||
#### 3. Set up disk partitioning
|
||||
|
||||
Install the required tools:
|
||||
|
||||
```bash
|
||||
nix-shell -p disko neovim
|
||||
```
|
||||
|
||||
Partition your disk using disko. **This will wipe your drive.** Replace `DISK_PATH` with your actual disk path (e.g., `/dev/vda` or `/dev/nvme0n1`):
|
||||
|
||||
```bash
|
||||
disko --mode disko ./hosts/canopus/disko.nix --arg device '"DISK_PATH"'
|
||||
```
|
||||
|
||||
#### 4. Configure your disk
|
||||
|
||||
Edit the configuration file:
|
||||
|
||||
```bash
|
||||
nvim ./hosts/canopus/default.nix
|
||||
```
|
||||
|
||||
In the imports statement, replace:
|
||||
|
||||
```nix
|
||||
(import ./disko.nix {device = "/dev/nvme0n1";})
|
||||
```
|
||||
|
||||
with:
|
||||
|
||||
```nix
|
||||
(import ./disko.nix {device = "DISK_PATH";})
|
||||
```
|
||||
|
||||
Make sure to replace `DISK_PATH` with your actual disk path.
|
||||
|
||||
#### 5. Generate hardware configuration
|
||||
|
||||
```bash
|
||||
nixos-generate-config --no-filesystems --root /mnt
|
||||
```
|
||||
|
||||
Copy the generated hardware configuration to the repository:
|
||||
|
||||
```bash
|
||||
cp /mnt/etc/nixos/hardware-configuration.nix ./hosts/canopus/hardware.nix
|
||||
```
|
||||
|
||||
#### 6. Install NixOS
|
||||
|
||||
```bash
|
||||
nixos-install --root /mnt --flake .#canopus
|
||||
```
|
||||
|
||||
#### 7. Enter into the new system
|
||||
|
||||
```bash
|
||||
nixos-enter --root /mnt
|
||||
```
|
||||
|
||||
#### 8. Set up directories and permissions
|
||||
|
||||
```bash
|
||||
mkdir -p /persist/home
|
||||
chown -R tux:users /persist/home
|
||||
```
|
||||
|
||||
#### 9. Set passwords
|
||||
|
||||
Set the root password:
|
||||
|
||||
```bash
|
||||
passwd root
|
||||
```
|
||||
|
||||
Set the user password:
|
||||
|
||||
```bash
|
||||
passwd tux
|
||||
```
|
||||
|
||||
#### 10. Reboot
|
||||
|
||||
```bash
|
||||
reboot
|
||||
```
|
||||
|
||||
Your NixOS system should now boot into a beautiful DE.
|
||||
| | Hostname | Board | CPU | RAM | GPU | Purpose |
|
||||
| --- | ---------- | ----------------- | ------------------ | ---- | ------------------------- | --------------------------------------------------------------------- |
|
||||
| 🖥️ | `sirius` | MSI X570-A Pro | Ryzen 7 5700X3D | 64GB | RTX 3080 TI + RTX 3060 TI | Triple-monitor desktop for work, gaming, and media consumption. |
|
||||
| 💻 | `canopus` | Asus Zephyrus G15 | Ryzen 9 5900HS | 16GB | RTX 3060 | Portable workstation for work, gaming, and media on the go. |
|
||||
| ☁️ | `arcturus` | Minisforum MS-A1 | Ryzen 7 8700G | 32GB | Radeon 780M | Homelab server for self-hosted services and infrastructure workloads. |
|
||||
| ☁️ | `alpha` | KVM | 2 Core | 4GB | | Public-facing server for exposing homelab services to the internet. |
|
||||
| 📱 | `vega` | Samsung S25 Ultra | Snapdragon 8 Elite | 12GB | Adreno 830 | Primary mobile for daily usage. (Locked) |
|
||||
| 📱 | `capella` | Motorola Edge 30 | Snapdragon 778G+ | 8GB | Adreno 642L | Secondary mobile for tinkering and experimentation. (Rooted) |
|
||||
|
||||
## Components
|
||||
|
||||
| | Wayland | Xorg |
|
||||
| ------------- | -------- | ---------------- |
|
||||
| DM | ly | ly |
|
||||
| WM/DE | Hyprland | AwesomeWM |
|
||||
| Compositor | Hyprland | Picom (Jonaburg) |
|
||||
| Bar | tPanel | Wibar |
|
||||
| Hotkeys | Hyprland | Awful |
|
||||
| Launcher | tPanel | Rofi |
|
||||
| Notifications | tPanel | Naughty |
|
||||
| Terminal | Wezterm | Wezterm |
|
||||
| Editor | Neovim | Neovim |
|
||||
| | Wayland | Xorg |
|
||||
| ------------- | -------- | ---- |
|
||||
| DM | ly | - |
|
||||
| WM/DE | Hyprland | - |
|
||||
| Compositor | Hyprland | - |
|
||||
| Bar | Tshell | - |
|
||||
| Hotkeys | Hyprland | - |
|
||||
| Launcher | Tshell | - |
|
||||
| Notifications | Tshell | - |
|
||||
| Terminal | Wezterm | - |
|
||||
| Editor | Neovim | - |
|
||||
|
||||
## Showcase
|
||||
|
||||
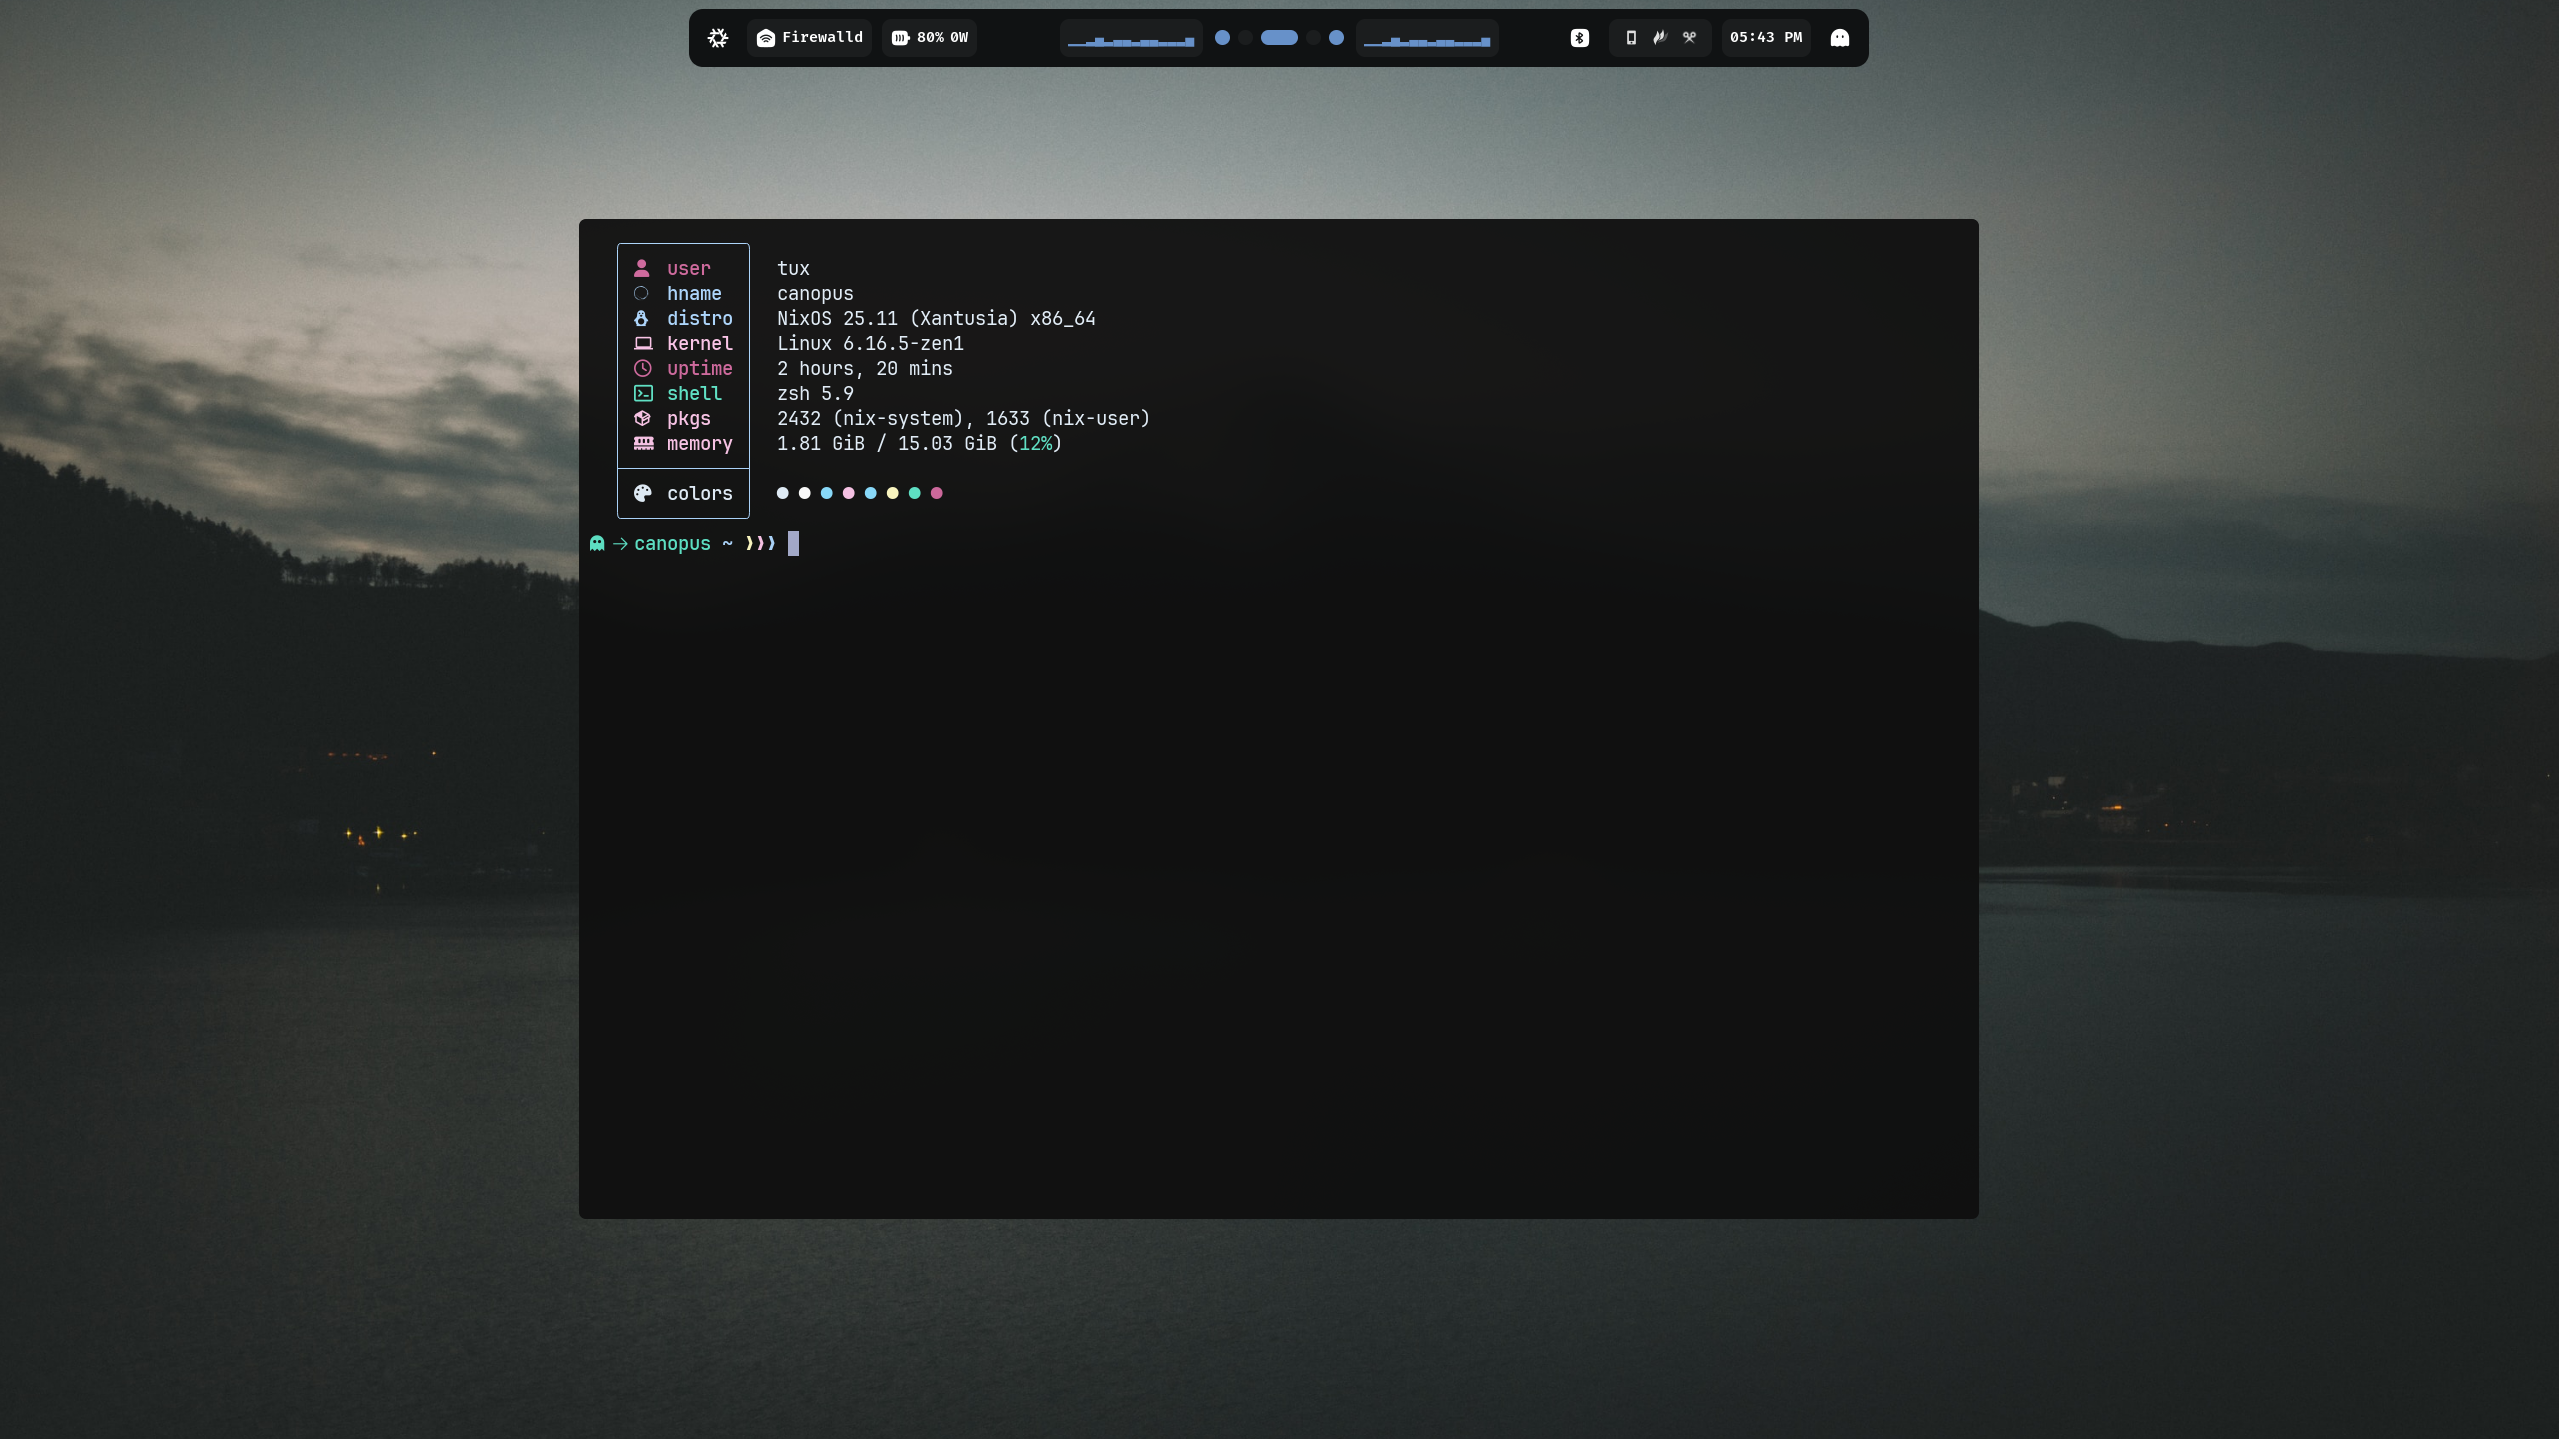
### Desktop Hyprland
|
||||
| **Desktop** | **Tshell** |
|
||||
| :-------------------------------------------------------------------------------------------------------------------------: | :-----------------------------------------------------------------------------------------------------------------------: |
|
||||
| <img src="https://raw.githubusercontent.com/tuxdotrs/nix-config/refs/heads/main/assets/hyprland/desktop.png" width="100%"> | <img src="https://raw.githubusercontent.com/tuxdotrs/nix-config/refs/heads/main/assets/hyprland/tPanel.png" width="100%"> |
|
||||
| **Workflow** | **Neovim** |
|
||||
| <img src="https://raw.githubusercontent.com/tuxdotrs/nix-config/refs/heads/main/assets/hyprland/workflow.png" width="100%"> | <img src="https://github.com/user-attachments/assets/f881c672-8d77-43ec-b637-df5004c7d11f" width="100%"> |
|
||||
| **Floating Terminal** | **Lazygit** |
|
||||
| <img src="https://github.com/user-attachments/assets/3339ecf8-3264-4179-a093-337c844592a6" width="100%"> | <img src="https://github.com/user-attachments/assets/6df15881-fc2b-41b1-af3b-124fe0599b94" width="100%"> |
|
||||
| **Telescope** | **Firefox** |
|
||||
| <img src="https://github.com/user-attachments/assets/03be05bc-8ede-4d6e-a341-2761d89b7288" width="100%"> | <img src="https://github.com/user-attachments/assets/6f12173b-2480-404e-b01a-599115a886c0" width="100%"> |
|
||||
|
||||
|
||||
|
||||
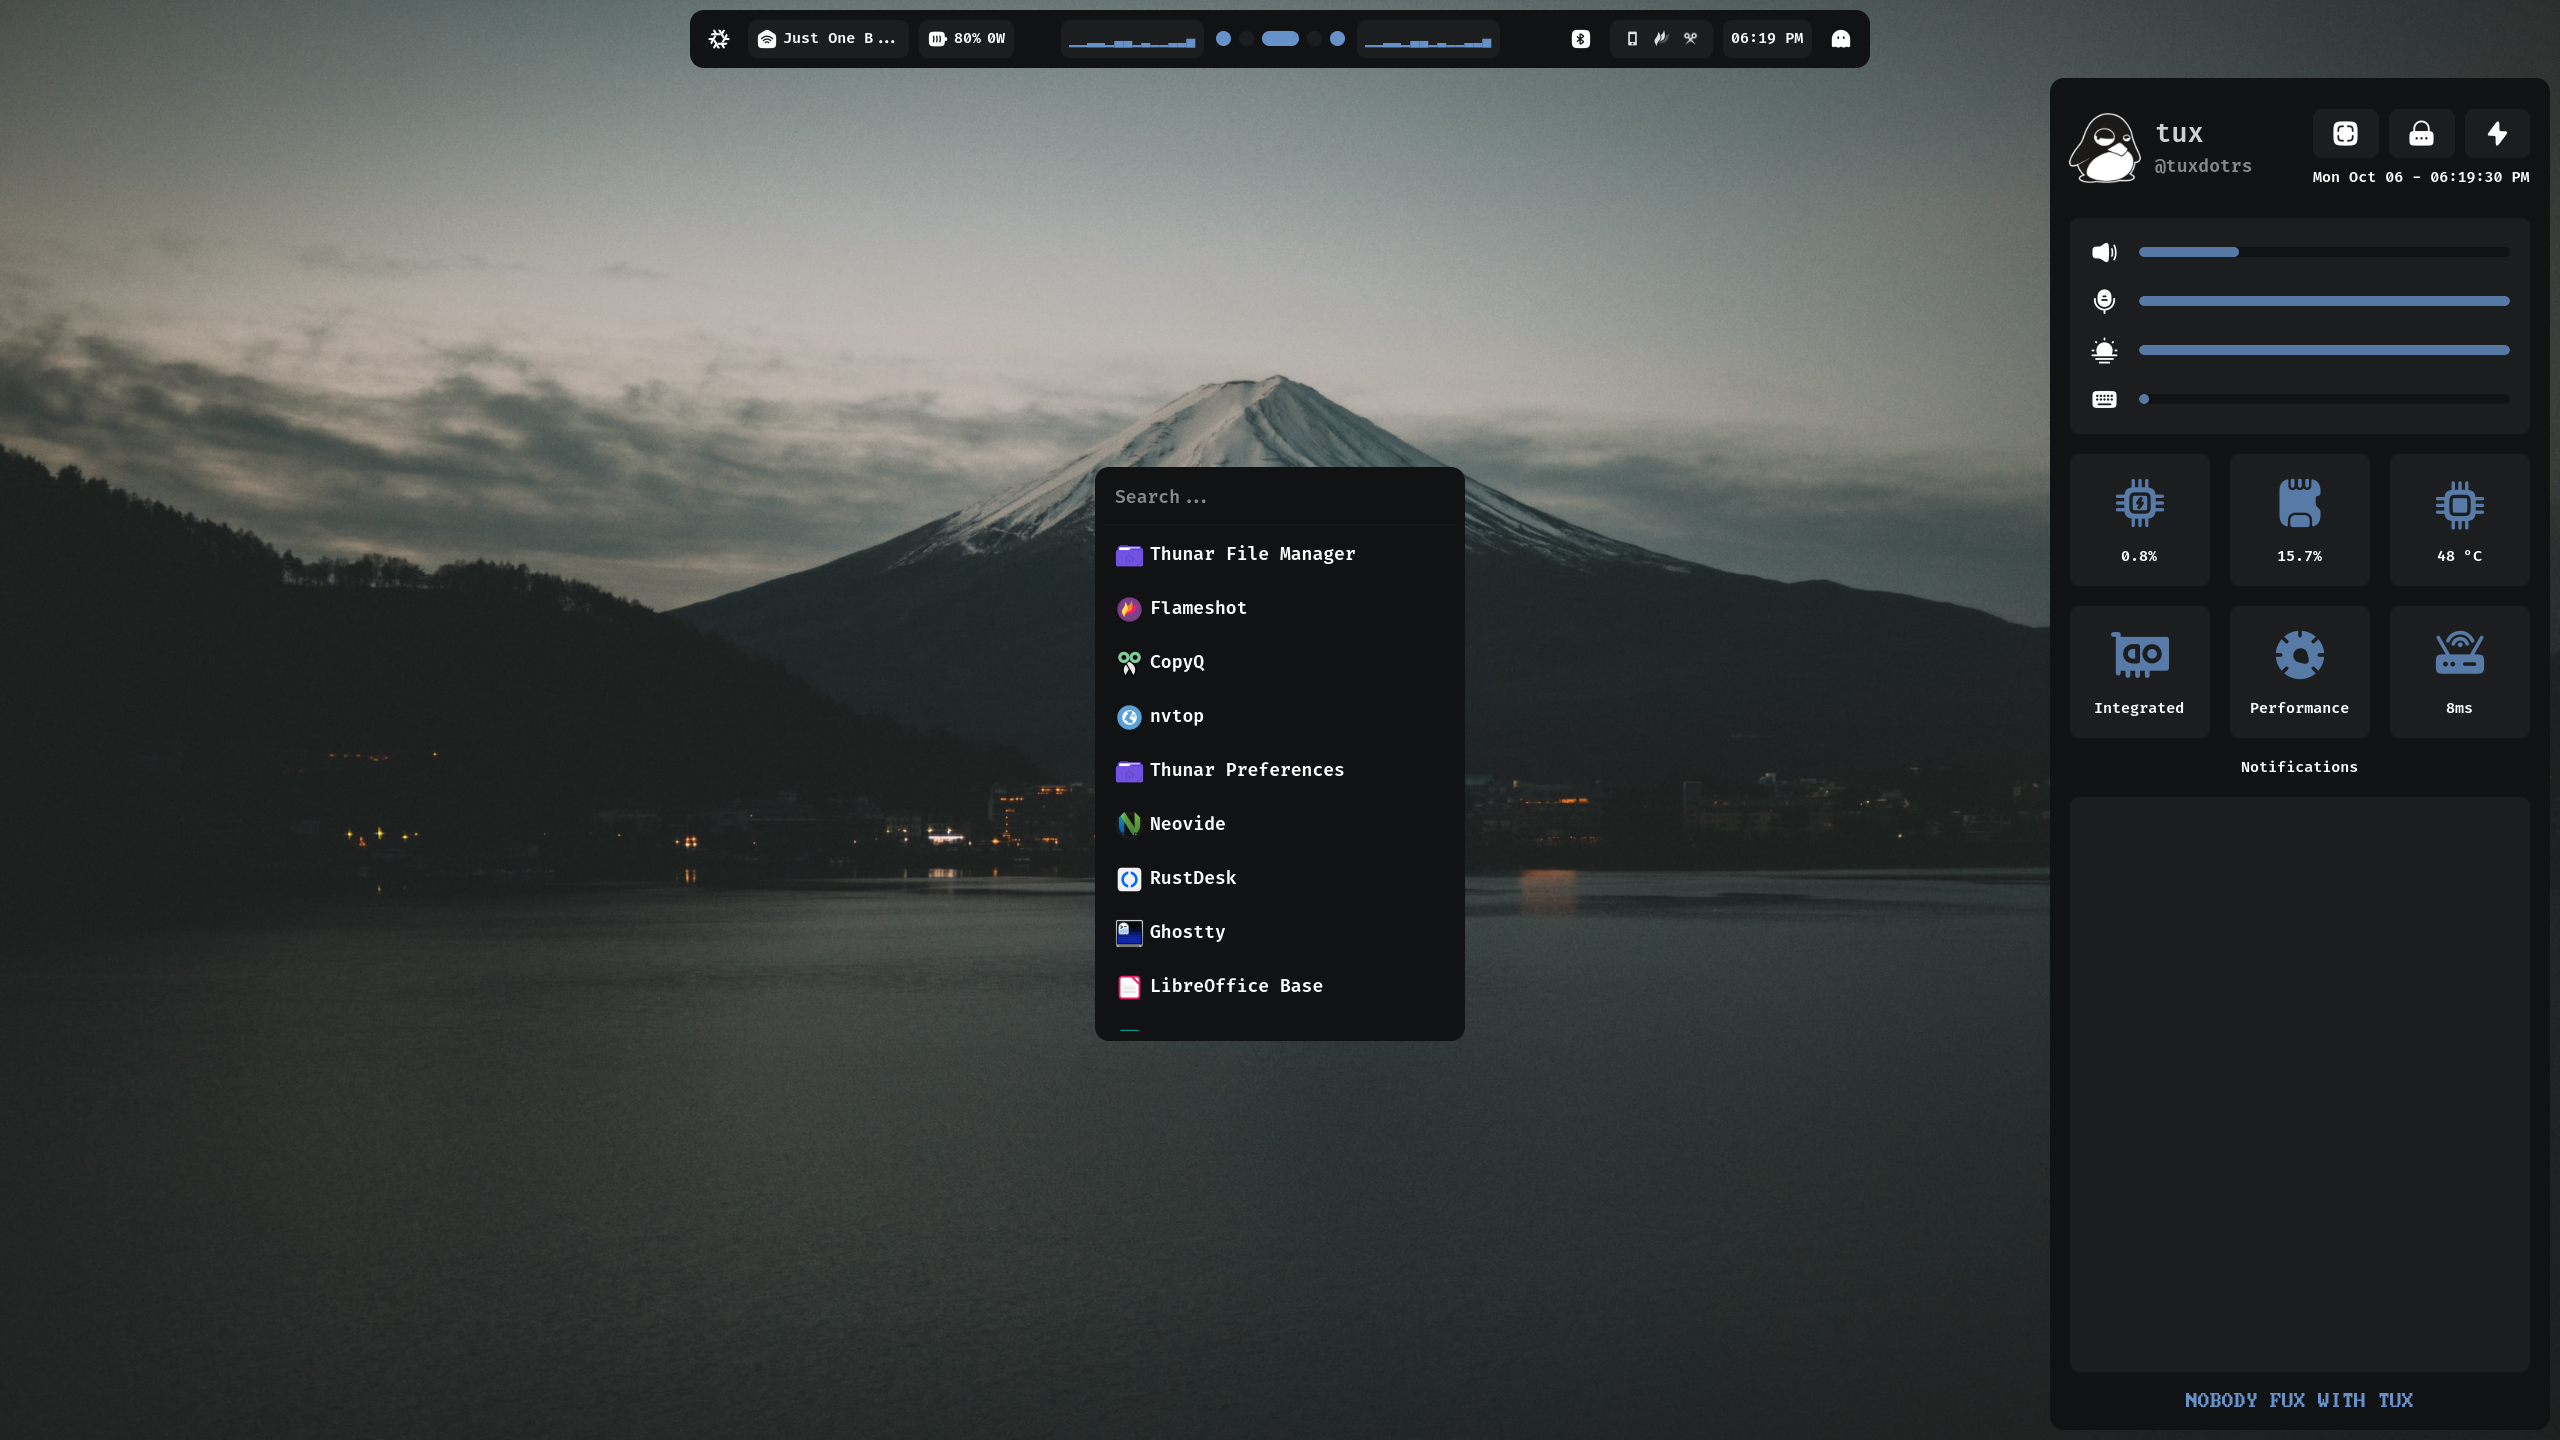
### tPanel
|
||||
|
||||
|
||||
|
||||
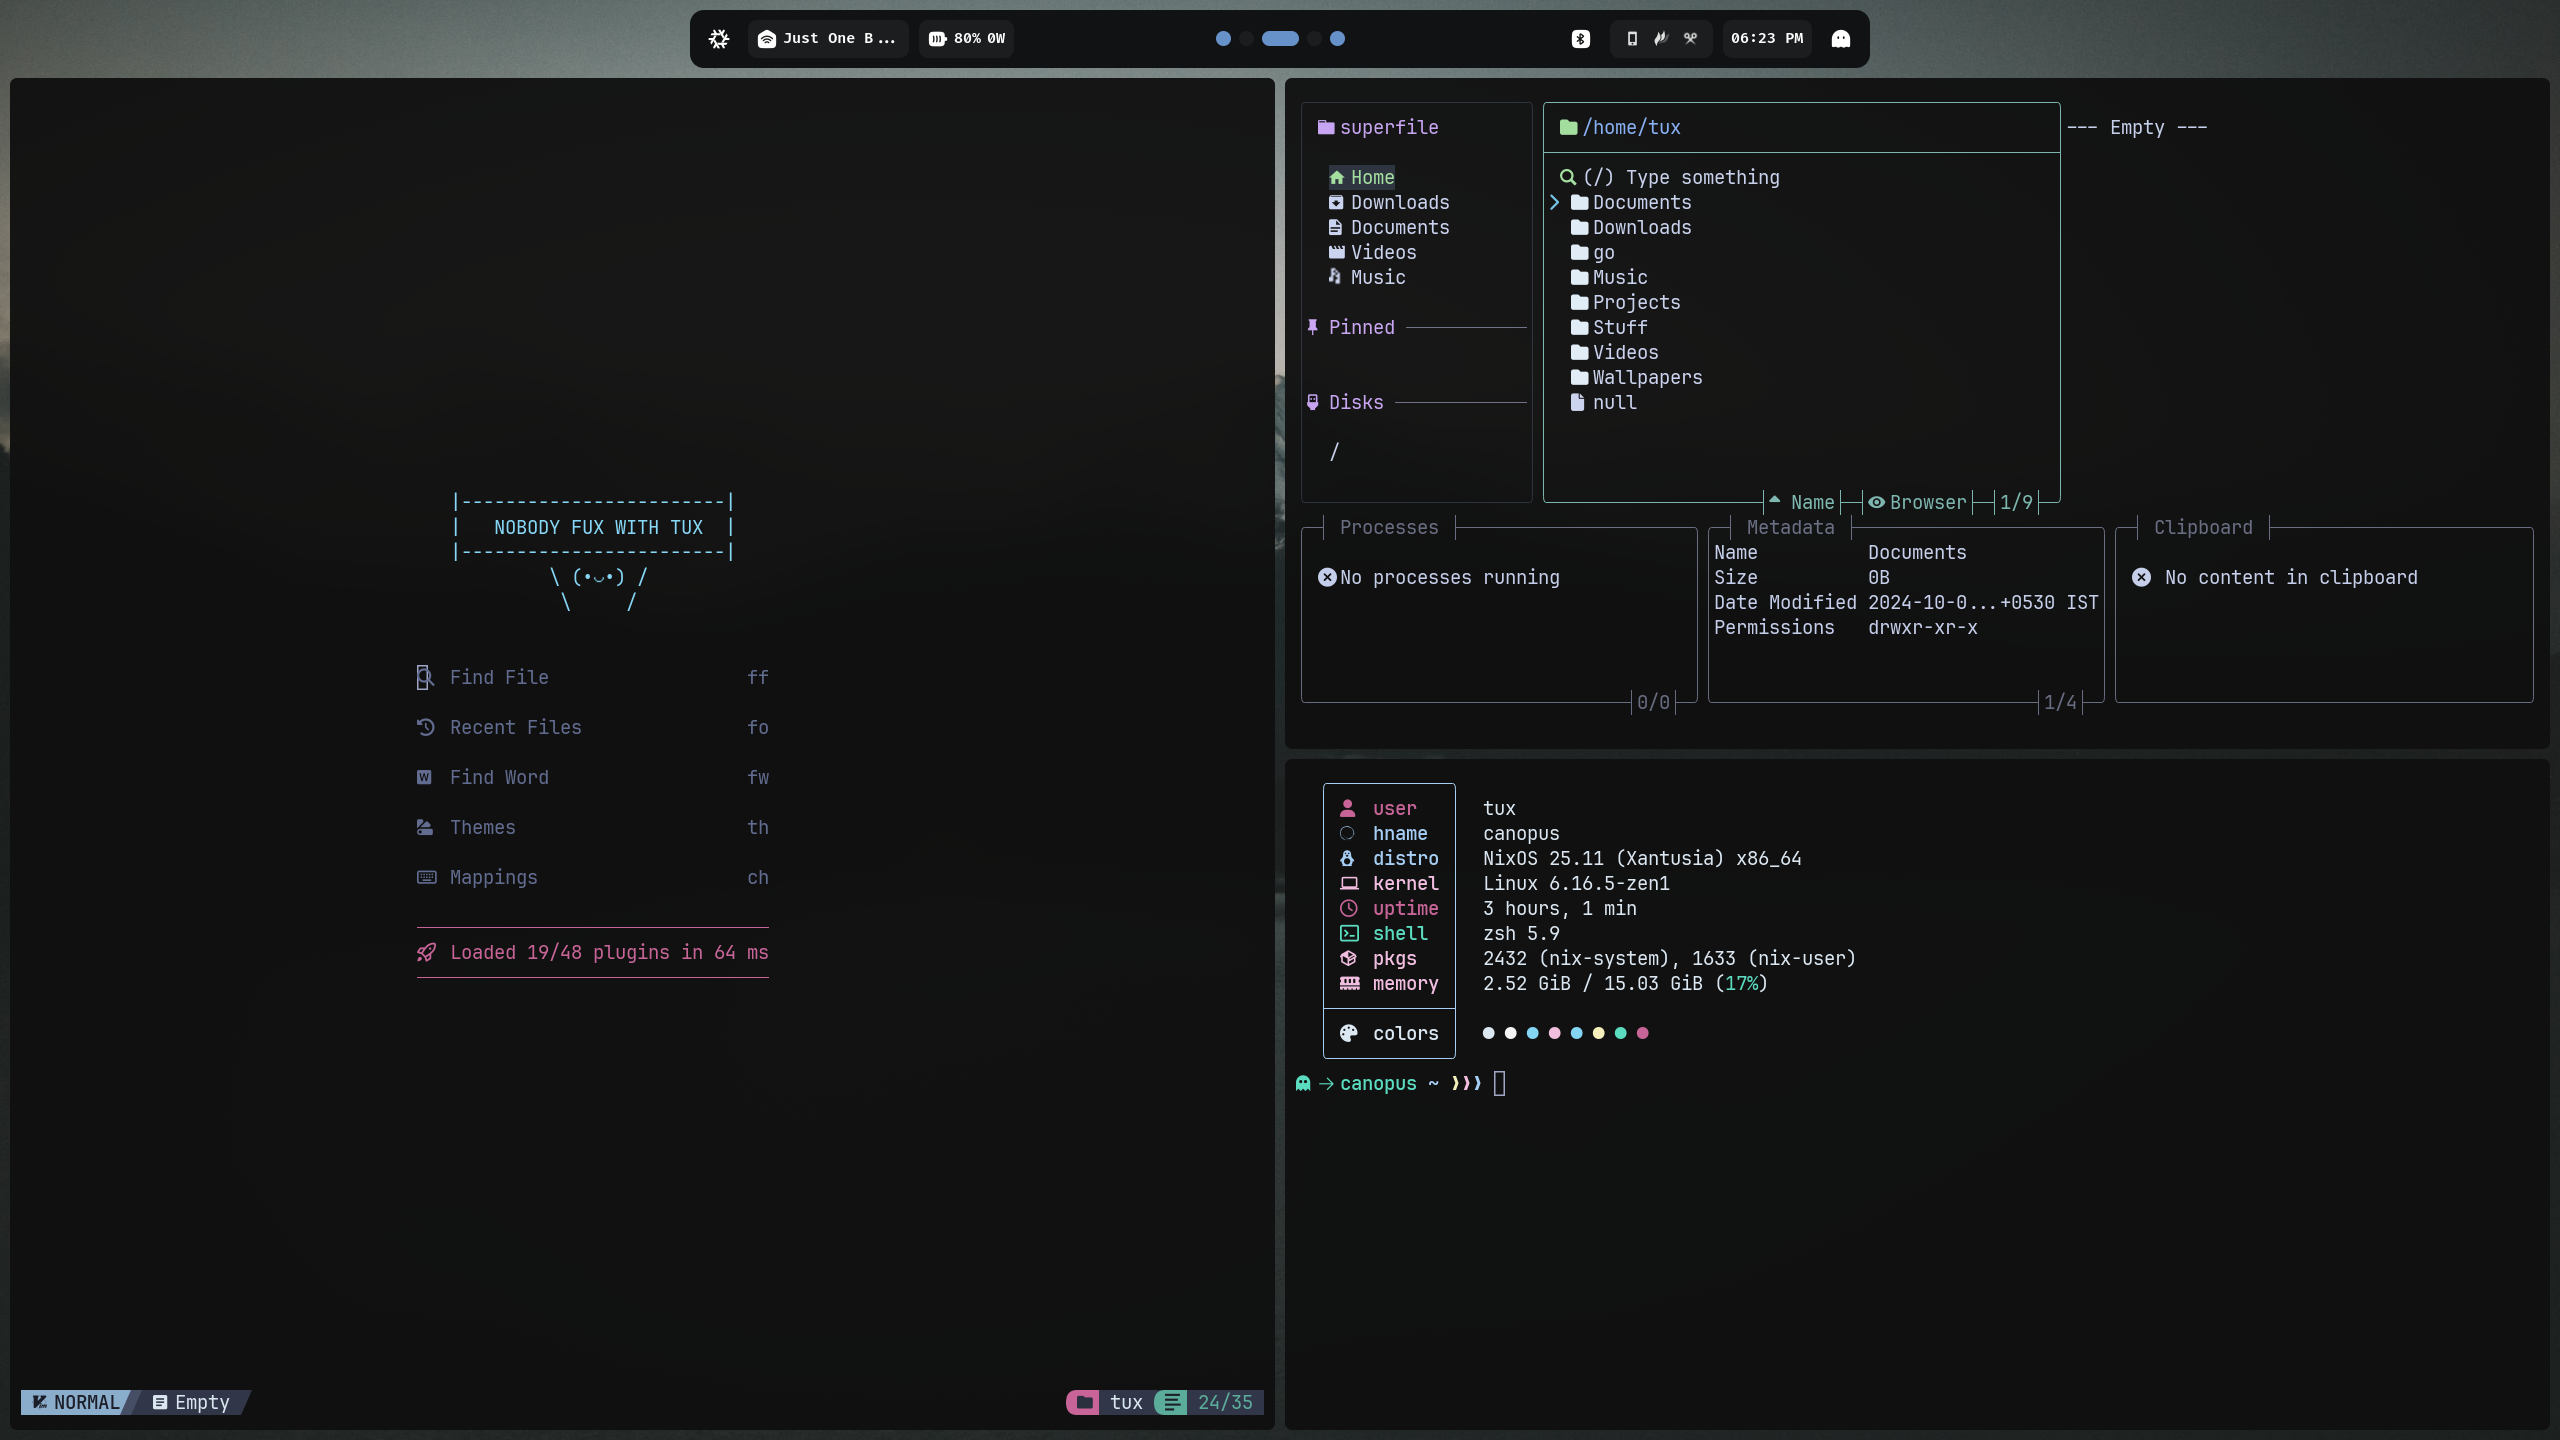
### Workflow
|
||||
|
||||
|
||||
|
||||
## Showcase
|
||||
|
||||
### Desktop AwesomeWM
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||
### Neovim
|
||||
|
||||

|
||||
|
||||
### Floating Terminal
|
||||
|
||||

|
||||
|
||||
### Lazygit
|
||||
|
||||

|
||||
|
||||
### Telescope
|
||||
|
||||

|
||||
|
||||
### Firefox
|
||||
|
||||

|
||||
|
||||
## Spent weeks on this system configuration 😢
|
||||
## Spent months on this system configuration 😢
|
||||
|
||||
<div align="center">
|
||||
<img src="https://user-images.githubusercontent.com/97862450/265550523-2f66a8b6-4347-40af-89c6-12db3a61cc7c.jpeg" width="60%">
|
||||
|
||||
994
flake.lock
generated
994
flake.lock
generated
File diff suppressed because it is too large
Load Diff
24
flake.nix
24
flake.nix
@@ -1,7 +1,7 @@
|
||||
{
|
||||
description = "tux's nix configurations";
|
||||
|
||||
outputs = inputs: inputs.flake-parts.lib.mkFlake { inherit inputs; } (inputs.import-tree ./modules);
|
||||
outputs = inputs: inputs.flake-parts.lib.mkFlake {inherit inputs;} (inputs.import-tree ./modules);
|
||||
|
||||
inputs = {
|
||||
flake-parts = {
|
||||
@@ -24,8 +24,18 @@
|
||||
inputs.nixpkgs.follows = "nixpkgs";
|
||||
};
|
||||
|
||||
tpanel = {
|
||||
url = "github:tuxdotrs/tpanel";
|
||||
tshell = {
|
||||
url = "github:tuxdotrs/tshell";
|
||||
inputs.nixpkgs.follows = "nixpkgs";
|
||||
};
|
||||
|
||||
trok = {
|
||||
url = "github:tuxdotrs/trok";
|
||||
inputs.nixpkgs.follows = "nixpkgs";
|
||||
};
|
||||
|
||||
tfolio = {
|
||||
url = "git+ssh://git@github.com/tuxdotrs/tfolio.git";
|
||||
inputs.nixpkgs.follows = "nixpkgs";
|
||||
};
|
||||
|
||||
@@ -60,9 +70,7 @@
|
||||
};
|
||||
|
||||
nix-on-droid = {
|
||||
# @TODO: upstream module is broken for nixpkgs-unstable
|
||||
# url = "github:nix-community/nix-on-droid/release-24.05";
|
||||
url = "github:newAM/nix-on-droid/update-proot";
|
||||
url = "github:nix-community/nix-on-droid/master";
|
||||
inputs.nixpkgs.follows = "nixpkgs";
|
||||
inputs.home-manager.follows = "home-manager";
|
||||
};
|
||||
@@ -83,5 +91,9 @@
|
||||
lanzaboote.url = "github:nix-community/lanzaboote/v1.1.0";
|
||||
copyparty.url = "github:9001/copyparty";
|
||||
hermes-agent.url = "github:NousResearch/hermes-agent";
|
||||
voxtype.url = "github:peteonrails/voxtype/v0.7.5";
|
||||
opencode.url = "github:anomalyco/opencode";
|
||||
serpantinum.url = "github:ilyamiro/serpantinum";
|
||||
llm-agents.url = "github:numtide/llm-agents.nix";
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,32 +1,33 @@
|
||||
{ inputs, config, ... }:
|
||||
{
|
||||
flake.modules.nixOnDroid.core =
|
||||
{
|
||||
hostName,
|
||||
userName,
|
||||
userEmail,
|
||||
...
|
||||
}:
|
||||
{
|
||||
home-manager = {
|
||||
backupFileExtension = "bak";
|
||||
useGlobalPkgs = true;
|
||||
useUserPackages = true;
|
||||
extraSpecialArgs = {
|
||||
inherit
|
||||
inputs
|
||||
hostName
|
||||
userName
|
||||
userEmail
|
||||
;
|
||||
};
|
||||
inputs,
|
||||
config,
|
||||
...
|
||||
}: {
|
||||
flake.modules.nixOnDroid.core = {
|
||||
hostName,
|
||||
userName,
|
||||
userEmail,
|
||||
...
|
||||
}: {
|
||||
home-manager = {
|
||||
backupFileExtension = "bak";
|
||||
useGlobalPkgs = true;
|
||||
useUserPackages = true;
|
||||
extraSpecialArgs = {
|
||||
inherit
|
||||
inputs
|
||||
hostName
|
||||
userName
|
||||
userEmail
|
||||
;
|
||||
};
|
||||
|
||||
config = {
|
||||
imports = [
|
||||
config.flake.modules.homeManager.shell
|
||||
config.flake.modules.homeManager.${hostName}
|
||||
];
|
||||
};
|
||||
config = {
|
||||
imports = [
|
||||
config.flake.modules.homeManager.shell
|
||||
config.flake.modules.homeManager.${hostName}
|
||||
];
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,109 +1,106 @@
|
||||
{
|
||||
flake.modules.nixOnDroid.networking =
|
||||
{
|
||||
config,
|
||||
lib,
|
||||
pkgs,
|
||||
...
|
||||
}:
|
||||
let
|
||||
# utility functions
|
||||
concatLines = list: builtins.concatStringsSep "\n" list;
|
||||
flake.modules.nixOnDroid.networking = {
|
||||
config,
|
||||
lib,
|
||||
pkgs,
|
||||
...
|
||||
}: let
|
||||
# utility functions
|
||||
concatLines = list: builtins.concatStringsSep "\n" list;
|
||||
|
||||
prefixLines = mapper: list: concatLines (map mapper list);
|
||||
prefixLines = mapper: list: concatLines (map mapper list);
|
||||
|
||||
# could be put in the config
|
||||
configPath = "ssh/sshd_config";
|
||||
# could be put in the config
|
||||
configPath = "ssh/sshd_config";
|
||||
|
||||
keysFolder = "/etc/ssh";
|
||||
keysFolder = "/etc/ssh";
|
||||
|
||||
authorizedKeysFolder = "/etc/ssh/authorized_keys.d";
|
||||
authorizedKeysFolder = "/etc/ssh/authorized_keys.d";
|
||||
|
||||
supportedKeysTypes = [
|
||||
"rsa"
|
||||
"ed25519"
|
||||
];
|
||||
supportedKeysTypes = [
|
||||
"rsa"
|
||||
"ed25519"
|
||||
];
|
||||
|
||||
sshd-start-bin = "sshd-start";
|
||||
sshd-start-bin = "sshd-start";
|
||||
|
||||
# real config
|
||||
cfg = config.tnix.networking.openssh;
|
||||
# real config
|
||||
cfg = config.tnix.networking.openssh;
|
||||
|
||||
pathOfKeyOf = type: "${keysFolder}/ssh_host_${type}_key";
|
||||
pathOfKeyOf = type: "${keysFolder}/ssh_host_${type}_key";
|
||||
|
||||
generateKeyOf = type: ''
|
||||
${lib.getExe' pkgs.openssh "ssh-keygen"} \
|
||||
-t "${type}" \
|
||||
-f "${pathOfKeyOf type}" \
|
||||
-N ""
|
||||
generateKeyOf = type: ''
|
||||
${lib.getExe' pkgs.openssh "ssh-keygen"} \
|
||||
-t "${type}" \
|
||||
-f "${pathOfKeyOf type}" \
|
||||
-N ""
|
||||
'';
|
||||
|
||||
generateKeyWhenNeededOf = type: ''
|
||||
if [ ! -f ${pathOfKeyOf type} ]; then
|
||||
mkdir --parents ${keysFolder}
|
||||
${generateKeyOf type}
|
||||
fi
|
||||
'';
|
||||
|
||||
sshd-start = pkgs.writeScriptBin sshd-start-bin ''
|
||||
#!${pkgs.runtimeShell}
|
||||
${prefixLines generateKeyWhenNeededOf supportedKeysTypes}
|
||||
|
||||
mkdir --parents "${authorizedKeysFolder}"
|
||||
echo "${lib.concatStringsSep "\n" cfg.authorizedKeys}" > ${authorizedKeysFolder}/${config.user.userName}
|
||||
|
||||
echo "Starting sshd in non-daemonized way on port ${lib.concatMapStrings toString cfg.ports}"
|
||||
${lib.getExe' pkgs.openssh "sshd"} \
|
||||
-f "/etc/${configPath}" \
|
||||
-D # don't detach into a daemon process
|
||||
'';
|
||||
in {
|
||||
options.tnix.networking.openssh = {
|
||||
enable = lib.mkEnableOption ''
|
||||
Whether to enable the OpenSSH secure shell daemon, which
|
||||
allows secure remote logins.
|
||||
'';
|
||||
|
||||
generateKeyWhenNeededOf = type: ''
|
||||
if [ ! -f ${pathOfKeyOf type} ]; then
|
||||
mkdir --parents ${keysFolder}
|
||||
${generateKeyOf type}
|
||||
fi
|
||||
'';
|
||||
|
||||
sshd-start = pkgs.writeScriptBin sshd-start-bin ''
|
||||
#!${pkgs.runtimeShell}
|
||||
${prefixLines generateKeyWhenNeededOf supportedKeysTypes}
|
||||
|
||||
mkdir --parents "${authorizedKeysFolder}"
|
||||
echo "${lib.concatStringsSep "\n" cfg.authorizedKeys}" > ${authorizedKeysFolder}/${config.user.userName}
|
||||
|
||||
echo "Starting sshd in non-daemonized way on port ${lib.concatMapStrings toString cfg.ports}"
|
||||
${lib.getExe' pkgs.openssh "sshd"} \
|
||||
-f "/etc/${configPath}" \
|
||||
-D # don't detach into a daemon process
|
||||
'';
|
||||
in
|
||||
{
|
||||
options.tnix.networking.openssh = {
|
||||
enable = lib.mkEnableOption ''
|
||||
Whether to enable the OpenSSH secure shell daemon, which
|
||||
allows secure remote logins.
|
||||
ports = lib.mkOption {
|
||||
type = lib.types.listOf lib.types.port;
|
||||
default = [22];
|
||||
description = ''
|
||||
Specifies on which ports the SSH daemon listens.
|
||||
'';
|
||||
|
||||
ports = lib.mkOption {
|
||||
type = lib.types.listOf lib.types.port;
|
||||
default = [ 22 ];
|
||||
description = ''
|
||||
Specifies on which ports the SSH daemon listens.
|
||||
'';
|
||||
};
|
||||
|
||||
authorizedKeys = lib.mkOption {
|
||||
type = lib.types.listOf lib.types.str;
|
||||
default = [ ];
|
||||
description = ''
|
||||
Specify a list of public keys to be added to the authorized_keys file.
|
||||
'';
|
||||
};
|
||||
};
|
||||
|
||||
config = lib.mkIf cfg.enable {
|
||||
environment.etc = {
|
||||
"${configPath}".text = ''
|
||||
${prefixLines (port: "Port ${toString port}") cfg.ports}
|
||||
|
||||
AuthorizedKeysFile ${authorizedKeysFolder}/%u
|
||||
|
||||
LogLevel VERBOSE
|
||||
'';
|
||||
};
|
||||
|
||||
environment.packages = [
|
||||
sshd-start
|
||||
pkgs.openssh
|
||||
];
|
||||
|
||||
build.activationAfter.sshd = ''
|
||||
SERVER_PID=$(${lib.getExe' pkgs.procps "ps"} -a | ${lib.getExe' pkgs.toybox "grep"} sshd || true)
|
||||
if [ -z "$SERVER_PID" ]; then
|
||||
$DRY_RUN_CMD ${lib.getExe sshd-start}
|
||||
fi
|
||||
authorizedKeys = lib.mkOption {
|
||||
type = lib.types.listOf lib.types.str;
|
||||
default = [];
|
||||
description = ''
|
||||
Specify a list of public keys to be added to the authorized_keys file.
|
||||
'';
|
||||
};
|
||||
};
|
||||
|
||||
config = lib.mkIf cfg.enable {
|
||||
environment.etc = {
|
||||
"${configPath}".text = ''
|
||||
${prefixLines (port: "Port ${toString port}") cfg.ports}
|
||||
|
||||
AuthorizedKeysFile ${authorizedKeysFolder}/%u
|
||||
|
||||
LogLevel VERBOSE
|
||||
'';
|
||||
};
|
||||
|
||||
environment.packages = [
|
||||
sshd-start
|
||||
pkgs.openssh
|
||||
];
|
||||
|
||||
build.activationAfter.sshd = ''
|
||||
SERVER_PID=$(${lib.getExe' pkgs.procps "ps"} -a | ${lib.getExe' pkgs.toybox "grep"} sshd || true)
|
||||
if [ -z "$SERVER_PID" ]; then
|
||||
$DRY_RUN_CMD ${lib.getExe sshd-start}
|
||||
fi
|
||||
'';
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,4 +1,3 @@
|
||||
{ inputs, ... }:
|
||||
{
|
||||
imports = [ inputs.flake-parts.flakeModules.modules ];
|
||||
{inputs, ...}: {
|
||||
imports = [inputs.flake-parts.flakeModules.modules];
|
||||
}
|
||||
|
||||
@@ -3,19 +3,18 @@
|
||||
inputs,
|
||||
config,
|
||||
...
|
||||
}:
|
||||
let
|
||||
mkNixOSHost =
|
||||
hostName:
|
||||
{
|
||||
userName ? "tux",
|
||||
userEmail ? "t@tux.rs",
|
||||
system ? "x86_64-linux",
|
||||
unstable ? true,
|
||||
}:
|
||||
let
|
||||
nixpkgs = if unstable then inputs.nixpkgs else inputs.nixpkgs-stable;
|
||||
in
|
||||
}: let
|
||||
mkNixOSHost = hostName: {
|
||||
userName ? "tux",
|
||||
userEmail ? "t@tux.rs",
|
||||
system ? "x86_64-linux",
|
||||
unstable ? true,
|
||||
}: let
|
||||
nixpkgs =
|
||||
if unstable
|
||||
then inputs.nixpkgs
|
||||
else inputs.nixpkgs-stable;
|
||||
in
|
||||
nixpkgs.lib.nixosSystem {
|
||||
inherit system;
|
||||
specialArgs = {
|
||||
@@ -32,17 +31,17 @@ let
|
||||
];
|
||||
};
|
||||
|
||||
mkDroidHost =
|
||||
hostName:
|
||||
{
|
||||
userName ? "nix-on-droid",
|
||||
userEmail ? "t@tux.rs",
|
||||
system ? "aarch64-linux",
|
||||
unstable ? true,
|
||||
}:
|
||||
let
|
||||
nixpkgs = if unstable then inputs.nixpkgs else inputs.nixpkgs-stable;
|
||||
in
|
||||
mkDroidHost = hostName: {
|
||||
userName ? "nix-on-droid",
|
||||
userEmail ? "t@tux.rs",
|
||||
system ? "aarch64-linux",
|
||||
unstable ? true,
|
||||
}: let
|
||||
nixpkgs =
|
||||
if unstable
|
||||
then inputs.nixpkgs
|
||||
else inputs.nixpkgs-stable;
|
||||
in
|
||||
inputs.nix-on-droid.lib.nixOnDroidConfiguration {
|
||||
pkgs = import nixpkgs {
|
||||
inherit system;
|
||||
@@ -65,66 +64,55 @@ let
|
||||
];
|
||||
};
|
||||
|
||||
mkNixOSNode =
|
||||
hostName:
|
||||
{
|
||||
system ? "x86_64-linux",
|
||||
}:
|
||||
{
|
||||
hostname = hostName;
|
||||
profiles.system = {
|
||||
user = "root";
|
||||
path = inputs.deploy-rs.lib.${system}.activate.nixos self.nixosConfigurations.${hostName};
|
||||
};
|
||||
mkNixOSNode = hostName: {system ? "x86_64-linux"}: {
|
||||
hostname = hostName;
|
||||
profiles.system = {
|
||||
user = "root";
|
||||
path = inputs.deploy-rs.lib.${system}.activate.nixos self.nixosConfigurations.${hostName};
|
||||
};
|
||||
};
|
||||
|
||||
activateNixOnDroid =
|
||||
system: configuration:
|
||||
activateNixOnDroid = system: configuration:
|
||||
inputs.deploy-rs.lib.${system}.activate.custom configuration.activationPackage
|
||||
"${configuration.activationPackage}/activate";
|
||||
"${configuration.activationPackage}/activate";
|
||||
|
||||
mkDroidNode =
|
||||
hostName:
|
||||
{
|
||||
system ? "aarch64-linux",
|
||||
}:
|
||||
{
|
||||
hostname = hostName;
|
||||
profiles.system = {
|
||||
sshUser = "nix-on-droid";
|
||||
user = "nix-on-droid";
|
||||
magicRollback = true;
|
||||
sshOpts = [
|
||||
"-p"
|
||||
"8033"
|
||||
];
|
||||
path = activateNixOnDroid system self.nixOnDroidConfigurations.${hostName};
|
||||
};
|
||||
mkDroidNode = hostName: {system ? "aarch64-linux"}: {
|
||||
hostname = hostName;
|
||||
profiles.system = {
|
||||
sshUser = "nix-on-droid";
|
||||
user = "nix-on-droid";
|
||||
magicRollback = true;
|
||||
sshOpts = [
|
||||
"-p"
|
||||
"8033"
|
||||
];
|
||||
path = activateNixOnDroid system self.nixOnDroidConfigurations.${hostName};
|
||||
};
|
||||
|
||||
in
|
||||
{
|
||||
};
|
||||
in {
|
||||
flake = {
|
||||
nixosConfigurations = builtins.mapAttrs mkNixOSHost {
|
||||
sirius = { };
|
||||
canopus = { };
|
||||
arcturus = { };
|
||||
alpha = { };
|
||||
vps = { };
|
||||
sirius = {};
|
||||
canopus = {};
|
||||
arcturus = {};
|
||||
alpha = {};
|
||||
vps = {};
|
||||
};
|
||||
|
||||
nixOnDroidConfigurations = builtins.mapAttrs mkDroidHost {
|
||||
vega = { };
|
||||
vega = {};
|
||||
};
|
||||
|
||||
deploy.nodes =
|
||||
builtins.mapAttrs (hostName: _: mkNixOSNode hostName { }) self.nixosConfigurations
|
||||
// builtins.mapAttrs (hostName: _: mkDroidNode hostName { }) self.nixOnDroidConfigurations;
|
||||
builtins.mapAttrs (hostName: _: mkNixOSNode hostName {}) self.nixosConfigurations
|
||||
// builtins.mapAttrs (hostName: _: mkDroidNode hostName {}) self.nixOnDroidConfigurations;
|
||||
};
|
||||
|
||||
perSystem = {
|
||||
checks = builtins.mapAttrs (
|
||||
_: hostConfig: hostConfig.config.system.build.toplevel
|
||||
) self.nixosConfigurations;
|
||||
checks =
|
||||
builtins.mapAttrs (
|
||||
_: hostConfig: hostConfig.config.system.build.toplevel
|
||||
)
|
||||
self.nixosConfigurations;
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,20 +1,32 @@
|
||||
{
|
||||
inputs,
|
||||
...
|
||||
}:
|
||||
{
|
||||
{inputs, ...}: {
|
||||
flake.overlays = {
|
||||
modifications = final: prev: {
|
||||
omasnap = prev.callPackage ../../packages/omasnap.nix {};
|
||||
tnvim = inputs.tnvim.packages.${prev.stdenv.hostPlatform.system}.default;
|
||||
tpanel = inputs.tpanel.packages.${prev.stdenv.hostPlatform.system}.default;
|
||||
tshell = inputs.tshell.packages.${prev.stdenv.hostPlatform.system}.default;
|
||||
trok = inputs.trok.packages.${prev.stdenv.hostPlatform.system}.default;
|
||||
tfolio = inputs.tfolio.packages.${prev.stdenv.hostPlatform.system}.default;
|
||||
cyber-tux = inputs.cyber-tux.packages.${prev.stdenv.hostPlatform.system}.default;
|
||||
ags = inputs.tpanel.packages.${prev.stdenv.hostPlatform.system}.ags.default;
|
||||
wezterm-git = inputs.wezterm-flake.packages.${prev.stdenv.hostPlatform.system}.default;
|
||||
hyprland-git = inputs.hyprland.packages.${prev.stdenv.hostPlatform.system};
|
||||
awww = inputs.awww.packages.${prev.stdenv.hostPlatform.system}.awww;
|
||||
vicinae-extensions = inputs.vicinae-extensions.packages.${prev.stdenv.hostPlatform.system};
|
||||
voxtype = inputs.voxtype.packages.${prev.stdenv.hostPlatform.system};
|
||||
opencode-git = inputs.opencode.packages.${prev.stdenv.hostPlatform.system}.default;
|
||||
nix-index-small =
|
||||
inputs.nix-index-database.packages.${prev.stdenv.hostPlatform.system}.nix-index-with-small-db;
|
||||
|
||||
davinci-resolve = prev.davinci-resolve.override {
|
||||
runCommandLocal = name: env: cmd:
|
||||
if prev.lib.hasSuffix "-src.zip" name
|
||||
then
|
||||
prev.runCommandLocal name (env
|
||||
// {
|
||||
outputHash = "sha256-+3SB32EHpH9/0hM3h8CrO6f7V4ZAmxUFh3P8m6QDeO0=";
|
||||
})
|
||||
cmd
|
||||
else prev.runCommandLocal name env cmd;
|
||||
};
|
||||
};
|
||||
|
||||
stable-packages = final: _prev: {
|
||||
@@ -26,14 +38,17 @@
|
||||
|
||||
nur = inputs.nur.overlays.default;
|
||||
copyparty = inputs.copyparty.overlays.default;
|
||||
llm-agents = inputs.llm-agents.overlays.shared-nixpkgs;
|
||||
};
|
||||
|
||||
perSystem =
|
||||
{ system, ... }:
|
||||
{
|
||||
_module.args.pkgs = import inputs.nixpkgs {
|
||||
inherit system;
|
||||
overlays = builtins.attrValues inputs.self.overlays;
|
||||
};
|
||||
perSystem = {system, ...}: let
|
||||
pkgs = import inputs.nixpkgs {
|
||||
inherit system;
|
||||
overlays = builtins.attrValues inputs.self.overlays;
|
||||
};
|
||||
in {
|
||||
_module.args.pkgs = pkgs;
|
||||
|
||||
packages.omasnap = pkgs.omasnap;
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,5 +1,4 @@
|
||||
{ inputs, ... }:
|
||||
{
|
||||
{inputs, ...}: {
|
||||
imports = [
|
||||
inputs.treefmt-nix.flakeModule
|
||||
];
|
||||
@@ -9,7 +8,7 @@
|
||||
projectRootFile = "flake.nix";
|
||||
flakeCheck = true;
|
||||
programs = {
|
||||
nixfmt.enable = true;
|
||||
alejandra.enable = true;
|
||||
};
|
||||
};
|
||||
};
|
||||
|
||||
@@ -1,13 +1,11 @@
|
||||
{
|
||||
flake.modules.homeManager.core =
|
||||
{ userName, ... }:
|
||||
{
|
||||
programs.home-manager.enable = true;
|
||||
systemd.user.startServices = "sd-switch";
|
||||
flake.modules.homeManager.core = {userName, ...}: {
|
||||
programs.home-manager.enable = true;
|
||||
systemd.user.startServices = "sd-switch";
|
||||
|
||||
home = {
|
||||
username = "${userName}";
|
||||
homeDirectory = "/home/${userName}";
|
||||
};
|
||||
home = {
|
||||
username = "${userName}";
|
||||
homeDirectory = "/home/${userName}";
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,18 +1,15 @@
|
||||
{ inputs, ... }:
|
||||
{
|
||||
flake.modules.homeManager.core =
|
||||
{
|
||||
lib,
|
||||
osConfig ? { },
|
||||
...
|
||||
}:
|
||||
{
|
||||
nixpkgs = lib.mkIf (!(osConfig.home-manager.useGlobalPkgs or false)) {
|
||||
config = {
|
||||
allowUnfree = true;
|
||||
joypixels.acceptLicense = true;
|
||||
};
|
||||
overlays = builtins.attrValues inputs.self.overlays;
|
||||
{inputs, ...}: {
|
||||
flake.modules.homeManager.core = {
|
||||
lib,
|
||||
osConfig ? {},
|
||||
...
|
||||
}: {
|
||||
nixpkgs = lib.mkIf (!(osConfig.home-manager.useGlobalPkgs or false)) {
|
||||
config = {
|
||||
allowUnfree = true;
|
||||
joypixels.acceptLicense = true;
|
||||
};
|
||||
overlays = builtins.attrValues inputs.self.overlays;
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,38 +1,37 @@
|
||||
{
|
||||
flake.modules.homeManager.desktop =
|
||||
{
|
||||
pkgs,
|
||||
config,
|
||||
...
|
||||
}:
|
||||
let
|
||||
configDir = "${config.xdg.configHome}/BraveSoftware/Brave-Browser";
|
||||
flake.modules.homeManager.desktop = {
|
||||
pkgs,
|
||||
config,
|
||||
...
|
||||
}: let
|
||||
configDir = "${config.xdg.configHome}/BraveSoftware/Brave-Origin";
|
||||
|
||||
extensionJson = ext: {
|
||||
name = "${configDir}/External Extensions/${ext.id}.json";
|
||||
value.text = builtins.toJSON {
|
||||
external_update_url = "https://clients2.google.com/service/update2/crx";
|
||||
};
|
||||
extensionJson = ext: {
|
||||
name = "${configDir}/External Extensions/${ext.id}.json";
|
||||
value.text = builtins.toJSON {
|
||||
external_update_url = "https://clients2.google.com/service/update2/crx";
|
||||
};
|
||||
|
||||
extensions = [
|
||||
{ id = "nkbihfbeogaeaoehlefnkodbefgpgknn"; } # Metamask
|
||||
{ id = "gppongmhjkpfnbhagpmjfkannfbllamg"; } # Wappalyzer
|
||||
{ id = "nngceckbapebfimnlniiiahkandclblb"; } # Bitwarden
|
||||
{ id = "bfnaelmomeimhlpmgjnjophhpkkoljpa"; } # Phantom
|
||||
{ id = "eimadpbcbfnmbkopoojfekhnkhdbieeh"; } # DarkReader
|
||||
];
|
||||
in
|
||||
{
|
||||
programs.chromium = {
|
||||
enable = true;
|
||||
package = pkgs.brave;
|
||||
commandLineArgs = [
|
||||
"--disable-features=WebRtcAllowInputVolumeAdjustment"
|
||||
"--force-device-scale-factor=1.0"
|
||||
];
|
||||
};
|
||||
|
||||
home.file = builtins.listToAttrs (map extensionJson extensions);
|
||||
};
|
||||
|
||||
extensions = [
|
||||
{id = "nkbihfbeogaeaoehlefnkodbefgpgknn";} # Metamask
|
||||
{id = "gppongmhjkpfnbhagpmjfkannfbllamg";} # Wappalyzer
|
||||
{id = "nngceckbapebfimnlniiiahkandclblb";} # Bitwarden
|
||||
{id = "bfnaelmomeimhlpmgjnjophhpkkoljpa";} # Phantom
|
||||
{id = "eimadpbcbfnmbkopoojfekhnkhdbieeh";} # DarkReader
|
||||
];
|
||||
in {
|
||||
programs.chromium = {
|
||||
enable = true;
|
||||
package = pkgs.brave-origin;
|
||||
commandLineArgs = [
|
||||
"--disable-features=WebRtcAllowInputVolumeAdjustment"
|
||||
"--force-device-scale-factor=1.0"
|
||||
];
|
||||
};
|
||||
|
||||
home.packages = [pkgs.brave];
|
||||
|
||||
home.file = builtins.listToAttrs (map extensionJson extensions);
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,45 +1,58 @@
|
||||
{
|
||||
flake.modules.homeManager.desktop =
|
||||
{ inputs, userName, ... }:
|
||||
{
|
||||
imports = [
|
||||
inputs.nixcord.homeModules.nixcord
|
||||
];
|
||||
flake.modules.homeManager.desktop = {
|
||||
inputs,
|
||||
userName,
|
||||
...
|
||||
}: {
|
||||
imports = [
|
||||
inputs.nixcord.homeModules.nixcord
|
||||
];
|
||||
|
||||
programs.nixcord = {
|
||||
enable = true;
|
||||
user = userName;
|
||||
discord.enable = false;
|
||||
vesktop.enable = true;
|
||||
config = {
|
||||
themeLinks = [
|
||||
"https://raw.githubusercontent.com/refact0r/system24/refs/heads/main/archive/flavors/spotify-text.theme.css"
|
||||
];
|
||||
frameless = true;
|
||||
plugins = {
|
||||
hideMedia.enable = true;
|
||||
ignoreActivities = {
|
||||
enable = true;
|
||||
ignorePlaying = true;
|
||||
ignoreWatching = true;
|
||||
};
|
||||
programs.nixcord = {
|
||||
enable = true;
|
||||
user = userName;
|
||||
discord.enable = false;
|
||||
vesktop.enable = true;
|
||||
config = {
|
||||
themeLinks = [
|
||||
"https://raw.githubusercontent.com/refact0r/system24/refs/heads/main/archive/flavors/spotify-text.theme.css"
|
||||
];
|
||||
frameless = true;
|
||||
plugins = {
|
||||
hideMedia.enable = true;
|
||||
anonymiseFileNames.enable = true;
|
||||
copyFileContents.enable = true;
|
||||
noTypingAnimation.enable = true;
|
||||
readAllNotificationsButton.enable = true;
|
||||
silentTyping.enable = true;
|
||||
validUser.enable = true;
|
||||
biggerStreamPreview.enable = true;
|
||||
ignoreActivities = {
|
||||
enable = true;
|
||||
ignorePlaying = true;
|
||||
ignoreWatching = true;
|
||||
};
|
||||
sortFriendRequests = {
|
||||
enable = true;
|
||||
showDates = true;
|
||||
};
|
||||
};
|
||||
dorion = {
|
||||
theme = "dark";
|
||||
zoom = "1.1";
|
||||
blur = "acrylic";
|
||||
sysTray = true;
|
||||
openOnStartup = true;
|
||||
autoClearCache = true;
|
||||
disableHardwareAccel = false;
|
||||
rpcServer = true;
|
||||
rpcProcessScanner = true;
|
||||
pushToTalk = true;
|
||||
pushToTalkKeys = [ "RControl" ];
|
||||
desktopNotifications = true;
|
||||
unreadBadge = true;
|
||||
};
|
||||
};
|
||||
dorion = {
|
||||
theme = "dark";
|
||||
zoom = "1.1";
|
||||
blur = "acrylic";
|
||||
sysTray = true;
|
||||
openOnStartup = true;
|
||||
autoClearCache = true;
|
||||
disableHardwareAccel = false;
|
||||
rpcServer = true;
|
||||
rpcProcessScanner = true;
|
||||
pushToTalk = true;
|
||||
pushToTalkKeys = ["RControl"];
|
||||
desktopNotifications = true;
|
||||
unreadBadge = true;
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,75 +1,73 @@
|
||||
{
|
||||
flake.modules.homeManager.desktop =
|
||||
{
|
||||
pkgs,
|
||||
userName,
|
||||
...
|
||||
}:
|
||||
{
|
||||
programs.firefox = {
|
||||
enable = true;
|
||||
flake.modules.homeManager.desktop = {
|
||||
pkgs,
|
||||
userName,
|
||||
...
|
||||
}: {
|
||||
programs.firefox = {
|
||||
enable = true;
|
||||
|
||||
package = pkgs.firefox.override {
|
||||
extraPolicies = {
|
||||
CaptivePortal = false;
|
||||
DisableFirefoxStudies = true;
|
||||
DisablePocket = true;
|
||||
DisableTelemetry = true;
|
||||
DisableFirefoxAccounts = false;
|
||||
NoDefaultBookmarks = true;
|
||||
OfferToSaveLogins = false;
|
||||
OfferToSaveLoginsDefault = false;
|
||||
PasswordManagerEnabled = false;
|
||||
FirefoxHome = {
|
||||
Search = true;
|
||||
Pocket = false;
|
||||
Snippets = false;
|
||||
TopSites = false;
|
||||
Highlights = false;
|
||||
};
|
||||
UserMessaging = {
|
||||
ExtensionRecommendations = false;
|
||||
SkipOnboarding = true;
|
||||
};
|
||||
package = pkgs.firefox.override {
|
||||
extraPolicies = {
|
||||
CaptivePortal = false;
|
||||
DisableFirefoxStudies = true;
|
||||
DisablePocket = true;
|
||||
DisableTelemetry = true;
|
||||
DisableFirefoxAccounts = false;
|
||||
NoDefaultBookmarks = true;
|
||||
OfferToSaveLogins = false;
|
||||
OfferToSaveLoginsDefault = false;
|
||||
PasswordManagerEnabled = false;
|
||||
FirefoxHome = {
|
||||
Search = true;
|
||||
Pocket = false;
|
||||
Snippets = false;
|
||||
TopSites = false;
|
||||
Highlights = false;
|
||||
};
|
||||
};
|
||||
|
||||
profiles = {
|
||||
${userName} = {
|
||||
id = 0;
|
||||
name = "tux";
|
||||
search = {
|
||||
force = true;
|
||||
default = "google";
|
||||
};
|
||||
settings = {
|
||||
"general.smoothScroll" = true;
|
||||
"extensions.activeThemeID" = "firefox-compact-dark@mozilla.org";
|
||||
"layout.css.prefers-color-scheme.content-override" = 0;
|
||||
"browser.compactmode.show" = true;
|
||||
"browser.tabs.firefox-view" = false;
|
||||
"browser.bookmarks.addedImportButton" = false;
|
||||
"extensions.pocket.enabled" = false;
|
||||
"browser.fullscreen.autohide" = false;
|
||||
};
|
||||
extraConfig = ''
|
||||
user_pref("toolkit.legacyUserProfileCustomizations.stylesheets", true);
|
||||
user_pref("full-screen-api.ignore-widgets", true);
|
||||
user_pref("media.ffmpeg.vaapi.enabled", true);
|
||||
user_pref("media.rdd-vpx.enabled", true);
|
||||
'';
|
||||
|
||||
extensions.packages = with pkgs.nur.repos.rycee.firefox-addons; [
|
||||
ublock-origin
|
||||
facebook-container
|
||||
metamask
|
||||
darkreader
|
||||
bitwarden
|
||||
wappalyzer
|
||||
clearurls
|
||||
];
|
||||
UserMessaging = {
|
||||
ExtensionRecommendations = false;
|
||||
SkipOnboarding = true;
|
||||
};
|
||||
};
|
||||
};
|
||||
|
||||
profiles = {
|
||||
${userName} = {
|
||||
id = 0;
|
||||
name = "tux";
|
||||
search = {
|
||||
force = true;
|
||||
default = "google";
|
||||
};
|
||||
settings = {
|
||||
"general.smoothScroll" = true;
|
||||
"extensions.activeThemeID" = "firefox-compact-dark@mozilla.org";
|
||||
"layout.css.prefers-color-scheme.content-override" = 0;
|
||||
"browser.compactmode.show" = true;
|
||||
"browser.tabs.firefox-view" = false;
|
||||
"browser.bookmarks.addedImportButton" = false;
|
||||
"extensions.pocket.enabled" = false;
|
||||
"browser.fullscreen.autohide" = false;
|
||||
};
|
||||
extraConfig = ''
|
||||
user_pref("toolkit.legacyUserProfileCustomizations.stylesheets", true);
|
||||
user_pref("full-screen-api.ignore-widgets", true);
|
||||
user_pref("media.ffmpeg.vaapi.enabled", true);
|
||||
user_pref("media.rdd-vpx.enabled", true);
|
||||
'';
|
||||
|
||||
extensions.packages = with pkgs.nur.repos.rycee.firefox-addons; [
|
||||
ublock-origin
|
||||
facebook-container
|
||||
metamask
|
||||
darkreader
|
||||
bitwarden
|
||||
wappalyzer
|
||||
clearurls
|
||||
];
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -13,6 +13,8 @@
|
||||
font-size = 12;
|
||||
font-family = "JetBrainsMono Nerd Font";
|
||||
theme = "poimandres";
|
||||
custom-shader = "shaders/cursor_warp.glsl";
|
||||
custom-shader-animation = "always";
|
||||
};
|
||||
|
||||
themes = {
|
||||
|
||||
@@ -1,40 +1,43 @@
|
||||
{
|
||||
flake.modules.homeManager.desktop =
|
||||
{ config, pkgs, ... }:
|
||||
{
|
||||
# TODO: Hyprland 0.55 switched to Lua-based configuration.
|
||||
# Until the Home Manager module is updated, we symlink our config instead.
|
||||
|
||||
# wayland.windowManager.hyprland = {
|
||||
# enable = true;
|
||||
# package = null;
|
||||
# portalPackage = null;
|
||||
# xwayland.enable = true;
|
||||
# systemd.variables = [ "--all" ];
|
||||
# };
|
||||
|
||||
home.file = {
|
||||
".config/hypr/config".source =
|
||||
config.lib.file.mkOutOfStoreSymlink "${config.home.homeDirectory}/Projects/hypr/config";
|
||||
".config/hypr/hyprland.lua".source =
|
||||
config.lib.file.mkOutOfStoreSymlink "${config.home.homeDirectory}/Projects/hypr/hyprland.lua";
|
||||
};
|
||||
|
||||
home.packages = with pkgs; [
|
||||
ags
|
||||
awww
|
||||
grim
|
||||
slurp
|
||||
hyprshot
|
||||
wl-clipboard
|
||||
wl-screenrec
|
||||
(writeShellScriptBin "hypr-screenshot" ''
|
||||
hyprshot -m region -r ppm - | satty --filename -
|
||||
'')
|
||||
|
||||
(writeShellScriptBin "hypr-screenrecord" ''
|
||||
wl-screenrec -g "$(slurp)"
|
||||
'')
|
||||
];
|
||||
flake.modules.homeManager.desktop = {
|
||||
config,
|
||||
pkgs,
|
||||
...
|
||||
}: {
|
||||
# TODO: Hyprland 0.55 switched to Lua-based configuration.
|
||||
# HM module is updated but I'm too lazy at this point so we symlink our config instead.
|
||||
wayland.windowManager.hyprland = {
|
||||
enable = true;
|
||||
package = null;
|
||||
portalPackage = null;
|
||||
xwayland.enable = true;
|
||||
configType = "hyprlang";
|
||||
systemd.variables = ["--all"];
|
||||
};
|
||||
|
||||
home.file = {
|
||||
".config/hypr/config".source =
|
||||
config.lib.file.mkOutOfStoreSymlink "${config.home.homeDirectory}/Projects/hypr/config";
|
||||
".config/hypr/hyprland.lua".source =
|
||||
config.lib.file.mkOutOfStoreSymlink "${config.home.homeDirectory}/Projects/hypr/hyprland.lua";
|
||||
};
|
||||
|
||||
home.packages = with pkgs; [
|
||||
ags
|
||||
awww
|
||||
grim
|
||||
slurp
|
||||
hyprshot
|
||||
wl-clipboard
|
||||
wl-screenrec
|
||||
omasnap
|
||||
(writeShellScriptBin "hypr-screenshot" ''
|
||||
hyprshot -m region -r ppm - | satty --filename -
|
||||
'')
|
||||
|
||||
(writeShellScriptBin "hypr-screenrecord" ''
|
||||
wl-screenrec -g "$(slurp)"
|
||||
'')
|
||||
];
|
||||
};
|
||||
}
|
||||
|
||||
86
modules/hm/desktop/kitty.nix
Normal file
86
modules/hm/desktop/kitty.nix
Normal file
@@ -0,0 +1,86 @@
|
||||
{
|
||||
flake.modules.homeManager.desktop = {pkgs, ...}: {
|
||||
programs.kitty = {
|
||||
enable = true;
|
||||
package = pkgs.kitty;
|
||||
|
||||
font = {
|
||||
name = "JetBrainsMono Nerd Font";
|
||||
size = 12.0;
|
||||
};
|
||||
|
||||
shellIntegration.enableZshIntegration = true;
|
||||
|
||||
settings = {
|
||||
background_opacity = "1.0";
|
||||
|
||||
enable_audio_bell = false;
|
||||
confirm_os_window_close = 0;
|
||||
|
||||
cursor_trail = 3;
|
||||
|
||||
# Window
|
||||
window_padding_width = 10;
|
||||
|
||||
foreground = "#f1f1f1";
|
||||
background = "#0f0f0f";
|
||||
|
||||
# Borders
|
||||
active_border_color = "#3d59a1";
|
||||
inactive_border_color = "#101014";
|
||||
bell_border_color = "#fffac2";
|
||||
|
||||
# Colors
|
||||
color0 = "#0f0f0f";
|
||||
color8 = "#a6accd";
|
||||
|
||||
color1 = "#d0679d";
|
||||
color9 = "#d0679d";
|
||||
|
||||
color2 = "#5de4c7";
|
||||
color10 = "#5de4c7";
|
||||
|
||||
color3 = "#fffac2";
|
||||
color11 = "#fffac2";
|
||||
|
||||
color4 = "#89ddff";
|
||||
color12 = "#add7ff";
|
||||
|
||||
color5 = "#fcc5e9";
|
||||
color13 = "#fae4fc";
|
||||
|
||||
color6 = "#add7ff";
|
||||
color14 = "#89ddff";
|
||||
|
||||
color7 = "#ffffff";
|
||||
color15 = "#ffffff";
|
||||
|
||||
# Cursor
|
||||
cursor = "#ffffff";
|
||||
cursor_text_color = "#0f0f0f";
|
||||
|
||||
# Selection
|
||||
selection_foreground = "none";
|
||||
selection_background = "#28344a";
|
||||
|
||||
# URLs
|
||||
url_color = "#5de4c7";
|
||||
|
||||
# Tab bar
|
||||
tab_bar_edge = "bottom";
|
||||
tab_bar_style = "fade";
|
||||
tab_fade = "1";
|
||||
|
||||
active_tab_foreground = "#3d59a1";
|
||||
active_tab_background = "#16161e";
|
||||
active_tab_font_style = "bold";
|
||||
|
||||
inactive_tab_foreground = "#787c99";
|
||||
inactive_tab_background = "#16161e";
|
||||
inactive_tab_font_style = "bold";
|
||||
|
||||
tab_bar_background = "#101014";
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
@@ -1,25 +1,21 @@
|
||||
{ inputs, ... }:
|
||||
{
|
||||
flake.modules.homeManager.desktop =
|
||||
{
|
||||
config,
|
||||
pkgs,
|
||||
lib,
|
||||
...
|
||||
}:
|
||||
with lib;
|
||||
let
|
||||
{inputs, ...}: {
|
||||
flake.modules.homeManager.desktop = {
|
||||
config,
|
||||
pkgs,
|
||||
lib,
|
||||
...
|
||||
}:
|
||||
with lib; let
|
||||
cfg = config.tnix.services.lan-mouse;
|
||||
in
|
||||
{
|
||||
imports = [ inputs.lan-mouse.homeManagerModules.default ];
|
||||
in {
|
||||
imports = [inputs.lan-mouse.homeManagerModules.default];
|
||||
|
||||
options.tnix.services.lan-mouse = {
|
||||
enable = mkEnableOption "Enable Lan-Mouse";
|
||||
|
||||
settings = mkOption {
|
||||
type = (pkgs.formats.toml { }).type;
|
||||
default = { };
|
||||
type = (pkgs.formats.toml {}).type;
|
||||
default = {};
|
||||
description = ''
|
||||
TOML configuration for lan-mouse.
|
||||
See <https://github.com/feschber/lan-mouse/> for available options.
|
||||
@@ -28,7 +24,6 @@
|
||||
};
|
||||
|
||||
config = mkIf cfg.enable {
|
||||
|
||||
programs.lan-mouse = {
|
||||
enable = true;
|
||||
systemd = true;
|
||||
|
||||
@@ -1,17 +1,13 @@
|
||||
{ inputs, ... }:
|
||||
{
|
||||
flake.modules.homeManager.desktop =
|
||||
{
|
||||
config,
|
||||
pkgs,
|
||||
lib,
|
||||
...
|
||||
}:
|
||||
with lib;
|
||||
let
|
||||
{inputs, ...}: {
|
||||
flake.modules.homeManager.desktop = {
|
||||
config,
|
||||
pkgs,
|
||||
lib,
|
||||
...
|
||||
}:
|
||||
with lib; let
|
||||
cfg = config.tnix.desktop.mangowm;
|
||||
in
|
||||
{
|
||||
in {
|
||||
imports = [
|
||||
inputs.mango.hmModules.mango
|
||||
];
|
||||
@@ -21,12 +17,12 @@
|
||||
|
||||
monitorRule = mkOption {
|
||||
type = with types; listOf str;
|
||||
default = [ ];
|
||||
default = [];
|
||||
};
|
||||
|
||||
tagRule = mkOption {
|
||||
type = with types; listOf str;
|
||||
default = [ ];
|
||||
default = [];
|
||||
};
|
||||
};
|
||||
|
||||
|
||||
@@ -1,24 +1,21 @@
|
||||
{
|
||||
flake.modules.homeManager.desktop =
|
||||
{ pkgs, ... }:
|
||||
{
|
||||
programs.mpv = {
|
||||
enable = true;
|
||||
flake.modules.homeManager.desktop = {pkgs, ...}: {
|
||||
programs.mpv = {
|
||||
enable = true;
|
||||
|
||||
scripts = (
|
||||
with pkgs.mpvScripts;
|
||||
[
|
||||
modernz
|
||||
thumbfast
|
||||
mpris
|
||||
mpv-image-viewer.image-positioning
|
||||
]
|
||||
);
|
||||
scripts = (
|
||||
with pkgs.mpvScripts; [
|
||||
modernz
|
||||
thumbfast
|
||||
mpris
|
||||
mpv-image-viewer.image-positioning
|
||||
]
|
||||
);
|
||||
|
||||
config = {
|
||||
osc = "no";
|
||||
border = "no";
|
||||
};
|
||||
config = {
|
||||
osc = "no";
|
||||
border = "no";
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
77
modules/hm/desktop/serpantinum.nix
Normal file
77
modules/hm/desktop/serpantinum.nix
Normal file
@@ -0,0 +1,77 @@
|
||||
{inputs, ...}: {
|
||||
flake.modules.nixos.desktop = {
|
||||
imports = [
|
||||
inputs.serpantinum.nixosModules.default
|
||||
];
|
||||
|
||||
programs.serpantinum.enable = true;
|
||||
};
|
||||
|
||||
flake.modules.homeManager.desktop = {pkgs, ...}: {
|
||||
imports = [
|
||||
inputs.serpantinum.homeManagerModules.default
|
||||
];
|
||||
|
||||
home.packages = with pkgs; [pulseaudioFull];
|
||||
|
||||
programs.serpantinum = {
|
||||
enable = true;
|
||||
systemd.enable = true;
|
||||
|
||||
settings = {
|
||||
wallpaperDir = "/home/tux/Wallpapers";
|
||||
|
||||
general = {
|
||||
language = "en";
|
||||
weatherUnit = "metric";
|
||||
weatherInterval = 30;
|
||||
avatarPath = "/home/tux/Wallpapers/tux.png";
|
||||
muteSfx = true;
|
||||
};
|
||||
|
||||
bar = {
|
||||
position = "top";
|
||||
style = "modular";
|
||||
time = {
|
||||
format = "hh:mm:ss A";
|
||||
};
|
||||
width = 5;
|
||||
workspaceCount = 7;
|
||||
modules = {
|
||||
left = [
|
||||
"left"
|
||||
"workspaces"
|
||||
"sysmon"
|
||||
"wifi"
|
||||
];
|
||||
center = ["vis"];
|
||||
right = [
|
||||
"media"
|
||||
"vol"
|
||||
"bat"
|
||||
"tray"
|
||||
"timedate"
|
||||
];
|
||||
};
|
||||
};
|
||||
|
||||
theme = {
|
||||
fontFamily = "JetBrains Mono SemiBold";
|
||||
borderRadius = 12;
|
||||
matugen = true;
|
||||
};
|
||||
|
||||
notifications = {
|
||||
dnd = false;
|
||||
position = "top right";
|
||||
sound = true;
|
||||
};
|
||||
|
||||
idle = {
|
||||
enabled = true;
|
||||
manualInhibit = true;
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
@@ -1,32 +1,30 @@
|
||||
{
|
||||
flake.modules.homeManager.desktop =
|
||||
{ pkgs, ... }:
|
||||
{
|
||||
home.pointerCursor = {
|
||||
enable = true;
|
||||
package = pkgs.bibata-cursors;
|
||||
name = "Bibata-Modern-Ice";
|
||||
size = 28;
|
||||
};
|
||||
|
||||
qt = {
|
||||
enable = true;
|
||||
style.name = "adwaita-dark";
|
||||
};
|
||||
|
||||
gtk = {
|
||||
enable = true;
|
||||
theme = {
|
||||
name = "adw-gtk3-dark";
|
||||
package = pkgs.adw-gtk3;
|
||||
};
|
||||
iconTheme = {
|
||||
package = pkgs.tela-icon-theme;
|
||||
name = "Tela-black";
|
||||
};
|
||||
};
|
||||
|
||||
# Make GTK4/libadwaita apps prefer dark too (they ignore gtk.theme).
|
||||
dconf.settings."org/gnome/desktop/interface".color-scheme = "prefer-dark";
|
||||
flake.modules.homeManager.desktop = {pkgs, ...}: {
|
||||
home.pointerCursor = {
|
||||
enable = true;
|
||||
package = pkgs.bibata-cursors;
|
||||
name = "Bibata-Modern-Ice";
|
||||
size = 24;
|
||||
};
|
||||
|
||||
qt = {
|
||||
enable = true;
|
||||
style.name = "adwaita-dark";
|
||||
};
|
||||
|
||||
gtk = {
|
||||
enable = true;
|
||||
theme = {
|
||||
name = "adw-gtk3-dark";
|
||||
package = pkgs.adw-gtk3;
|
||||
};
|
||||
iconTheme = {
|
||||
package = pkgs.tela-icon-theme;
|
||||
name = "Tela-black";
|
||||
};
|
||||
};
|
||||
|
||||
# Make GTK4/libadwaita apps prefer dark too (they ignore gtk.theme).
|
||||
dconf.settings."org/gnome/desktop/interface".color-scheme = "prefer-dark";
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,69 +1,60 @@
|
||||
{
|
||||
flake.modules.homeManager.desktop =
|
||||
{
|
||||
pkgs,
|
||||
...
|
||||
}:
|
||||
{
|
||||
programs.vicinae = {
|
||||
flake.modules.homeManager.desktop = {pkgs, ...}: {
|
||||
programs.vicinae = {
|
||||
enable = true;
|
||||
systemd = {
|
||||
enable = true;
|
||||
systemd = {
|
||||
enable = true;
|
||||
autoStart = true;
|
||||
autoStart = true;
|
||||
};
|
||||
useLayerShell = true;
|
||||
|
||||
extensions = with pkgs.vicinae-extensions; [
|
||||
nix
|
||||
ssh
|
||||
awww-switcher
|
||||
process-manager
|
||||
pulseaudio
|
||||
port-killer
|
||||
];
|
||||
|
||||
settings = {
|
||||
close_on_focus_loss = false;
|
||||
consider_preedit = true;
|
||||
pop_to_root_on_close = true;
|
||||
favicon_service = "twenty";
|
||||
search_files_in_root = true;
|
||||
font = {
|
||||
normal = {
|
||||
size = 10;
|
||||
family = "JetBrainsMono Nerd Font";
|
||||
};
|
||||
};
|
||||
useLayerShell = true;
|
||||
|
||||
extensions = with pkgs.vicinae-extensions; [
|
||||
# @TODO broken in upstream repo
|
||||
# bluetooth
|
||||
nix
|
||||
ssh
|
||||
awww-switcher
|
||||
process-manager
|
||||
pulseaudio
|
||||
wifi-commander
|
||||
port-killer
|
||||
silverbullet
|
||||
];
|
||||
|
||||
settings = {
|
||||
close_on_focus_loss = true;
|
||||
consider_preedit = true;
|
||||
pop_to_root_on_close = true;
|
||||
favicon_service = "twenty";
|
||||
search_files_in_root = true;
|
||||
font = {
|
||||
normal = {
|
||||
size = 10;
|
||||
family = "JetBrainsMono Nerd Font";
|
||||
};
|
||||
theme = {
|
||||
light = {
|
||||
name = "vicinae-light";
|
||||
icon_theme = "default";
|
||||
};
|
||||
theme = {
|
||||
light = {
|
||||
name = "vicinae-light";
|
||||
icon_theme = "default";
|
||||
};
|
||||
dark = {
|
||||
name = "vicinae-dark";
|
||||
icon_theme = "default";
|
||||
};
|
||||
};
|
||||
launcher_window = {
|
||||
opacity = 0.98;
|
||||
dark = {
|
||||
name = "vicinae-dark";
|
||||
icon_theme = "default";
|
||||
};
|
||||
};
|
||||
launcher_window = {
|
||||
opacity = 0.98;
|
||||
};
|
||||
|
||||
imports = [ "/run/secrets/vicinae.json" ];
|
||||
imports = ["/run/secrets/vicinae.json"];
|
||||
|
||||
providers = {
|
||||
"@sovereign/vicinae-extension-awww-switcher-0" = {
|
||||
"preferences" = {
|
||||
"transitionDuration" = "1";
|
||||
"transitionType" = "center";
|
||||
"wallpaperPath" = "/home/tux/Wallpapers/";
|
||||
};
|
||||
providers = {
|
||||
"@sovereign/vicinae-extension-awww-switcher-0" = {
|
||||
"preferences" = {
|
||||
"transitionDuration" = "1";
|
||||
"transitionType" = "center";
|
||||
"wallpaperPath" = "/home/tux/Wallpapers/";
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
26
modules/hm/desktop/voxtype.nix
Normal file
26
modules/hm/desktop/voxtype.nix
Normal file
@@ -0,0 +1,26 @@
|
||||
{inputs, ...}: {
|
||||
flake.modules.homeManager.desktop = {pkgs, ...}: {
|
||||
imports = [
|
||||
inputs.voxtype.homeManagerModules.default
|
||||
];
|
||||
|
||||
programs.voxtype = {
|
||||
enable = true;
|
||||
package = pkgs.voxtype.onnx-cuda;
|
||||
engine = "parakeet";
|
||||
model.path = "/home/tux/.local/share/voxtype/models/parakeet-tdt-0.6b-v3";
|
||||
service.enable = true;
|
||||
settings = {
|
||||
hotkey.enabled = false;
|
||||
whisper = {
|
||||
language = "en";
|
||||
on_demand_loading = true;
|
||||
};
|
||||
|
||||
parakeet = {
|
||||
on_demand_loading = true;
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
@@ -1,33 +1,31 @@
|
||||
{
|
||||
flake.modules.homeManager.desktop =
|
||||
{ pkgs, ... }:
|
||||
{
|
||||
programs.wezterm = {
|
||||
enable = true;
|
||||
package = pkgs.wezterm-git;
|
||||
enableZshIntegration = false;
|
||||
flake.modules.homeManager.desktop = {pkgs, ...}: {
|
||||
programs.wezterm = {
|
||||
enable = true;
|
||||
package = pkgs.wezterm-git;
|
||||
enableZshIntegration = false;
|
||||
|
||||
extraConfig = ''
|
||||
local wezterm = require 'wezterm'
|
||||
local config = {}
|
||||
extraConfig = ''
|
||||
local wezterm = require 'wezterm'
|
||||
local config = {}
|
||||
|
||||
config.check_for_updates = false
|
||||
config.check_for_updates = false
|
||||
|
||||
config.window_close_confirmation = 'NeverPrompt'
|
||||
config.color_scheme = 'Poimandres'
|
||||
config.colors = {
|
||||
background = "#0f0f0f"
|
||||
}
|
||||
config.enable_tab_bar = false
|
||||
config.font = wezterm.font_with_fallback {
|
||||
'JetBrainsMono Nerd Font',
|
||||
}
|
||||
config.font_size = 12.0
|
||||
config.window_background_opacity = 1
|
||||
config.audible_bell = "Disabled"
|
||||
config.window_close_confirmation = 'NeverPrompt'
|
||||
config.color_scheme = 'Poimandres'
|
||||
config.colors = {
|
||||
background = "#0f0f0f"
|
||||
}
|
||||
config.enable_tab_bar = false
|
||||
config.font = wezterm.font_with_fallback {
|
||||
'JetBrainsMono Nerd Font',
|
||||
}
|
||||
config.font_size = 12.0
|
||||
config.window_background_opacity = 1
|
||||
config.audible_bell = "Disabled"
|
||||
|
||||
return config
|
||||
'';
|
||||
};
|
||||
return config
|
||||
'';
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -29,6 +29,25 @@
|
||||
diagnostics = false;
|
||||
metrics = false;
|
||||
};
|
||||
|
||||
agent = {
|
||||
dock = "right";
|
||||
favorite_models = [];
|
||||
model_parameters = [];
|
||||
};
|
||||
|
||||
collaboration_panel = {
|
||||
button = false;
|
||||
};
|
||||
|
||||
agent_servers = {
|
||||
opencode = {
|
||||
default_config_options = {
|
||||
model = "opencode-go/deepseek-v4.1-flash";
|
||||
};
|
||||
type = "registry";
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
|
||||
8
modules/hm/gaming/lutris.nix
Normal file
8
modules/hm/gaming/lutris.nix
Normal file
@@ -0,0 +1,8 @@
|
||||
{
|
||||
flake.modules.homeManager.desktop = {osConfig, ...}: {
|
||||
programs.lutris = {
|
||||
enable = true;
|
||||
steamPackage = osConfig.programs.steam.package;
|
||||
};
|
||||
};
|
||||
}
|
||||
@@ -1,27 +1,25 @@
|
||||
{
|
||||
flake.modules.homeManager.shell =
|
||||
{
|
||||
userName,
|
||||
userEmail,
|
||||
...
|
||||
}:
|
||||
{
|
||||
programs.git = {
|
||||
enable = true;
|
||||
signing = {
|
||||
key = "~/.ssh/id_ed25519.pub";
|
||||
signByDefault = true;
|
||||
};
|
||||
lfs.enable = true;
|
||||
settings = {
|
||||
user = {
|
||||
name = "${userName}";
|
||||
email = "${userEmail}";
|
||||
};
|
||||
init.defaultBranch = "main";
|
||||
commit.gpgSign = true;
|
||||
gpg.format = "ssh";
|
||||
flake.modules.homeManager.shell = {
|
||||
userName,
|
||||
userEmail,
|
||||
...
|
||||
}: {
|
||||
programs.git = {
|
||||
enable = true;
|
||||
signing = {
|
||||
key = "~/.ssh/id_ed25519.pub";
|
||||
signByDefault = true;
|
||||
};
|
||||
lfs.enable = true;
|
||||
settings = {
|
||||
user = {
|
||||
name = "${userName}";
|
||||
email = "${userEmail}";
|
||||
};
|
||||
init.defaultBranch = "main";
|
||||
commit.gpgSign = true;
|
||||
gpg.format = "ssh";
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
7
modules/hm/shell/github.nix
Normal file
7
modules/hm/shell/github.nix
Normal file
@@ -0,0 +1,7 @@
|
||||
{
|
||||
flake.modules.homeManager.shell = {
|
||||
programs.gh = {
|
||||
enable = true;
|
||||
};
|
||||
};
|
||||
}
|
||||
@@ -1,16 +1,86 @@
|
||||
{
|
||||
flake.modules.homeManager.shell =
|
||||
{ pkgs, ... }:
|
||||
{
|
||||
home.packages = with pkgs; [
|
||||
systemctl-tui
|
||||
zip
|
||||
unzip
|
||||
pciutils
|
||||
usbutils
|
||||
jq
|
||||
dig
|
||||
lsof
|
||||
];
|
||||
};
|
||||
flake.modules.homeManager.shell = {pkgs, ...}: {
|
||||
home.packages = with pkgs; [
|
||||
systemctl-tui
|
||||
zip
|
||||
unzip
|
||||
pciutils
|
||||
usbutils
|
||||
jq
|
||||
dig
|
||||
lsof
|
||||
trok
|
||||
|
||||
(writeShellScriptBin "hm-override" ''
|
||||
#!/usr/bin/env bash
|
||||
|
||||
set -euo pipefail
|
||||
|
||||
usage() {
|
||||
echo "Usage:"
|
||||
echo " $0 <filename> Override symlink"
|
||||
echo " $0 <filename> --restore Restore symlink"
|
||||
echo " $0 <filename> -r Restore symlink"
|
||||
exit 1
|
||||
}
|
||||
|
||||
if [[ $# -lt 1 || $# -gt 2 ]]; then
|
||||
usage
|
||||
fi
|
||||
|
||||
FILE="$1"
|
||||
LINK_BACKUP="''${FILE}.backup-link"
|
||||
|
||||
# Restore
|
||||
if [[ "''${2:-}" == "--restore" || "''${2:-}" == "-r" ]]; then
|
||||
if [[ ! -f "$LINK_BACKUP" ]]; then
|
||||
echo "Error: no backup symlink found: $LINK_BACKUP"
|
||||
exit 1
|
||||
fi
|
||||
|
||||
TARGET="$(cat "$LINK_BACKUP")"
|
||||
|
||||
# Remove the temporary override.
|
||||
rm -f "$FILE"
|
||||
|
||||
# Restore the original symlink.
|
||||
ln -s "$TARGET" "$FILE"
|
||||
|
||||
# Remove the temporary symlink target backup.
|
||||
rm "$LINK_BACKUP"
|
||||
|
||||
echo "Restored: $FILE -> $TARGET"
|
||||
exit 0
|
||||
fi
|
||||
|
||||
# Override mode
|
||||
if [[ ! -L "$FILE" ]]; then
|
||||
echo "Error: $FILE is not a symlink"
|
||||
exit 1
|
||||
fi
|
||||
|
||||
if [[ -e "$LINK_BACKUP" ]]; then
|
||||
echo "Error: backup already exists: $LINK_BACKUP"
|
||||
echo "Restore the existing override before running again."
|
||||
exit 1
|
||||
fi
|
||||
|
||||
# Remember the original symlink target.
|
||||
TARGET="$(readlink "$FILE")"
|
||||
printf '%s\n' "$TARGET" > "$LINK_BACKUP"
|
||||
|
||||
# Copy the contents before removing the symlink.
|
||||
cp "$FILE" "$FILE.tmp"
|
||||
|
||||
# Replace the symlink with a regular writable file.
|
||||
rm "$FILE"
|
||||
mv "$FILE.tmp" "$FILE"
|
||||
|
||||
chmod u+w "$FILE"
|
||||
|
||||
echo "Overridden: $FILE"
|
||||
echo "Original: $FILE -> $TARGET"
|
||||
'')
|
||||
];
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,42 +1,38 @@
|
||||
{
|
||||
flake.modules.homeManager.shell =
|
||||
{ pkgs, ... }:
|
||||
{
|
||||
home.file = {
|
||||
".config/nvim" = {
|
||||
recursive = true;
|
||||
source = "${pkgs.tnvim}";
|
||||
};
|
||||
};
|
||||
|
||||
programs = {
|
||||
neovim = {
|
||||
enable = true;
|
||||
defaultEditor = true;
|
||||
};
|
||||
|
||||
vim.enable = true;
|
||||
};
|
||||
|
||||
home = {
|
||||
packages = with pkgs; [
|
||||
python3
|
||||
nodejs
|
||||
bun
|
||||
pnpm
|
||||
go
|
||||
rustup
|
||||
typescript
|
||||
neovide
|
||||
nil
|
||||
statix
|
||||
deadnix
|
||||
alejandra
|
||||
luarocks
|
||||
gdu
|
||||
gcc
|
||||
wakatime-cli
|
||||
];
|
||||
flake.modules.homeManager.shell = {pkgs, ...}: {
|
||||
home.file = {
|
||||
".config/nvim" = {
|
||||
recursive = true;
|
||||
source = "${pkgs.tnvim}";
|
||||
};
|
||||
};
|
||||
|
||||
programs = {
|
||||
neovim = {
|
||||
enable = true;
|
||||
defaultEditor = true;
|
||||
};
|
||||
};
|
||||
|
||||
home = {
|
||||
packages = with pkgs; [
|
||||
python3
|
||||
nodejs
|
||||
bun
|
||||
pnpm
|
||||
go
|
||||
rustup
|
||||
typescript
|
||||
neovide
|
||||
nil
|
||||
statix
|
||||
deadnix
|
||||
alejandra
|
||||
luarocks
|
||||
gdu
|
||||
gcc
|
||||
wakatime-cli
|
||||
];
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,12 +1,13 @@
|
||||
{
|
||||
flake.modules.homeManager.shell = {
|
||||
flake.modules.homeManager.shell = {pkgs, ...}: {
|
||||
programs.opencode = {
|
||||
enable = true;
|
||||
package = pkgs.opencode-git;
|
||||
tui = {
|
||||
theme = "system";
|
||||
};
|
||||
settings = {
|
||||
model = "opencode-go/kimi-k3";
|
||||
model = "opencode-go/deepseek-v4.1-flash";
|
||||
provider = {
|
||||
google = {
|
||||
options = {
|
||||
@@ -23,7 +24,13 @@
|
||||
apiKey = "{file:/run/secrets/opencode-go-api-key}";
|
||||
};
|
||||
};
|
||||
zai-coding-plan = {
|
||||
options = {
|
||||
apiKey = "{file:/run/secrets/zai-coding-plan-api-key}";
|
||||
};
|
||||
};
|
||||
};
|
||||
plugin = ["@dietrichgebert/ponytail"];
|
||||
};
|
||||
};
|
||||
};
|
||||
|
||||
@@ -1,155 +1,138 @@
|
||||
{
|
||||
flake.modules.homeManager.shell =
|
||||
{ pkgs, ... }:
|
||||
let
|
||||
bg = "default";
|
||||
fg = "default";
|
||||
bg2 = "brightblack";
|
||||
fg2 = "white";
|
||||
color = c: "#{@${c}}";
|
||||
flake.modules.homeManager.shell = {pkgs, ...}: let
|
||||
bg = "default";
|
||||
fg = "default";
|
||||
bg2 = "brightblack";
|
||||
fg2 = "white";
|
||||
color = c: "#{@${c}}";
|
||||
|
||||
indicator =
|
||||
let
|
||||
accent = color "indicator_color";
|
||||
content = " ";
|
||||
in
|
||||
"#[reverse,fg=${accent}]#{?client_prefix,${content},}";
|
||||
indicator = let
|
||||
accent = color "indicator_color";
|
||||
content = " ";
|
||||
in "#[reverse,fg=${accent}]#{?client_prefix,${content},}";
|
||||
|
||||
current_window =
|
||||
let
|
||||
accent = color "main_accent";
|
||||
index = "#[reverse,fg=${accent},bg=${fg}] #I ";
|
||||
name = "#[fg=${bg2},bg=${fg2}] #W ";
|
||||
# flags = "#{?window_flags,#{window_flags}, }";
|
||||
in
|
||||
"${index}${name}";
|
||||
current_window = let
|
||||
accent = color "main_accent";
|
||||
index = "#[reverse,fg=${accent},bg=${fg}] #I ";
|
||||
name = "#[fg=${bg2},bg=${fg2}] #W ";
|
||||
# flags = "#{?window_flags,#{window_flags}, }";
|
||||
in "${index}${name}";
|
||||
|
||||
window_status =
|
||||
let
|
||||
accent = color "window_color";
|
||||
index = "#[reverse,fg=${accent},bg=${fg}] #I ";
|
||||
name = "#[fg=${bg2},bg=${fg2}] #W ";
|
||||
# flags = "#{?window_flags,#{window_flags}, }";
|
||||
in
|
||||
"${index}${name}";
|
||||
window_status = let
|
||||
accent = color "window_color";
|
||||
index = "#[reverse,fg=${accent},bg=${fg}] #I ";
|
||||
name = "#[fg=${bg2},bg=${fg2}] #W ";
|
||||
# flags = "#{?window_flags,#{window_flags}, }";
|
||||
in "${index}${name}";
|
||||
|
||||
battery =
|
||||
let
|
||||
percentage = pkgs.writeShellScript "percentage" (
|
||||
if pkgs.stdenv.isDarwin then
|
||||
''
|
||||
echo $(pmset -g batt | grep -o "[0-9]\+%" | tr '%' ' ')
|
||||
''
|
||||
else
|
||||
''
|
||||
path="/org/freedesktop/UPower/devices/DisplayDevice"
|
||||
echo $(${pkgs.upower}/bin/upower -i $path | grep -o "[0-9]\+%" | tr '%' ' ')
|
||||
''
|
||||
);
|
||||
state = pkgs.writeShellScript "state" (
|
||||
if pkgs.stdenv.isDarwin then
|
||||
''
|
||||
echo $(pmset -g batt | awk '{print $4}')
|
||||
''
|
||||
else
|
||||
''
|
||||
path="/org/freedesktop/UPower/devices/DisplayDevice"
|
||||
echo $(${pkgs.upower}/bin/upower -i $path | grep state | awk '{print $2}')
|
||||
''
|
||||
);
|
||||
icon = pkgs.writeShellScript "icon" ''
|
||||
percentage=$(${percentage})
|
||||
state=$(${state})
|
||||
if [ "$state" == "charging" ] || [ "$state" == "fully-charged" ]; then echo ""
|
||||
elif [ $percentage -ge 75 ]; then echo ""
|
||||
elif [ $percentage -ge 50 ]; then echo ""
|
||||
elif [ $percentage -ge 25 ]; then echo ""
|
||||
elif [ $percentage -ge 0 ]; then echo ""
|
||||
fi
|
||||
'';
|
||||
color = pkgs.writeShellScript "color" ''
|
||||
percentage=$(${percentage})
|
||||
state=$(${state})
|
||||
if [ "$state" == "charging" ] || [ "$state" == "fully-charged" ]; then echo "green"
|
||||
elif [ $percentage -ge 75 ]; then echo "green"
|
||||
elif [ $percentage -ge 50 ]; then echo "${fg2}"
|
||||
elif [ $percentage -ge 30 ]; then echo "yellow"
|
||||
elif [ $percentage -ge 0 ]; then echo "red"
|
||||
fi
|
||||
'';
|
||||
in
|
||||
"#[fg=#(${color})]#(${icon}) #[fg=${fg}]#(${percentage})%";
|
||||
battery = let
|
||||
percentage = pkgs.writeShellScript "percentage" (
|
||||
if pkgs.stdenv.isDarwin
|
||||
then ''
|
||||
echo $(pmset -g batt | grep -o "[0-9]\+%" | tr '%' ' ')
|
||||
''
|
||||
else ''
|
||||
path="/org/freedesktop/UPower/devices/DisplayDevice"
|
||||
echo $(${pkgs.upower}/bin/upower -i $path | grep -o "[0-9]\+%" | tr '%' ' ')
|
||||
''
|
||||
);
|
||||
state = pkgs.writeShellScript "state" (
|
||||
if pkgs.stdenv.isDarwin
|
||||
then ''
|
||||
echo $(pmset -g batt | awk '{print $4}')
|
||||
''
|
||||
else ''
|
||||
path="/org/freedesktop/UPower/devices/DisplayDevice"
|
||||
echo $(${pkgs.upower}/bin/upower -i $path | grep state | awk '{print $2}')
|
||||
''
|
||||
);
|
||||
icon = pkgs.writeShellScript "icon" ''
|
||||
percentage=$(${percentage})
|
||||
state=$(${state})
|
||||
if [ "$state" == "charging" ] || [ "$state" == "fully-charged" ]; then echo ""
|
||||
elif [ $percentage -ge 75 ]; then echo ""
|
||||
elif [ $percentage -ge 50 ]; then echo ""
|
||||
elif [ $percentage -ge 25 ]; then echo ""
|
||||
elif [ $percentage -ge 0 ]; then echo ""
|
||||
fi
|
||||
'';
|
||||
color = pkgs.writeShellScript "color" ''
|
||||
percentage=$(${percentage})
|
||||
state=$(${state})
|
||||
if [ "$state" == "charging" ] || [ "$state" == "fully-charged" ]; then echo "green"
|
||||
elif [ $percentage -ge 75 ]; then echo "green"
|
||||
elif [ $percentage -ge 50 ]; then echo "${fg2}"
|
||||
elif [ $percentage -ge 30 ]; then echo "yellow"
|
||||
elif [ $percentage -ge 0 ]; then echo "red"
|
||||
fi
|
||||
'';
|
||||
in "#[fg=#(${color})]#(${icon}) #[fg=${fg}]#(${percentage})%";
|
||||
|
||||
pwd =
|
||||
let
|
||||
accent = color "main_accent";
|
||||
icon = "#[fg=${accent}] ";
|
||||
format = "#[fg=${fg}]#{b:pane_current_path}";
|
||||
in
|
||||
"${icon}${format}";
|
||||
pwd = let
|
||||
accent = color "main_accent";
|
||||
icon = "#[fg=${accent}] ";
|
||||
format = "#[fg=${fg}]#{b:pane_current_path}";
|
||||
in "${icon}${format}";
|
||||
|
||||
git =
|
||||
let
|
||||
icon = pkgs.writeShellScript "branch" ''
|
||||
git -C "$1" branch && echo " "
|
||||
'';
|
||||
branch = pkgs.writeShellScript "branch" ''
|
||||
git -C "$1" rev-parse --abbrev-ref HEAD
|
||||
'';
|
||||
in
|
||||
"#[fg=magenta]#(${icon} #{pane_current_path})#(${branch} #{pane_current_path})";
|
||||
git = let
|
||||
icon = pkgs.writeShellScript "branch" ''
|
||||
git -C "$1" branch && echo " "
|
||||
'';
|
||||
branch = pkgs.writeShellScript "branch" ''
|
||||
git -C "$1" rev-parse --abbrev-ref HEAD
|
||||
'';
|
||||
in "#[fg=magenta]#(${icon} #{pane_current_path})#(${branch} #{pane_current_path})";
|
||||
|
||||
separator = "#[fg=${fg}]|";
|
||||
in
|
||||
{
|
||||
programs.tmux = {
|
||||
enable = true;
|
||||
baseIndex = 1;
|
||||
escapeTime = 0;
|
||||
mouse = true;
|
||||
extraConfig = ''
|
||||
set-option -sa terminal-overrides ",xterm*:Tc"
|
||||
set-option -g status-position top
|
||||
unbind r
|
||||
bind r source-file ~/.config/tmux/tmux.conf
|
||||
separator = "#[fg=${fg}]|";
|
||||
in {
|
||||
programs.tmux = {
|
||||
enable = true;
|
||||
baseIndex = 1;
|
||||
escapeTime = 0;
|
||||
mouse = true;
|
||||
extraConfig = ''
|
||||
set-option -sa terminal-overrides ",xterm*:Tc"
|
||||
set-option -g status-position top
|
||||
unbind r
|
||||
bind r source-file ~/.config/tmux/tmux.conf
|
||||
|
||||
# remap prefix from C-b to C-Space
|
||||
# unbind C-b
|
||||
# set -g prefix C-Space
|
||||
# bind C-Space send-prefix
|
||||
# remap prefix from C-b to C-Space
|
||||
# unbind C-b
|
||||
# set -g prefix C-Space
|
||||
# bind C-Space send-prefix
|
||||
|
||||
# split panes using | and -
|
||||
unbind '"'
|
||||
unbind %
|
||||
bind | split-window -h
|
||||
bind - split-window -v
|
||||
# split panes using | and -
|
||||
unbind '"'
|
||||
unbind %
|
||||
bind | split-window -h
|
||||
bind - split-window -v
|
||||
|
||||
# Start windows and panes at 1, not 0
|
||||
set -g base-index 1
|
||||
set -g pane-base-index 1
|
||||
set-window-option -g pane-base-index 1
|
||||
set-option -g renumber-windows on
|
||||
# Start windows and panes at 1, not 0
|
||||
set -g base-index 1
|
||||
set -g pane-base-index 1
|
||||
set-window-option -g pane-base-index 1
|
||||
set-option -g renumber-windows on
|
||||
|
||||
# switch panes using Alt-arrow without prefix
|
||||
bind -n M-Left select-pane -L
|
||||
bind -n M-Right select-pane -R
|
||||
bind -n M-Up select-pane -U
|
||||
bind -n M-Down select-pane -D
|
||||
# switch panes using Alt-arrow without prefix
|
||||
bind -n M-Left select-pane -L
|
||||
bind -n M-Right select-pane -R
|
||||
bind -n M-Up select-pane -U
|
||||
bind -n M-Down select-pane -D
|
||||
|
||||
set-option -g default-terminal "screen-256color"
|
||||
set-option -g status-right-length 100
|
||||
set-option -g @indicator_color "yellow"
|
||||
set-option -g @window_color "magenta"
|
||||
set-option -g @main_accent "blue"
|
||||
set-option -g pane-active-border fg=black
|
||||
set-option -g pane-border-style fg=black
|
||||
set-option -g status-style "bg=${bg} fg=${fg}"
|
||||
set-option -g status-left "${indicator}"
|
||||
set-option -g status-right "${git} ${pwd} ${separator} ${battery}"
|
||||
set-option -g window-status-current-format "${current_window}"
|
||||
set-option -g window-status-format "${window_status}"
|
||||
set-option -g window-status-separator ""
|
||||
'';
|
||||
};
|
||||
set-option -g default-terminal "screen-256color"
|
||||
set-option -g status-right-length 100
|
||||
set-option -g @indicator_color "yellow"
|
||||
set-option -g @window_color "magenta"
|
||||
set-option -g @main_accent "blue"
|
||||
set-option -g pane-active-border fg=black
|
||||
set-option -g pane-border-style fg=black
|
||||
set-option -g status-style "bg=${bg} fg=${fg}"
|
||||
set-option -g status-left "${indicator}"
|
||||
set-option -g status-right "${git} ${pwd} ${separator} ${battery}"
|
||||
set-option -g window-status-current-format "${current_window}"
|
||||
set-option -g window-status-format "${window_status}"
|
||||
set-option -g window-status-separator ""
|
||||
'';
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -2,7 +2,7 @@
|
||||
flake.modules.homeManager.shell = {
|
||||
programs.zoxide = {
|
||||
enable = true;
|
||||
options = [ "--cmd cd" ];
|
||||
options = ["--cmd cd"];
|
||||
enableZshIntegration = true;
|
||||
};
|
||||
};
|
||||
|
||||
@@ -1,27 +1,28 @@
|
||||
{ lib, ... }:
|
||||
{
|
||||
flake.modules.homeManager.shell =
|
||||
{ pkgs, ... }:
|
||||
{
|
||||
programs.zsh = {
|
||||
enable = true;
|
||||
history = {
|
||||
append = true;
|
||||
share = true;
|
||||
expireDuplicatesFirst = true;
|
||||
ignoreDups = true;
|
||||
size = 1000000;
|
||||
save = 1000000;
|
||||
path = "$HOME/.local/share/zsh/.zsh_history";
|
||||
};
|
||||
fastSyntaxHighlighting.enable = true;
|
||||
autosuggestion.enable = true;
|
||||
initContent = ''
|
||||
${lib.getExe pkgs.fastfetch}
|
||||
bindkey "^A" vi-beginning-of-line
|
||||
bindkey "^E" vi-end-of-line
|
||||
bindkey '^R' fzf-history-widget
|
||||
'';
|
||||
{lib, ...}: {
|
||||
flake.modules.homeManager.shell = {pkgs, ...}: {
|
||||
programs.zsh = {
|
||||
enable = true;
|
||||
history = {
|
||||
append = true;
|
||||
share = true;
|
||||
expireDuplicatesFirst = true;
|
||||
ignoreDups = true;
|
||||
size = 1000000;
|
||||
save = 1000000;
|
||||
path = "$HOME/.local/share/zsh/.zsh_history";
|
||||
};
|
||||
fastSyntaxHighlighting.enable = true;
|
||||
autosuggestion.enable = true;
|
||||
initContent = ''
|
||||
${lib.getExe pkgs.fastfetch}
|
||||
bindkey "^A" vi-beginning-of-line
|
||||
bindkey "^E" vi-end-of-line
|
||||
bindkey '^R' fzf-history-widget
|
||||
|
||||
PATH=$PATH:~/.cargo/bin:~/.local/bin
|
||||
alias stui='systemctl-tui'
|
||||
alias vim='nvim --clean'
|
||||
'';
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,121 +1,143 @@
|
||||
{ config, ... }:
|
||||
{
|
||||
flake.modules.nixos.alpha =
|
||||
{
|
||||
hostName,
|
||||
userName,
|
||||
...
|
||||
}@innerArgs:
|
||||
{
|
||||
imports = with config.flake.modules.nixos; [
|
||||
inputs,
|
||||
config,
|
||||
...
|
||||
}: {
|
||||
flake.modules.nixos.alpha = {
|
||||
hostName,
|
||||
userName,
|
||||
...
|
||||
} @ innerArgs: {
|
||||
imports = with config.flake.modules.nixos;
|
||||
[
|
||||
boot
|
||||
networking
|
||||
virtualisation
|
||||
services
|
||||
]
|
||||
++ [
|
||||
inputs.trok.nixosModules.default
|
||||
inputs.tfolio.nixosModules.default
|
||||
];
|
||||
|
||||
tnix = {
|
||||
boot = {
|
||||
legacy.enable = true;
|
||||
tnix = {
|
||||
boot = {
|
||||
legacy.enable = true;
|
||||
|
||||
impermanence = {
|
||||
enable = true;
|
||||
impermanence = {
|
||||
enable = true;
|
||||
|
||||
home = {
|
||||
directories = [
|
||||
".local/share/nvim"
|
||||
".local/share/zsh"
|
||||
".local/share/zoxide"
|
||||
".local/state/lazygit"
|
||||
".local/share/opencode"
|
||||
];
|
||||
};
|
||||
home = {
|
||||
directories = [
|
||||
".local/share/nvim"
|
||||
".local/share/zsh"
|
||||
".local/share/zoxide"
|
||||
".local/state/lazygit"
|
||||
".local/share/opencode"
|
||||
];
|
||||
};
|
||||
};
|
||||
|
||||
networking = {
|
||||
openssh.enable = true;
|
||||
netbird-client.enable = true;
|
||||
};
|
||||
|
||||
services = {
|
||||
pangolin = {
|
||||
enable = true;
|
||||
domain = "pangolin.lab.tux.rs";
|
||||
baseDomain = "lab.tux.rs";
|
||||
environmentFile = innerArgs.config.sops.secrets."pangolin".path;
|
||||
};
|
||||
|
||||
uptime-kuma = {
|
||||
enable = true;
|
||||
domain = "status.lab.tux.rs";
|
||||
};
|
||||
|
||||
mediaflow-proxy = {
|
||||
enable = true;
|
||||
environmentFile = innerArgs.config.sops.secrets."mediaflow-proxy".path;
|
||||
};
|
||||
};
|
||||
|
||||
virtualisation = {
|
||||
docker.enable = true;
|
||||
};
|
||||
};
|
||||
|
||||
sops.secrets = {
|
||||
tux-password = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
neededForUsers = true;
|
||||
networking = {
|
||||
openssh = {
|
||||
enable = true;
|
||||
ports = [
|
||||
23
|
||||
];
|
||||
};
|
||||
netbird-client.enable = true;
|
||||
};
|
||||
|
||||
services = {
|
||||
pangolin = {
|
||||
enable = true;
|
||||
domain = "pangolin.lab.tux.rs";
|
||||
baseDomain = "lab.tux.rs";
|
||||
environmentFile = innerArgs.config.sops.secrets."pangolin".path;
|
||||
};
|
||||
|
||||
gemini-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
openrouter-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
opencode-go-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
netbird-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
"cloudflare-credentials/email" = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
};
|
||||
|
||||
"cloudflare-credentials/dns-api-token" = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
};
|
||||
|
||||
aiostreams = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
uptime-kuma = {
|
||||
enable = true;
|
||||
domain = "status.lab.tux.rs";
|
||||
};
|
||||
|
||||
mediaflow-proxy = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
enable = true;
|
||||
environmentFile = innerArgs.config.sops.secrets."mediaflow-proxy".path;
|
||||
};
|
||||
|
||||
pangolin = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
trok = {
|
||||
enable = true;
|
||||
};
|
||||
};
|
||||
|
||||
# --- Networking ---
|
||||
networking = {
|
||||
hostName = hostName;
|
||||
networkmanager.enable = true;
|
||||
firewall.enable = false;
|
||||
virtualisation = {
|
||||
docker.enable = true;
|
||||
};
|
||||
|
||||
system.stateVersion = "26.05";
|
||||
};
|
||||
|
||||
sops.secrets = {
|
||||
tux-password = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
neededForUsers = true;
|
||||
};
|
||||
|
||||
gemini-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
openrouter-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
opencode-go-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
zai-coding-plan-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
netbird-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
"cloudflare-credentials/email" = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
};
|
||||
|
||||
"cloudflare-credentials/dns-api-token" = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
};
|
||||
|
||||
aiostreams = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
};
|
||||
|
||||
mediaflow-proxy = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
};
|
||||
|
||||
pangolin = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
};
|
||||
};
|
||||
|
||||
# --- Networking ---
|
||||
networking = {
|
||||
hostName = hostName;
|
||||
networkmanager.enable = true;
|
||||
firewall.enable = false;
|
||||
};
|
||||
|
||||
services.tfolio.enable = true;
|
||||
|
||||
system.stateVersion = "26.05";
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,22 +1,23 @@
|
||||
{ inputs, ... }:
|
||||
{
|
||||
flake.modules.nixos.alpha =
|
||||
{ config, lib, ... }:
|
||||
let
|
||||
hasOptinPersistence = config.tnix.boot.impermanence.enable;
|
||||
isLegacy = config.tnix.boot.legacy.enable;
|
||||
in
|
||||
{
|
||||
imports = [
|
||||
inputs.disko.nixosModules.disko
|
||||
];
|
||||
{inputs, ...}: {
|
||||
flake.modules.nixos.alpha = {
|
||||
config,
|
||||
lib,
|
||||
...
|
||||
}: let
|
||||
hasOptinPersistence = config.tnix.boot.impermanence.enable;
|
||||
isLegacy = config.tnix.boot.legacy.enable;
|
||||
in {
|
||||
imports = [
|
||||
inputs.disko.nixosModules.disko
|
||||
];
|
||||
|
||||
disko.devices.disk.primary = {
|
||||
device = "/dev/sda";
|
||||
type = "disk";
|
||||
content = {
|
||||
type = "gpt";
|
||||
partitions = {
|
||||
disko.devices.disk.primary = {
|
||||
device = "/dev/sda";
|
||||
type = "disk";
|
||||
content = {
|
||||
type = "gpt";
|
||||
partitions =
|
||||
{
|
||||
ESP = {
|
||||
size = "1G";
|
||||
type = "EF00";
|
||||
@@ -36,36 +37,37 @@
|
||||
content = {
|
||||
type = "btrfs";
|
||||
# Base subvolumes that always exist
|
||||
subvolumes = {
|
||||
"/root" = {
|
||||
mountOptions = [
|
||||
"compress=zstd"
|
||||
"noatime"
|
||||
"space_cache=v2"
|
||||
];
|
||||
mountpoint = "/";
|
||||
subvolumes =
|
||||
{
|
||||
"/root" = {
|
||||
mountOptions = [
|
||||
"compress=zstd"
|
||||
"noatime"
|
||||
"space_cache=v2"
|
||||
];
|
||||
mountpoint = "/";
|
||||
};
|
||||
"/nix" = {
|
||||
mountOptions = [
|
||||
"compress=zstd"
|
||||
"noatime"
|
||||
"noacl"
|
||||
"space_cache=v2"
|
||||
];
|
||||
mountpoint = "/nix";
|
||||
};
|
||||
}
|
||||
# Conditionally merge /persist only when impermanence is enabled
|
||||
// lib.optionalAttrs hasOptinPersistence {
|
||||
"/persist" = {
|
||||
mountOptions = [
|
||||
"compress=zstd"
|
||||
"noatime"
|
||||
"space_cache=v2"
|
||||
];
|
||||
mountpoint = "/persist";
|
||||
};
|
||||
};
|
||||
"/nix" = {
|
||||
mountOptions = [
|
||||
"compress=zstd"
|
||||
"noatime"
|
||||
"noacl"
|
||||
"space_cache=v2"
|
||||
];
|
||||
mountpoint = "/nix";
|
||||
};
|
||||
}
|
||||
# Conditionally merge /persist only when impermanence is enabled
|
||||
// lib.optionalAttrs hasOptinPersistence {
|
||||
"/persist" = {
|
||||
mountOptions = [
|
||||
"compress=zstd"
|
||||
"noatime"
|
||||
"space_cache=v2"
|
||||
];
|
||||
mountpoint = "/persist";
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
@@ -76,7 +78,7 @@
|
||||
type = "EF02";
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,17 +1,15 @@
|
||||
{
|
||||
flake.modules.nixos.alpha =
|
||||
{
|
||||
lib,
|
||||
modulesPath,
|
||||
system,
|
||||
...
|
||||
}:
|
||||
{
|
||||
imports = [
|
||||
(modulesPath + "/profiles/qemu-guest.nix")
|
||||
];
|
||||
flake.modules.nixos.alpha = {
|
||||
lib,
|
||||
modulesPath,
|
||||
system,
|
||||
...
|
||||
}: {
|
||||
imports = [
|
||||
(modulesPath + "/profiles/qemu-guest.nix")
|
||||
];
|
||||
|
||||
networking.useDHCP = lib.mkDefault true;
|
||||
nixpkgs.hostPlatform = lib.mkDefault system;
|
||||
};
|
||||
networking.useDHCP = lib.mkDefault true;
|
||||
nixpkgs.hostPlatform = lib.mkDefault system;
|
||||
};
|
||||
}
|
||||
|
||||
@@ -2,6 +2,7 @@ tux-password: ENC[AES256_GCM,data:tvx3nMoIuQSotxHDWLs7UesnyWY3u3EwkqAIzCw3Z2AJse
|
||||
gemini-api-key: ENC[AES256_GCM,data:Bo3Z5Jhce0UOBn77I2AcrXYbBgPLDx0eOjPC8J63E/VWNhMPbbxb,iv:iWOsTACOMcK3oqq848WnJ5Ku3tYy1aadmLB4IMgoyqg=,tag:BPzlXoP8/iJaj8c/YFCWyg==,type:str]
|
||||
openrouter-api-key: ENC[AES256_GCM,data:D+/ImUTg7UvBTh0fMlWMZ0O/GsQS/R4Hz+CO4l42R6mn+zk+udvw79BctXdWWyrFf2ZNOTJ/99QTtWOUOvHISWaEJogXyb+93g==,iv:c7OtgBu1Zaf7lA4InIsKOAPbAvTl3gaO7QGCFNx21Bo=,tag:KXiASj/qC1YzK6DUox57ug==,type:str]
|
||||
opencode-go-api-key: ENC[AES256_GCM,data:ipKkNcRqBERIQ6f6yFzVm999s+UwJys4elHWhzpL441RfOaG9MmRWMcD+wRLJ7DSWFjYu6uUPF7TKez8J6abWeKDgg==,iv:FDSYE3R8zKVxWiP2S/sCVcwEu3fEXg/hCeqCRSF+c6g=,tag:5RDuMFGMoN6xwAYj0HiyjQ==,type:str]
|
||||
zai-coding-plan-api-key: ENC[AES256_GCM,data:HrNfR+Ux/Iyt4qkD1uXzDFQb+l0ltMMrbRahEG3pofFbw98VXfRFbhspcxh9vEyqkw==,iv:lzkLxPV7Q38dn0IEgtchVMrvnVBz4e5q282704x/hmU=,tag:IKzE6Tp6D93nJHoEvCPGBQ==,type:str]
|
||||
netbird-key: ENC[AES256_GCM,data:NilfyafnGhFVYD6q4+jJQxlhXNdNC8BQ1CZfu8a5wc693Y1h,iv:Rpl0OpkQdBMPpIJ08t9Z0AjDAW6c97pFZKO1KPu8ipY=,tag:du3d0SQWuqJtJSwhSgJE4g==,type:str]
|
||||
cloudflare-credentials:
|
||||
email: ENC[AES256_GCM,data:K9L6H4dqNNgbCFg=,iv:jirDJb+Y2sXrup6/doRmOdd8tV7zLnttcgG75r4Fs04=,tag:XeyMVC+Q9TEuTxSfOeR2Uw==,type:str]
|
||||
@@ -29,7 +30,7 @@ sops:
|
||||
4TkObqH8ddGpbd7cX5a/wboTjYuEdAviWxjK2oBPgtcFc1f03X3tmA==
|
||||
-----END AGE ENCRYPTED FILE-----
|
||||
recipient: age1mzxxxzhy3us3rd960ufqv7vlxj5cnug86md6x69llg9ujzw2pqws057llf
|
||||
lastmodified: "2026-08-07T20:02:00Z"
|
||||
mac: ENC[AES256_GCM,data:VrA2OPCcVvAzYjZTkHPxytclISP24P1FqiIQjSGQItkMLieom80N6933hB0Tdn3BM6600bHt2NweSqHjGx//pn2Gbur4pxeN3TpF9tKXc12IcAThUL9g48fMbk5y+kWWVUF1Pezod0YnzWAlalUXFqvKinfm4RqPNjDjndA/dcI=,iv:xfs9XD5ZIQ6dyMMZ8OE5FEs/hrSr/T2VwC7XvZ7xC2A=,tag:jYWo2kgwwltKB+njiYaPkQ==,type:str]
|
||||
lastmodified: "2026-09-16T14:21:00Z"
|
||||
mac: ENC[AES256_GCM,data:Aqg1cboHKW5QrJooVIqgbHTFg9EpTEnfCv/RRSp0efzyXvDrR7eG5WTvJPE9IbrmS190yvOlT0fw1Bhzyr8kiyoO71sbyUessw5IMUGcLP+m2FNtt8osc7fSTGseojv3MXBndOMDEOpT+Clv6hbv/rr5eGbb05oK6rW97/pDDfU=,iv:s/9PAHHQ0mHQJosKGclSnumHqm6CG3fDVKD5eT4Q1Y0=,tag:3pgycAwYUz9aEOy4/aW30Q==,type:str]
|
||||
unencrypted_suffix: _unencrypted
|
||||
version: 3.13.3
|
||||
|
||||
@@ -1,159 +1,175 @@
|
||||
{ config, ... }:
|
||||
{
|
||||
flake.modules.nixos.arcturus =
|
||||
{
|
||||
hostName,
|
||||
userName,
|
||||
...
|
||||
}@innerArgs:
|
||||
{
|
||||
imports = with config.flake.modules.nixos; [
|
||||
boot
|
||||
networking
|
||||
virtualisation
|
||||
services
|
||||
];
|
||||
{config, ...}: {
|
||||
flake.modules.nixos.arcturus = {
|
||||
pkgs,
|
||||
hostName,
|
||||
userName,
|
||||
...
|
||||
} @ innerArgs: {
|
||||
imports = with config.flake.modules.nixos; [
|
||||
boot
|
||||
networking
|
||||
virtualisation
|
||||
services
|
||||
];
|
||||
|
||||
tnix = {
|
||||
boot = {
|
||||
secure-boot.enable = true;
|
||||
tnix = {
|
||||
boot = {
|
||||
secure-boot.enable = true;
|
||||
|
||||
impermanence = {
|
||||
enable = true;
|
||||
impermanence = {
|
||||
enable = true;
|
||||
|
||||
home = {
|
||||
directories = [
|
||||
"Distrobox"
|
||||
".config/sops"
|
||||
".local/share/nvim"
|
||||
".local/share/opencode"
|
||||
".local/share/zsh"
|
||||
".local/share/zoxide"
|
||||
".local/state/lazygit"
|
||||
];
|
||||
home = {
|
||||
directories = [
|
||||
"Distrobox"
|
||||
".bun"
|
||||
".rustup"
|
||||
".config/sops"
|
||||
".config/nix"
|
||||
".local/share/nvim"
|
||||
".local/share/opencode"
|
||||
".local/share/zsh"
|
||||
".local/share/zoxide"
|
||||
".local/state/lazygit"
|
||||
];
|
||||
|
||||
files = [
|
||||
".wakatime.cfg"
|
||||
];
|
||||
};
|
||||
files = [
|
||||
".wakatime.cfg"
|
||||
];
|
||||
};
|
||||
};
|
||||
|
||||
networking = {
|
||||
openssh.enable = true;
|
||||
netbird-client.enable = true;
|
||||
newt = {
|
||||
enable = true;
|
||||
environmentFile = innerArgs.config.sops.secrets.newt.path;
|
||||
};
|
||||
};
|
||||
|
||||
services = {
|
||||
hermes-agent = {
|
||||
enable = true;
|
||||
environmentFiles = [ innerArgs.config.sops.secrets.hermes.path ];
|
||||
};
|
||||
|
||||
cyber-tux = {
|
||||
enable = true;
|
||||
environmentFile = innerArgs.config.sops.secrets.discord-token.path;
|
||||
};
|
||||
|
||||
vaultwarden = {
|
||||
enable = true;
|
||||
domain = "bw.lab.tux.rs";
|
||||
configurePangolin = true;
|
||||
};
|
||||
|
||||
copyparty = {
|
||||
enable = true;
|
||||
domain = "files.lab.tux.rs";
|
||||
accounts.${userName}.passwordFile = innerArgs.config.sops.secrets.copyparty.path;
|
||||
volumes = {
|
||||
"/" = {
|
||||
path = "/var/lib/copyparty/data";
|
||||
access = {
|
||||
r = "*";
|
||||
rwmdgGha = [ userName ];
|
||||
};
|
||||
};
|
||||
};
|
||||
configurePangolin = true;
|
||||
};
|
||||
};
|
||||
|
||||
virtualisation = {
|
||||
docker.enable = true;
|
||||
distrobox.enable = true;
|
||||
};
|
||||
};
|
||||
|
||||
sops.secrets = {
|
||||
tux-password = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
neededForUsers = true;
|
||||
};
|
||||
|
||||
discord-token = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
};
|
||||
|
||||
gemini-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
openrouter-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
opencode-go-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
netbird-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
networking = {
|
||||
openssh.enable = true;
|
||||
netbird-client.enable = true;
|
||||
newt = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
enable = true;
|
||||
environmentFile = innerArgs.config.sops.secrets.newt.path;
|
||||
};
|
||||
};
|
||||
|
||||
services = {
|
||||
hermes-agent = {
|
||||
enable = true;
|
||||
environmentFiles = [innerArgs.config.sops.secrets.hermes.path];
|
||||
};
|
||||
|
||||
cyber-tux = {
|
||||
enable = true;
|
||||
environmentFile = innerArgs.config.sops.secrets.discord-token.path;
|
||||
};
|
||||
|
||||
vaultwarden = {
|
||||
enable = true;
|
||||
domain = "bw.lab.tux.rs";
|
||||
configurePangolin = true;
|
||||
};
|
||||
|
||||
copyparty = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = innerArgs.config.services.copyparty.user;
|
||||
};
|
||||
|
||||
hermes = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
};
|
||||
};
|
||||
|
||||
# --- Networking ---
|
||||
networking = {
|
||||
hostName = hostName;
|
||||
networkmanager = {
|
||||
enable = true;
|
||||
wifi.backend = "iwd";
|
||||
};
|
||||
wireless.iwd = {
|
||||
enable = true;
|
||||
settings = {
|
||||
Network = {
|
||||
EnableIPv6 = true;
|
||||
};
|
||||
Settings = {
|
||||
AutoConnect = true;
|
||||
domain = "files.lab.tux.rs";
|
||||
accounts.${userName}.passwordFile = innerArgs.config.sops.secrets.copyparty.path;
|
||||
volumes = {
|
||||
"/" = {
|
||||
path = "/var/lib/copyparty/data";
|
||||
access = {
|
||||
r = "*";
|
||||
rwmdgGha = [userName];
|
||||
};
|
||||
};
|
||||
};
|
||||
configurePangolin = true;
|
||||
};
|
||||
|
||||
coder = {
|
||||
enable = true;
|
||||
domain = "coder.lab.tux.rs";
|
||||
configurePangolin = true;
|
||||
};
|
||||
firewall.enable = false;
|
||||
};
|
||||
|
||||
system.stateVersion = "26.05";
|
||||
virtualisation = {
|
||||
docker.enable = true;
|
||||
distrobox.enable = true;
|
||||
};
|
||||
};
|
||||
|
||||
sops.secrets = {
|
||||
tux-password = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
neededForUsers = true;
|
||||
};
|
||||
|
||||
discord-token = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
};
|
||||
|
||||
gemini-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
openrouter-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
opencode-go-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
zai-coding-plan-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
netbird-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
newt = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
copyparty = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = innerArgs.config.services.copyparty.user;
|
||||
};
|
||||
|
||||
hermes = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
};
|
||||
};
|
||||
|
||||
# --- Networking ---
|
||||
networking = {
|
||||
hostName = hostName;
|
||||
networkmanager = {
|
||||
enable = true;
|
||||
wifi.backend = "iwd";
|
||||
};
|
||||
wireless.iwd = {
|
||||
enable = true;
|
||||
settings = {
|
||||
Network = {
|
||||
EnableIPv6 = true;
|
||||
};
|
||||
Settings = {
|
||||
AutoConnect = true;
|
||||
};
|
||||
};
|
||||
};
|
||||
firewall.enable = false;
|
||||
};
|
||||
|
||||
environment.systemPackages = with pkgs; [
|
||||
impala
|
||||
];
|
||||
|
||||
system.stateVersion = "26.05";
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,41 +1,42 @@
|
||||
{ inputs, ... }:
|
||||
{
|
||||
flake.modules.nixos.arcturus =
|
||||
{ config, lib, ... }:
|
||||
let
|
||||
hasOptinPersistence = config.tnix.boot.impermanence.enable;
|
||||
in
|
||||
{
|
||||
imports = [
|
||||
inputs.disko.nixosModules.disko
|
||||
];
|
||||
{inputs, ...}: {
|
||||
flake.modules.nixos.arcturus = {
|
||||
config,
|
||||
lib,
|
||||
...
|
||||
}: let
|
||||
hasOptinPersistence = config.tnix.boot.impermanence.enable;
|
||||
in {
|
||||
imports = [
|
||||
inputs.disko.nixosModules.disko
|
||||
];
|
||||
|
||||
disko.devices.disk.primary = {
|
||||
device = "/dev/nvme0n1";
|
||||
type = "disk";
|
||||
content = {
|
||||
type = "gpt";
|
||||
partitions = {
|
||||
ESP = {
|
||||
size = "1G";
|
||||
type = "EF00";
|
||||
content = {
|
||||
type = "filesystem";
|
||||
format = "vfat";
|
||||
mountpoint = "/boot";
|
||||
mountOptions = [
|
||||
"defaults"
|
||||
"umask=0077"
|
||||
];
|
||||
};
|
||||
disko.devices.disk.primary = {
|
||||
device = "/dev/nvme0n1";
|
||||
type = "disk";
|
||||
content = {
|
||||
type = "gpt";
|
||||
partitions = {
|
||||
ESP = {
|
||||
size = "1G";
|
||||
type = "EF00";
|
||||
content = {
|
||||
type = "filesystem";
|
||||
format = "vfat";
|
||||
mountpoint = "/boot";
|
||||
mountOptions = [
|
||||
"defaults"
|
||||
"umask=0077"
|
||||
];
|
||||
};
|
||||
root = {
|
||||
size = "100%";
|
||||
type = "8300";
|
||||
content = {
|
||||
type = "btrfs";
|
||||
# Base subvolumes that always exist
|
||||
subvolumes = {
|
||||
};
|
||||
root = {
|
||||
size = "100%";
|
||||
type = "8300";
|
||||
content = {
|
||||
type = "btrfs";
|
||||
# Base subvolumes that always exist
|
||||
subvolumes =
|
||||
{
|
||||
"/root" = {
|
||||
mountOptions = [
|
||||
"compress=zstd"
|
||||
@@ -65,10 +66,10 @@
|
||||
mountpoint = "/persist";
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,36 +1,33 @@
|
||||
{ config, ... }:
|
||||
{
|
||||
flake.modules.nixos.arcturus =
|
||||
{
|
||||
lib,
|
||||
pkgs,
|
||||
system,
|
||||
...
|
||||
}@innerArgs:
|
||||
{
|
||||
imports = with config.flake.modules.nixos; [
|
||||
hardware
|
||||
];
|
||||
{config, ...}: {
|
||||
flake.modules.nixos.arcturus = {
|
||||
lib,
|
||||
pkgs,
|
||||
system,
|
||||
...
|
||||
} @ innerArgs: {
|
||||
imports = with config.flake.modules.nixos; [
|
||||
hardware
|
||||
];
|
||||
|
||||
boot.initrd.availableKernelModules = [
|
||||
"nvme"
|
||||
"xhci_pci"
|
||||
"ahci"
|
||||
"usbhid"
|
||||
"usb_storage"
|
||||
"sd_mod"
|
||||
];
|
||||
boot.initrd.kernelModules = [ ];
|
||||
boot.kernelModules = [ "kvm-amd" ];
|
||||
boot.extraModulePackages = [ ];
|
||||
boot.initrd.availableKernelModules = [
|
||||
"nvme"
|
||||
"xhci_pci"
|
||||
"ahci"
|
||||
"usbhid"
|
||||
"usb_storage"
|
||||
"sd_mod"
|
||||
];
|
||||
boot.initrd.kernelModules = [];
|
||||
boot.kernelModules = ["kvm-amd"];
|
||||
boot.extraModulePackages = [];
|
||||
|
||||
hardware.cpu.amd.updateMicrocode = lib.mkDefault innerArgs.config.hardware.enableRedistributableFirmware;
|
||||
hardware.cpu.amd.updateMicrocode = lib.mkDefault innerArgs.config.hardware.enableRedistributableFirmware;
|
||||
|
||||
networking.useDHCP = lib.mkDefault true;
|
||||
nixpkgs.hostPlatform = lib.mkDefault system;
|
||||
networking.useDHCP = lib.mkDefault true;
|
||||
nixpkgs.hostPlatform = lib.mkDefault system;
|
||||
|
||||
environment.systemPackages = with pkgs; [
|
||||
nvtopPackages.amd
|
||||
];
|
||||
};
|
||||
environment.systemPackages = with pkgs; [
|
||||
nvtopPackages.amd
|
||||
];
|
||||
};
|
||||
}
|
||||
|
||||
@@ -3,6 +3,7 @@ discord-token: ENC[AES256_GCM,data:uzxkrNRRplL/1MfvPZ/EL+I8UACuZQBHZ95BSHuxW0nBj
|
||||
gemini-api-key: ENC[AES256_GCM,data:gLZSoYTdKY+rwIpYiXvN9n9PGkUD6q8Oe7dHnYkjEjwDf5qpjubg,iv:ySoNgQWTu9DjvbashF4ulyYP8fJUl4yrCTeBQ0jrGmw=,tag:FctubsQv50AP78JvTb9bpQ==,type:str]
|
||||
openrouter-api-key: ENC[AES256_GCM,data:6xONCl9lqOoO7b4CEyCz9607tICDUAkpglRjGS5nYq2ppg2UKqYTrWD1BGCA5Xfs/CWskniVhoNG3vscjKiYCCh9gbM6aqdmTQ==,iv:7Iwc9t00HOOBjA7URXcUO41badqYyJCkFHM/uPkLFxY=,tag:Cl39kitr2e0//HVwAdsdUQ==,type:str]
|
||||
opencode-go-api-key: ENC[AES256_GCM,data:dmeRKn7TWHnqvpyPQpcEG6yHTb2bRby/rh10ytL0jHj5R+lRmNVdmqUF92GTznY9vEaB6ZYCJecWhpm8g4upNfOWBg==,iv:9UMJpAlD8gpcNiN+liu3nawoAZQKapEg7sCp561N9E8=,tag:OZlASpOa5BQaQwFWjoLCRw==,type:str]
|
||||
zai-coding-plan-api-key: ENC[AES256_GCM,data:lLegmS/RIo7JoBoAyVdcS++rXS8W62cwz+zVsv4dPnlfjGFO/nVlI5InqC34sPxLRQ==,iv:BRC7eYVmdZuWwb+2k2FrnlJih63HXrcvhVp/K5t5td8=,tag:aP8x+Xcnkz2t0hn7erCkKw==,type:str]
|
||||
netbird-key: ENC[AES256_GCM,data:q6eKisca04qn/CvALrvXF79MsToDhvLRLv2JTiUBAZglCC9m,iv:jj0/ZD7IDgopprTVUgSfJmdAJmUP3iqewU3dqssGYbk=,tag:6IPRdCm2FGdlTEIX7jt3qA==,type:str]
|
||||
copyparty: ENC[AES256_GCM,data:QXt8IgTekg9rzFyuzpg=,iv:vJYfHqCiheq290K9TGACHNHyOWzIn60j1Kz502SE27w=,tag:ECt7Wavlqw1V6zgXiRZtUg==,type:str]
|
||||
newt: ENC[AES256_GCM,data:r5Rd81ZrzrIYbXtFkypbJltoGCOYrW6P4IpwGCtaH7lqCg7wD/WMboMx13HN4Mm0J4qbBpDakpfVv9qUTrisYP1xwpKkmY1kqPlFWRZN8hzuuNS2Tv3qUjavTp5XGotVPLHj1Cg/cwGcf8EAssYTwTy7H0PgdQKwqigQD1f1s/j4iXQ=,iv:1xP38/Ayt1xvn2fJGa5zgOrVNOw2J5taG1Orx6uNgZI=,tag:H9JXu9gzyyvTPWgXaoTsiw==,type:str]
|
||||
@@ -27,7 +28,7 @@ sops:
|
||||
TLKEYsPQgOJ7s8P9gw2uPUY6HRz86CtiC6EbO27u0+8BbI85x1QScg==
|
||||
-----END AGE ENCRYPTED FILE-----
|
||||
recipient: age1huqa3hc7wcxk4dpelrzny437nzrx4fnll3d8g9ahznzk268yju5qufapxy
|
||||
lastmodified: "2026-08-12T13:48:51Z"
|
||||
mac: ENC[AES256_GCM,data:0GyC8VW0qoPaIcKfGKto8wDF64gDmiIhczok8oiJ0l5B7+ZUCVAKmWkMaXHyrU7kqg06WSiIixsnclEjIMxlyZVBOcfQaXeSO51uom/ax+4CfzxSGxgnpySarWRfCHgkcGUeO/eci5MzmZPgAHy7b8IBcJWzVUCS7XBIMMyYwNs=,iv:yUsltZZ1y4fzi3Kakwt/ji/J+r/P1/3mLEQqZiN2pm4=,tag:6Fwo34LOX+jCXF9DoYUv/A==,type:str]
|
||||
lastmodified: "2026-09-16T14:20:26Z"
|
||||
mac: ENC[AES256_GCM,data:I33KZL3u+7jfOFu0qn4LVx2nACiURSd6RcEn0ojfT62yC/TcXlGGu4QeN1Dx4Nta77n/h8RzDTcZtiUJylLhiVBmqyMOoNaBOmLDJ+P1L7weYLoWMoaDP7IWyzttGkNTgvyv2nW5IxbdcTZwrcSlPtdupsJeNy76ATHO+eUsvGQ=,iv:FvQKGH5Vzm36huGDnMr15wQL9vsH2hsAhvu0BE/NfEI=,tag:fzAzzgmv3vjWs1VYhh4GeA==,type:str]
|
||||
unencrypted_suffix: _unencrypted
|
||||
version: 3.13.3
|
||||
|
||||
@@ -1,134 +1,161 @@
|
||||
{ config, ... }:
|
||||
{
|
||||
flake.modules.nixos.canopus =
|
||||
{
|
||||
pkgs,
|
||||
hostName,
|
||||
userName,
|
||||
...
|
||||
}:
|
||||
{
|
||||
imports = with config.flake.modules.nixos; [
|
||||
boot
|
||||
networking
|
||||
desktop
|
||||
gaming
|
||||
virtualisation
|
||||
];
|
||||
{config, ...}: {
|
||||
flake.modules.nixos.canopus = {
|
||||
pkgs,
|
||||
hostName,
|
||||
userName,
|
||||
...
|
||||
}: {
|
||||
imports = with config.flake.modules.nixos; [
|
||||
boot
|
||||
networking
|
||||
desktop
|
||||
gaming
|
||||
virtualisation
|
||||
];
|
||||
|
||||
tnix = {
|
||||
boot = {
|
||||
secure-boot.enable = true;
|
||||
tnix = {
|
||||
boot = {
|
||||
secure-boot.enable = true;
|
||||
|
||||
impermanence = {
|
||||
enable = true;
|
||||
impermanence = {
|
||||
enable = true;
|
||||
|
||||
home = {
|
||||
directories = [
|
||||
"Distrobox"
|
||||
".steam"
|
||||
".cache/awww"
|
||||
".config/BraveSoftware"
|
||||
".config/zed"
|
||||
".config/Vencord"
|
||||
".config/vesktop"
|
||||
".config/sops"
|
||||
".config/obs-studio"
|
||||
".config/easyeffects"
|
||||
".config/DankMaterialShell"
|
||||
".local/share/Steam"
|
||||
".local/share/nvim"
|
||||
".local/share/opencode"
|
||||
".local/share/zsh"
|
||||
".local/share/zoxide"
|
||||
".local/state/lazygit"
|
||||
".local/share/vicinae"
|
||||
".local/share/TelegramDesktop"
|
||||
".local/share/GalaxyBudsClient"
|
||||
];
|
||||
home = {
|
||||
directories = [
|
||||
"Distrobox"
|
||||
".steam"
|
||||
".bun"
|
||||
".rustup"
|
||||
".cache/awww"
|
||||
".cache/serpantinum"
|
||||
".config/BraveSoftware"
|
||||
".config/zed"
|
||||
".config/Vencord"
|
||||
".config/vesktop"
|
||||
".config/sops"
|
||||
".config/nix"
|
||||
".config/coderv2"
|
||||
".config/obs-studio"
|
||||
".config/easyeffects"
|
||||
".config/DankMaterialShell"
|
||||
".local/share/Steam"
|
||||
".local/share/lutris"
|
||||
".local/share/net.lutris.Lutris"
|
||||
".local/share/nvim"
|
||||
".local/share/opencode"
|
||||
".local/share/zsh"
|
||||
".local/share/zoxide"
|
||||
".local/share/voxtype"
|
||||
".local/state/lazygit"
|
||||
".local/share/vicinae"
|
||||
".local/share/TelegramDesktop"
|
||||
".local/share/GalaxyBudsClient"
|
||||
".local/state/serpantinum"
|
||||
".local/share/zed"
|
||||
|
||||
files = [
|
||||
".wakatime.cfg"
|
||||
];
|
||||
};
|
||||
".claude"
|
||||
".orca"
|
||||
".config/orca"
|
||||
".zcode"
|
||||
".config/ZCode"
|
||||
];
|
||||
|
||||
files = [
|
||||
".wakatime.cfg"
|
||||
".claude.json"
|
||||
".config/gh/hosts.yml"
|
||||
];
|
||||
};
|
||||
};
|
||||
|
||||
networking = {
|
||||
openssh.enable = true;
|
||||
netbird-client.enable = true;
|
||||
};
|
||||
|
||||
virtualisation = {
|
||||
docker.enable = true;
|
||||
docker.nvidia.enable = false;
|
||||
qemu.enable = true;
|
||||
waydroid.enable = true;
|
||||
distrobox.enable = true;
|
||||
};
|
||||
};
|
||||
|
||||
sops.secrets = {
|
||||
tux-password = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
neededForUsers = true;
|
||||
};
|
||||
|
||||
gemini-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
openrouter-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
opencode-go-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
netbird-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
vicinae-json = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
};
|
||||
|
||||
# --- Networking ---
|
||||
networking = {
|
||||
hostName = hostName;
|
||||
networkmanager = {
|
||||
enable = true;
|
||||
wifi.backend = "iwd";
|
||||
};
|
||||
wireless.iwd = {
|
||||
enable = true;
|
||||
settings = {
|
||||
Network = {
|
||||
EnableIPv6 = true;
|
||||
};
|
||||
Settings = {
|
||||
AutoConnect = true;
|
||||
};
|
||||
};
|
||||
};
|
||||
firewall.enable = false;
|
||||
openssh.enable = true;
|
||||
netbird-client.enable = true;
|
||||
};
|
||||
|
||||
environment.systemPackages = with pkgs; [
|
||||
davinci-resolve
|
||||
telegram-desktop
|
||||
galaxy-buds-client
|
||||
];
|
||||
virtualisation = {
|
||||
docker.enable = true;
|
||||
docker.nvidia.enable = false;
|
||||
qemu.enable = true;
|
||||
waydroid.enable = true;
|
||||
distrobox.enable = true;
|
||||
};
|
||||
|
||||
# !!! DO NOT CHANGE THIS !!!
|
||||
# This should match the version used at initial install.
|
||||
system.stateVersion = "26.05";
|
||||
programs.nix-ld.enable = true;
|
||||
};
|
||||
|
||||
sops.secrets = {
|
||||
tux-password = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
neededForUsers = true;
|
||||
};
|
||||
|
||||
gemini-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
openrouter-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
opencode-go-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
zai-coding-plan-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
netbird-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
vicinae-json = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
};
|
||||
|
||||
# --- Networking ---
|
||||
networking = {
|
||||
hostName = hostName;
|
||||
networkmanager = {
|
||||
enable = true;
|
||||
wifi.backend = "iwd";
|
||||
};
|
||||
wireless.iwd = {
|
||||
enable = true;
|
||||
settings = {
|
||||
Network = {
|
||||
EnableIPv6 = true;
|
||||
};
|
||||
Settings = {
|
||||
AutoConnect = true;
|
||||
};
|
||||
};
|
||||
};
|
||||
firewall.enable = false;
|
||||
};
|
||||
|
||||
environment.systemPackages = with pkgs; [
|
||||
davinci-resolve
|
||||
telegram-desktop
|
||||
galaxy-buds-client
|
||||
impala
|
||||
llm-agents.claude-code
|
||||
llm-agents.orca
|
||||
llm-agents.zcode
|
||||
coder
|
||||
];
|
||||
|
||||
# !!! DO NOT CHANGE THIS !!!
|
||||
# This should match the version used at initial install.
|
||||
system.stateVersion = "26.05";
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,49 +1,50 @@
|
||||
{ inputs, ... }:
|
||||
{
|
||||
flake.modules.nixos.canopus =
|
||||
{ config, lib, ... }:
|
||||
let
|
||||
hasOptinPersistence = config.tnix.boot.impermanence.enable;
|
||||
in
|
||||
{
|
||||
imports = [
|
||||
inputs.disko.nixosModules.disko
|
||||
];
|
||||
{inputs, ...}: {
|
||||
flake.modules.nixos.canopus = {
|
||||
config,
|
||||
lib,
|
||||
...
|
||||
}: let
|
||||
hasOptinPersistence = config.tnix.boot.impermanence.enable;
|
||||
in {
|
||||
imports = [
|
||||
inputs.disko.nixosModules.disko
|
||||
];
|
||||
|
||||
disko.devices.disk.primary = {
|
||||
device = "/dev/nvme0n1";
|
||||
type = "disk";
|
||||
content = {
|
||||
type = "gpt";
|
||||
partitions = {
|
||||
ESP = {
|
||||
size = "1G";
|
||||
type = "EF00";
|
||||
content = {
|
||||
type = "filesystem";
|
||||
format = "vfat";
|
||||
mountpoint = "/boot";
|
||||
mountOptions = [
|
||||
"defaults"
|
||||
"umask=0077"
|
||||
];
|
||||
};
|
||||
disko.devices.disk.primary = {
|
||||
device = "/dev/nvme0n1";
|
||||
type = "disk";
|
||||
content = {
|
||||
type = "gpt";
|
||||
partitions = {
|
||||
ESP = {
|
||||
size = "1G";
|
||||
type = "EF00";
|
||||
content = {
|
||||
type = "filesystem";
|
||||
format = "vfat";
|
||||
mountpoint = "/boot";
|
||||
mountOptions = [
|
||||
"defaults"
|
||||
"umask=0077"
|
||||
];
|
||||
};
|
||||
swap = {
|
||||
size = "32G";
|
||||
content = {
|
||||
type = "swap";
|
||||
discardPolicy = "both";
|
||||
resumeDevice = true;
|
||||
};
|
||||
};
|
||||
swap = {
|
||||
size = "32G";
|
||||
content = {
|
||||
type = "swap";
|
||||
discardPolicy = "both";
|
||||
resumeDevice = true;
|
||||
};
|
||||
root = {
|
||||
size = "100%";
|
||||
type = "8300";
|
||||
content = {
|
||||
type = "btrfs";
|
||||
# Base subvolumes that always exist
|
||||
subvolumes = {
|
||||
};
|
||||
root = {
|
||||
size = "100%";
|
||||
type = "8300";
|
||||
content = {
|
||||
type = "btrfs";
|
||||
# Base subvolumes that always exist
|
||||
subvolumes =
|
||||
{
|
||||
"/root" = {
|
||||
mountOptions = [
|
||||
"compress=zstd"
|
||||
@@ -73,10 +74,10 @@
|
||||
mountpoint = "/persist";
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,150 +1,150 @@
|
||||
{ inputs, config, ... }:
|
||||
{
|
||||
flake.modules.nixos.canopus =
|
||||
{
|
||||
lib,
|
||||
pkgs,
|
||||
system,
|
||||
...
|
||||
}@innerArgs:
|
||||
{
|
||||
imports =
|
||||
with config.flake.modules.nixos;
|
||||
[
|
||||
hardware
|
||||
]
|
||||
++ [
|
||||
inputs.nixos-hardware.nixosModules.asus-zephyrus-ga503
|
||||
inputs.cardwire.nixosModules.default
|
||||
];
|
||||
|
||||
boot.kernelParams = [ "nvidia-drm.modeset=1" ];
|
||||
boot.initrd.availableKernelModules = [
|
||||
"nvme"
|
||||
"xhci_pci"
|
||||
"ahci"
|
||||
"usbhid"
|
||||
"usb_storage"
|
||||
"sd_mod"
|
||||
inputs,
|
||||
config,
|
||||
...
|
||||
}: {
|
||||
flake.modules.nixos.canopus = {
|
||||
lib,
|
||||
pkgs,
|
||||
system,
|
||||
...
|
||||
} @ innerArgs: {
|
||||
imports = with config.flake.modules.nixos;
|
||||
[
|
||||
hardware
|
||||
]
|
||||
++ [
|
||||
inputs.nixos-hardware.nixosModules.asus-zephyrus-ga503
|
||||
inputs.cardwire.nixosModules.default
|
||||
];
|
||||
boot.initrd.kernelModules = [ ];
|
||||
boot.kernelModules = [ "kvm-amd" ];
|
||||
boot.extraModulePackages = [ ];
|
||||
|
||||
hardware = {
|
||||
nvidia = {
|
||||
modesetting.enable = true;
|
||||
open = false;
|
||||
nvidiaSettings = true;
|
||||
};
|
||||
boot.kernelParams = ["nvidia-drm.modeset=1"];
|
||||
boot.initrd.availableKernelModules = [
|
||||
"nvme"
|
||||
"xhci_pci"
|
||||
"ahci"
|
||||
"usbhid"
|
||||
"usb_storage"
|
||||
"sd_mod"
|
||||
];
|
||||
boot.initrd.kernelModules = [];
|
||||
boot.kernelModules = ["kvm-amd"];
|
||||
boot.extraModulePackages = [];
|
||||
|
||||
cpu.amd.updateMicrocode = lib.mkDefault innerArgs.config.hardware.enableRedistributableFirmware;
|
||||
hardware = {
|
||||
nvidia = {
|
||||
modesetting.enable = true;
|
||||
open = false;
|
||||
nvidiaSettings = true;
|
||||
};
|
||||
|
||||
services = {
|
||||
xserver.videoDrivers = [ "nvidia" ];
|
||||
power-profiles-daemon.enable = true;
|
||||
upower.enable = true;
|
||||
|
||||
cardwire = {
|
||||
enable = true;
|
||||
settings = {
|
||||
auto_apply_gpu_state = true;
|
||||
experimental_nvidia_block = true;
|
||||
battery_auto_switch = true;
|
||||
battery_auto_switch_mode = "hybrid";
|
||||
};
|
||||
};
|
||||
|
||||
asusd = {
|
||||
enable = true;
|
||||
asusdConfig.text = ''
|
||||
(
|
||||
charge_control_end_threshold: 80,
|
||||
disable_nvidia_powerd_on_battery: true,
|
||||
ac_command: "",
|
||||
bat_command: "",
|
||||
|
||||
platform_profile_linked_epp: true,
|
||||
platform_profile_on_battery: Quiet,
|
||||
platform_profile_on_ac: Performance,
|
||||
|
||||
change_platform_profile_on_battery: true,
|
||||
change_platform_profile_on_ac: true,
|
||||
|
||||
profile_quiet_epp: Power,
|
||||
profile_balanced_epp: BalancePower,
|
||||
profile_custom_epp: Performance,
|
||||
profile_performance_epp: Performance,
|
||||
|
||||
ac_profile_tunings: {},
|
||||
dc_profile_tunings: {},
|
||||
armoury_settings: {},
|
||||
)
|
||||
'';
|
||||
profileConfig.text = ''
|
||||
(
|
||||
active_profile: Quiet,
|
||||
)
|
||||
'';
|
||||
fanCurvesConfig.text = ''
|
||||
(
|
||||
profiles: (
|
||||
balanced: [
|
||||
(
|
||||
fan: CPU,
|
||||
pwm: (20, 40, 60, 85, 110, 140, 170, 200),
|
||||
temp: (45, 55, 62, 68, 74, 80, 86, 92),
|
||||
enabled: true,
|
||||
),
|
||||
(
|
||||
fan: GPU,
|
||||
pwm: (20, 40, 60, 85, 110, 140, 170, 200),
|
||||
temp: (45, 55, 62, 68, 74, 80, 86, 92),
|
||||
enabled: true,
|
||||
),
|
||||
],
|
||||
performance: [
|
||||
(
|
||||
fan: CPU,
|
||||
pwm: (35, 60, 90, 120, 150, 180, 220, 255),
|
||||
temp: (45, 55, 62, 68, 74, 80, 86, 92),
|
||||
enabled: true,
|
||||
),
|
||||
(
|
||||
fan: GPU,
|
||||
pwm: (35, 60, 90, 120, 150, 180, 220, 255),
|
||||
temp: (45, 55, 62, 68, 74, 80, 86, 92),
|
||||
enabled: true,
|
||||
),
|
||||
],
|
||||
quiet: [
|
||||
(
|
||||
fan: CPU,
|
||||
pwm: (0, 10, 20, 35, 55, 80, 110, 140),
|
||||
temp: (45, 55, 62, 68, 74, 80, 86, 92),
|
||||
enabled: true,
|
||||
),
|
||||
(
|
||||
fan: GPU,
|
||||
pwm: (0, 10, 20, 35, 55, 80, 110, 140),
|
||||
temp: (45, 55, 62, 68, 74, 80, 86, 92),
|
||||
enabled: true,
|
||||
),
|
||||
],
|
||||
custom: [],
|
||||
),
|
||||
)
|
||||
'';
|
||||
};
|
||||
};
|
||||
|
||||
networking.useDHCP = lib.mkDefault true;
|
||||
nixpkgs.config.cudaSupport = true;
|
||||
nixpkgs.hostPlatform = lib.mkDefault system;
|
||||
|
||||
environment.systemPackages = with pkgs; [
|
||||
nvtopPackages.full
|
||||
];
|
||||
cpu.amd.updateMicrocode = lib.mkDefault innerArgs.config.hardware.enableRedistributableFirmware;
|
||||
};
|
||||
|
||||
services = {
|
||||
xserver.videoDrivers = ["nvidia"];
|
||||
power-profiles-daemon.enable = true;
|
||||
upower.enable = true;
|
||||
|
||||
cardwire = {
|
||||
enable = true;
|
||||
settings = {
|
||||
auto_apply_gpu_state = true;
|
||||
experimental_nvidia_block = true;
|
||||
battery_auto_switch = true;
|
||||
battery_auto_switch_mode = "hybrid";
|
||||
};
|
||||
};
|
||||
|
||||
asusd = {
|
||||
enable = true;
|
||||
asusdConfig.text = ''
|
||||
(
|
||||
charge_control_end_threshold: 80,
|
||||
disable_nvidia_powerd_on_battery: true,
|
||||
ac_command: "",
|
||||
bat_command: "",
|
||||
|
||||
platform_profile_linked_epp: true,
|
||||
platform_profile_on_battery: Quiet,
|
||||
platform_profile_on_ac: Performance,
|
||||
|
||||
change_platform_profile_on_battery: true,
|
||||
change_platform_profile_on_ac: true,
|
||||
|
||||
profile_quiet_epp: Power,
|
||||
profile_balanced_epp: BalancePower,
|
||||
profile_custom_epp: Performance,
|
||||
profile_performance_epp: Performance,
|
||||
|
||||
ac_profile_tunings: {},
|
||||
dc_profile_tunings: {},
|
||||
armoury_settings: {},
|
||||
)
|
||||
'';
|
||||
profileConfig.text = ''
|
||||
(
|
||||
active_profile: Quiet,
|
||||
)
|
||||
'';
|
||||
fanCurvesConfig.text = ''
|
||||
(
|
||||
profiles: (
|
||||
balanced: [
|
||||
(
|
||||
fan: CPU,
|
||||
pwm: (20, 40, 60, 85, 110, 140, 170, 200),
|
||||
temp: (45, 55, 62, 68, 74, 80, 86, 92),
|
||||
enabled: true,
|
||||
),
|
||||
(
|
||||
fan: GPU,
|
||||
pwm: (20, 40, 60, 85, 110, 140, 170, 200),
|
||||
temp: (45, 55, 62, 68, 74, 80, 86, 92),
|
||||
enabled: true,
|
||||
),
|
||||
],
|
||||
performance: [
|
||||
(
|
||||
fan: CPU,
|
||||
pwm: (35, 60, 90, 120, 150, 180, 220, 255),
|
||||
temp: (45, 55, 62, 68, 74, 80, 86, 92),
|
||||
enabled: true,
|
||||
),
|
||||
(
|
||||
fan: GPU,
|
||||
pwm: (35, 60, 90, 120, 150, 180, 220, 255),
|
||||
temp: (45, 55, 62, 68, 74, 80, 86, 92),
|
||||
enabled: true,
|
||||
),
|
||||
],
|
||||
quiet: [
|
||||
(
|
||||
fan: CPU,
|
||||
pwm: (0, 10, 20, 35, 55, 80, 110, 140),
|
||||
temp: (45, 55, 62, 68, 74, 80, 86, 92),
|
||||
enabled: true,
|
||||
),
|
||||
(
|
||||
fan: GPU,
|
||||
pwm: (0, 10, 20, 35, 55, 80, 110, 140),
|
||||
temp: (45, 55, 62, 68, 74, 80, 86, 92),
|
||||
enabled: true,
|
||||
),
|
||||
],
|
||||
custom: [],
|
||||
),
|
||||
)
|
||||
'';
|
||||
};
|
||||
};
|
||||
|
||||
networking.useDHCP = lib.mkDefault true;
|
||||
nixpkgs.config.cudaSupport = true;
|
||||
nixpkgs.hostPlatform = lib.mkDefault system;
|
||||
|
||||
environment.systemPackages = with pkgs; [
|
||||
nvtopPackages.full
|
||||
];
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,6 +1,5 @@
|
||||
{ config, ... }:
|
||||
{
|
||||
flake.modules.homeManager.canopus = { pkgs, ... }: {
|
||||
{config, ...}: {
|
||||
flake.modules.homeManager.canopus = {pkgs, ...}: {
|
||||
imports = with config.flake.modules.homeManager; [
|
||||
desktop
|
||||
];
|
||||
@@ -27,8 +26,7 @@
|
||||
enable = true;
|
||||
settings = {
|
||||
authorized_fingerprints = {
|
||||
"f4:4b:17:61:f7:01:a4:a2:e1:c7:8c:1c:7a:f3:8b:87:14:3d:05:3d:a0:8b:cc:e7:88:d8:d8:d2:a4:c2:75:8b" =
|
||||
"sirius";
|
||||
"f4:4b:17:61:f7:01:a4:a2:e1:c7:8c:1c:7a:f3:8b:87:14:3d:05:3d:a0:8b:cc:e7:88:d8:d8:d2:a4:c2:75:8b" = "sirius";
|
||||
};
|
||||
};
|
||||
};
|
||||
@@ -42,7 +40,7 @@
|
||||
position = "0x0",
|
||||
scale = "1",
|
||||
disabled = false
|
||||
})' &&
|
||||
})' &&
|
||||
hyprctl eval 'hl.monitor({
|
||||
output = "HDMI-A-1",
|
||||
mode = "preferred",
|
||||
@@ -58,7 +56,7 @@
|
||||
position = "0x0",
|
||||
scale = "1",
|
||||
disabled = false
|
||||
})' &&
|
||||
})' &&
|
||||
hyprctl eval 'hl.monitor({
|
||||
output = "HDMI-A-1",
|
||||
mode = "preferred",
|
||||
@@ -71,7 +69,7 @@
|
||||
hyprctl eval 'hl.monitor({
|
||||
output = "eDP-1",
|
||||
disabled = true
|
||||
})' &&
|
||||
})' &&
|
||||
hyprctl eval 'hl.monitor({
|
||||
output = "HDMI-A-1",
|
||||
mode = "preferred",
|
||||
|
||||
@@ -2,12 +2,12 @@ tux-password: ENC[AES256_GCM,data:Xb4/JMAZCBnBheDCJdRRGXLnMJ1ej8HbN+AUqA/+2sdYES
|
||||
gemini-api-key: ENC[AES256_GCM,data:Q6+actg0oyUWiUJVy/9yZmea1QyGu2o8LfMsuAVFD6k7kp0dYIrl,iv:ukyouqrHxzVpBBE98KL6PW8P3j+seemm/e0Gl1urUcM=,tag:Z7MM3dJ414CmdxE72cdzNA==,type:str]
|
||||
openrouter-api-key: ENC[AES256_GCM,data:SalhWKR6artX/kOVKZGpKSmrgsQDU/heshrdkK3wotOZ3BRn/ZqZRBldvl1JPSenMAMvE2LWUdmBQmwG/id7L7JL1O/+lUHIQw==,iv:hLlHayFJgUkWOirVLfqP0pGRBZAqGKe+EE2yG1ELGNk=,tag:0qoo0tb+xWjjQXr4n1qGmw==,type:str]
|
||||
opencode-go-api-key: ENC[AES256_GCM,data:zbeTcaXJZFVfYnM/7sgblJFU9WfeosX/44KsXvrzKwiLPfGLLYYo9AFaCvWzzG6jHuSZC5OYrBWfOZv4+3omfCgglQ==,iv:LscUQE+PNhXGim9PSqc9nZIZichWSgAn/zsNxQ/HM/o=,tag:MaBCobnRM42fopiibibe5Q==,type:str]
|
||||
zai-coding-plan-api-key: ENC[AES256_GCM,data:osUoFOvBgu+PtNiTIDIm3JoxsBJnQ9I8zY//9oeTpJxIvMctSWYnT4GYP4oI5mClZg==,iv:z5qxUPomGF1avLyk8PrAS3t+34ZGlQMRjbxVJ4JH9Cc=,tag:Qbz/LYAMXejXU4RS3RUPqA==,type:str]
|
||||
netbird-key: ENC[AES256_GCM,data:swmaa+RjxeUmEl8hS2riGrW4lP5jdks9HM3x57/FLpOuqFtR,iv:MrpVjiocrPi+dBGPk7pwgSUNlJ1eryRpMjC8+jkU+T0=,tag:j6sqpQ02apqc6FwkdDvk9g==,type:str]
|
||||
vicinae-json: ENC[AES256_GCM,data:FarBf6l8pl3hF7kGKPIWztUhwiKoQXmyTufCuJ120K/bPh1Bfiyi+ETt4DLYOGI6FJXfpVz4BbZOA29bXTLhVPxH0QtyBu/F5uEqA015b/c8VevDJSyy9huR13qO9ksLbMBt8RfWbAd9j26t7A1C8/mMyiJOEXCCTV9CEIW3xWrsYmhwsT8RYM+PwrPSeN1gQXHSMyRUjf/kOdJoda8+iXpLfjo4II4r2ELpbqi8QxhrRdsJsoOfAymFM784NtlTjE+h6S4TMehmoF/9ARif6I5SGQ0WfIKt/8orTGCPllL+NupLziSnpIGRGSybdArD+o5NCw59GOAbVRADxq8rCESwEkq3cF+hm8HabfYbiQ==,iv:Y/hXLFTJT3gNF3B6tgKoAh7njVuneoUzjVTlsCZiySw=,tag:2hfrwph6IccJdRu/yGu3XA==,type:str]
|
||||
sops:
|
||||
age:
|
||||
- recipient: age14vktfes95f33vuefwnmuvryas7az04u76dsgyhfvsx73czkvmp2q7njkl4
|
||||
enc: |
|
||||
- enc: |
|
||||
-----BEGIN AGE ENCRYPTED FILE-----
|
||||
YWdlLWVuY3J5cHRpb24ub3JnL3YxCi0+IFgyNTUxOSBqS2RZdVJaNTlRamZPMkll
|
||||
MDRVSVl1b2x2LzZpdlBrdmZtdyt3UE15RldRCldXUXE2a1BFeHg5NGNPbW5IMDht
|
||||
@@ -15,8 +15,8 @@ sops:
|
||||
bThQTFdZU29ISm93TWcwVk5ZTkhRWm8KCcprmLGhahgDkXCBpzjctHgao+gc+rKC
|
||||
xLIwheUyFJOGK+ixqcdoZ/PC0kY68hVLt1YzLAyxFi4Ur1wltPrNug==
|
||||
-----END AGE ENCRYPTED FILE-----
|
||||
- recipient: age1x36yr8h993srfj29sfpzt4wyz52nztvncpmhgmfs0j26qvfecq3qvcm0an
|
||||
enc: |
|
||||
recipient: age14vktfes95f33vuefwnmuvryas7az04u76dsgyhfvsx73czkvmp2q7njkl4
|
||||
- enc: |
|
||||
-----BEGIN AGE ENCRYPTED FILE-----
|
||||
YWdlLWVuY3J5cHRpb24ub3JnL3YxCi0+IFgyNTUxOSBGVW13WFE1Ylh3Uk1HNU1i
|
||||
bU9kRzFqTmhkQlRzMlRkM0VhMlNmMDUyK25NCkZYUStxM2tScGozRXJGekxGa1RX
|
||||
@@ -24,7 +24,8 @@ sops:
|
||||
V1N3eUVjZ0VZRjBZdXRPNng3Y3JoUTAKQau9CG9XfvM+5JZVRwaJr/o/sXMaJiy2
|
||||
wo2YcDb+4vfT4Wr+/8J3ccQgbLRZH916X5ZPL+A+nFyVXVKOCl3ENg==
|
||||
-----END AGE ENCRYPTED FILE-----
|
||||
lastmodified: "2026-05-12T06:33:00Z"
|
||||
mac: ENC[AES256_GCM,data:htDJdEx34Q5NG8vwbBimnFENZawbLZ4FC0DkyG6J5RYP0BFnycKcKGsYR87SvIjcJZXvfZ0e6fXdtc78dd6I0sQtrQ7aNn4Iktbu/AkPmntsBwpIjVI99X9zUyQB87go/oX15yuyt8loB6ds2RkL/pfFsgLbFc10JHsBy+WcEzI=,iv:HvY+5LYzyHpRm8XCSKrN8ra/LJT9v23TPSsZg/4QVNU=,tag:k+d45+zgBYq4vlWmmc8ZkQ==,type:str]
|
||||
recipient: age1x36yr8h993srfj29sfpzt4wyz52nztvncpmhgmfs0j26qvfecq3qvcm0an
|
||||
lastmodified: "2026-09-16T14:20:36Z"
|
||||
mac: ENC[AES256_GCM,data:mhJvvn/+VBfNrP1pXRweLSNVlHq9/DLDcKQv8k9ZVsEcd077ifEAqduOXVKXcXDM0VTuBzArw9hmih+kZbCHoUZAQrk8LF7FC4a4FFwXG9p45uKWbUloTuq5w3MCxyU8IoyiAufZcWUlYFQjZ8K4n8N0bVrGQGHogemnrBXTUIo=,iv:H3tKQOuIe/pEIp0pUWCSar8VDompXNZ4BZfD1Wg4pb0=,tag:lyPR4Prlal1bpSRLmGfy7A==,type:str]
|
||||
unencrypted_suffix: _unencrypted
|
||||
version: 3.12.2
|
||||
version: 3.13.3
|
||||
|
||||
@@ -1,133 +1,162 @@
|
||||
{ config, ... }:
|
||||
{
|
||||
flake.modules.nixos.sirius =
|
||||
{
|
||||
pkgs,
|
||||
hostName,
|
||||
userName,
|
||||
...
|
||||
}:
|
||||
{
|
||||
imports = with config.flake.modules.nixos; [
|
||||
boot
|
||||
networking
|
||||
desktop
|
||||
gaming
|
||||
virtualisation
|
||||
];
|
||||
{config, ...}: {
|
||||
flake.modules.nixos.sirius = {
|
||||
pkgs,
|
||||
hostName,
|
||||
userName,
|
||||
...
|
||||
}: {
|
||||
imports = with config.flake.modules.nixos; [
|
||||
boot
|
||||
networking
|
||||
desktop
|
||||
gaming
|
||||
virtualisation
|
||||
];
|
||||
|
||||
tnix = {
|
||||
boot = {
|
||||
secure-boot.enable = true;
|
||||
tnix = {
|
||||
boot = {
|
||||
secure-boot.enable = true;
|
||||
|
||||
impermanence = {
|
||||
enable = true;
|
||||
impermanence = {
|
||||
enable = true;
|
||||
|
||||
home = {
|
||||
directories = [
|
||||
"Distrobox"
|
||||
".steam"
|
||||
".cache/awww"
|
||||
".config/BraveSoftware"
|
||||
".config/zed"
|
||||
".config/Vencord"
|
||||
".config/vesktop"
|
||||
".config/sops"
|
||||
".config/obs-studio"
|
||||
".config/easyeffects"
|
||||
".config/DankMaterialShell"
|
||||
".local/share/Steam"
|
||||
".local/share/nvim"
|
||||
".local/share/opencode"
|
||||
".local/share/zsh"
|
||||
".local/share/zoxide"
|
||||
".local/state/lazygit"
|
||||
".local/share/vicinae"
|
||||
".local/share/TelegramDesktop"
|
||||
];
|
||||
home = {
|
||||
directories = [
|
||||
"Distrobox"
|
||||
".steam"
|
||||
".bun"
|
||||
".rustup"
|
||||
".cache/awww"
|
||||
".cache/serpantinum"
|
||||
".config/BraveSoftware"
|
||||
".config/zed"
|
||||
".config/Vencord"
|
||||
".config/vesktop"
|
||||
".config/sops"
|
||||
".config/nix"
|
||||
".config/coderv2"
|
||||
".config/obs-studio"
|
||||
".config/easyeffects"
|
||||
".config/DankMaterialShell"
|
||||
".local/share/Steam"
|
||||
".local/share/lutris"
|
||||
".local/share/net.lutris.Lutris"
|
||||
".local/share/nvim"
|
||||
".local/share/opencode"
|
||||
".local/share/zsh"
|
||||
".local/share/zoxide"
|
||||
".local/share/voxtype"
|
||||
".local/state/lazygit"
|
||||
".local/share/vicinae"
|
||||
".local/share/TelegramDesktop"
|
||||
".local/share/GalaxyBudsClient"
|
||||
".local/state/serpantinum"
|
||||
".local/share/zed"
|
||||
|
||||
files = [
|
||||
".wakatime.cfg"
|
||||
".config/lan-mouse/lan-mouse.pem"
|
||||
];
|
||||
};
|
||||
".claude"
|
||||
".orca"
|
||||
".config/orca"
|
||||
".zcode"
|
||||
".config/ZCode"
|
||||
];
|
||||
|
||||
files = [
|
||||
".wakatime.cfg"
|
||||
".config/lan-mouse/lan-mouse.pem"
|
||||
".claude.json"
|
||||
".config/gh/hosts.yml"
|
||||
];
|
||||
};
|
||||
};
|
||||
|
||||
networking = {
|
||||
openssh.enable = true;
|
||||
netbird-client.enable = true;
|
||||
};
|
||||
|
||||
virtualisation = {
|
||||
docker.enable = true;
|
||||
docker.nvidia.enable = true;
|
||||
qemu.enable = true;
|
||||
waydroid.enable = true;
|
||||
distrobox.enable = true;
|
||||
};
|
||||
};
|
||||
|
||||
sops.secrets = {
|
||||
tux-password = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
neededForUsers = true;
|
||||
};
|
||||
|
||||
gemini-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
openrouter-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
opencode-go-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
netbird-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
vicinae-json = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
};
|
||||
|
||||
# --- Networking ---
|
||||
networking = {
|
||||
hostName = hostName;
|
||||
networkmanager = {
|
||||
enable = true;
|
||||
wifi.backend = "iwd";
|
||||
};
|
||||
wireless.iwd = {
|
||||
enable = true;
|
||||
settings = {
|
||||
Network = {
|
||||
EnableIPv6 = true;
|
||||
};
|
||||
Settings = {
|
||||
AutoConnect = true;
|
||||
};
|
||||
};
|
||||
};
|
||||
firewall.enable = false;
|
||||
openssh.enable = true;
|
||||
netbird-client.enable = true;
|
||||
};
|
||||
|
||||
environment.systemPackages = with pkgs; [
|
||||
davinci-resolve
|
||||
telegram-desktop
|
||||
];
|
||||
virtualisation = {
|
||||
docker.enable = true;
|
||||
docker.nvidia.enable = true;
|
||||
qemu.enable = true;
|
||||
waydroid.enable = true;
|
||||
distrobox.enable = true;
|
||||
};
|
||||
|
||||
# !!! DO NOT CHANGE THIS !!!
|
||||
# This should match the version used at initial install.
|
||||
system.stateVersion = "26.05";
|
||||
programs.nix-ld.enable = true;
|
||||
};
|
||||
|
||||
sops.secrets = {
|
||||
tux-password = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
neededForUsers = true;
|
||||
};
|
||||
|
||||
gemini-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
openrouter-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
opencode-go-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
zai-coding-plan-api-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
netbird-key = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
|
||||
vicinae-json = {
|
||||
sopsFile = ./secrets.yaml;
|
||||
owner = userName;
|
||||
};
|
||||
};
|
||||
|
||||
# --- Networking ---
|
||||
networking = {
|
||||
hostName = hostName;
|
||||
networkmanager = {
|
||||
enable = true;
|
||||
wifi.backend = "iwd";
|
||||
};
|
||||
wireless.iwd = {
|
||||
enable = true;
|
||||
settings = {
|
||||
Network = {
|
||||
EnableIPv6 = true;
|
||||
};
|
||||
Settings = {
|
||||
AutoConnect = true;
|
||||
};
|
||||
};
|
||||
};
|
||||
firewall.enable = false;
|
||||
};
|
||||
|
||||
environment.systemPackages = with pkgs; [
|
||||
davinci-resolve
|
||||
telegram-desktop
|
||||
galaxy-buds-client
|
||||
impala
|
||||
llm-agents.claude-code
|
||||
llm-agents.orca
|
||||
llm-agents.zcode
|
||||
coder
|
||||
];
|
||||
|
||||
# !!! DO NOT CHANGE THIS !!!
|
||||
# This should match the version used at initial install.
|
||||
system.stateVersion = "26.05";
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,49 +1,50 @@
|
||||
{ inputs, ... }:
|
||||
{
|
||||
flake.modules.nixos.sirius =
|
||||
{ config, lib, ... }:
|
||||
let
|
||||
hasOptinPersistence = config.tnix.boot.impermanence.enable;
|
||||
in
|
||||
{
|
||||
imports = [
|
||||
inputs.disko.nixosModules.disko
|
||||
];
|
||||
{inputs, ...}: {
|
||||
flake.modules.nixos.sirius = {
|
||||
config,
|
||||
lib,
|
||||
...
|
||||
}: let
|
||||
hasOptinPersistence = config.tnix.boot.impermanence.enable;
|
||||
in {
|
||||
imports = [
|
||||
inputs.disko.nixosModules.disko
|
||||
];
|
||||
|
||||
disko.devices.disk.primary = {
|
||||
device = "/dev/nvme1n1";
|
||||
type = "disk";
|
||||
content = {
|
||||
type = "gpt";
|
||||
partitions = {
|
||||
ESP = {
|
||||
size = "1G";
|
||||
type = "EF00";
|
||||
content = {
|
||||
type = "filesystem";
|
||||
format = "vfat";
|
||||
mountpoint = "/boot";
|
||||
mountOptions = [
|
||||
"defaults"
|
||||
"umask=0077"
|
||||
];
|
||||
};
|
||||
disko.devices.disk.primary = {
|
||||
device = "/dev/nvme1n1";
|
||||
type = "disk";
|
||||
content = {
|
||||
type = "gpt";
|
||||
partitions = {
|
||||
ESP = {
|
||||
size = "1G";
|
||||
type = "EF00";
|
||||
content = {
|
||||
type = "filesystem";
|
||||
format = "vfat";
|
||||
mountpoint = "/boot";
|
||||
mountOptions = [
|
||||
"defaults"
|
||||
"umask=0077"
|
||||
];
|
||||
};
|
||||
swap = {
|
||||
size = "70G";
|
||||
content = {
|
||||
type = "swap";
|
||||
discardPolicy = "both";
|
||||
resumeDevice = true;
|
||||
};
|
||||
};
|
||||
swap = {
|
||||
size = "70G";
|
||||
content = {
|
||||
type = "swap";
|
||||
discardPolicy = "both";
|
||||
resumeDevice = true;
|
||||
};
|
||||
root = {
|
||||
size = "100%";
|
||||
type = "8300";
|
||||
content = {
|
||||
type = "btrfs";
|
||||
# Base subvolumes that always exist
|
||||
subvolumes = {
|
||||
};
|
||||
root = {
|
||||
size = "100%";
|
||||
type = "8300";
|
||||
content = {
|
||||
type = "btrfs";
|
||||
# Base subvolumes that always exist
|
||||
subvolumes =
|
||||
{
|
||||
"/root" = {
|
||||
mountOptions = [
|
||||
"compress=zstd"
|
||||
@@ -73,10 +74,10 @@
|
||||
mountpoint = "/persist";
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,61 +1,61 @@
|
||||
{ inputs, config, ... }:
|
||||
{
|
||||
flake.modules.nixos.sirius =
|
||||
{
|
||||
lib,
|
||||
pkgs,
|
||||
system,
|
||||
...
|
||||
}@innerArgs:
|
||||
{
|
||||
imports =
|
||||
with config.flake.modules.nixos;
|
||||
[
|
||||
hardware
|
||||
]
|
||||
++ [
|
||||
inputs.cardwire.nixosModules.default
|
||||
];
|
||||
|
||||
boot.kernelParams = [ "nvidia-drm.modeset=1" ];
|
||||
boot.initrd.availableKernelModules = [
|
||||
"nvme"
|
||||
"xhci_pci"
|
||||
"ahci"
|
||||
"usbhid"
|
||||
"usb_storage"
|
||||
"sd_mod"
|
||||
inputs,
|
||||
config,
|
||||
...
|
||||
}: {
|
||||
flake.modules.nixos.sirius = {
|
||||
lib,
|
||||
pkgs,
|
||||
system,
|
||||
...
|
||||
} @ innerArgs: {
|
||||
imports = with config.flake.modules.nixos;
|
||||
[
|
||||
hardware
|
||||
]
|
||||
++ [
|
||||
inputs.cardwire.nixosModules.default
|
||||
];
|
||||
boot.initrd.kernelModules = [ ];
|
||||
boot.kernelModules = [ "kvm-amd" ];
|
||||
boot.extraModulePackages = [ ];
|
||||
|
||||
hardware = {
|
||||
nvidia = {
|
||||
modesetting.enable = true;
|
||||
open = false;
|
||||
nvidiaSettings = true;
|
||||
};
|
||||
boot.kernelParams = ["nvidia-drm.modeset=1"];
|
||||
boot.initrd.availableKernelModules = [
|
||||
"nvme"
|
||||
"xhci_pci"
|
||||
"ahci"
|
||||
"usbhid"
|
||||
"usb_storage"
|
||||
"sd_mod"
|
||||
];
|
||||
boot.initrd.kernelModules = [];
|
||||
boot.kernelModules = ["kvm-amd"];
|
||||
boot.extraModulePackages = [];
|
||||
|
||||
cpu.amd.updateMicrocode = lib.mkDefault innerArgs.config.hardware.enableRedistributableFirmware;
|
||||
hardware = {
|
||||
nvidia = {
|
||||
modesetting.enable = true;
|
||||
open = false;
|
||||
nvidiaSettings = true;
|
||||
};
|
||||
|
||||
services = {
|
||||
xserver.videoDrivers = [ "nvidia" ];
|
||||
power-profiles-daemon.enable = true;
|
||||
|
||||
cardwire = {
|
||||
enable = true;
|
||||
settings.auto_apply_gpu_state = true;
|
||||
};
|
||||
};
|
||||
|
||||
networking.useDHCP = lib.mkDefault true;
|
||||
nixpkgs.config.cudaSupport = true;
|
||||
nixpkgs.hostPlatform = lib.mkDefault system;
|
||||
|
||||
environment.systemPackages = with pkgs; [
|
||||
nvtopPackages.full
|
||||
];
|
||||
cpu.amd.updateMicrocode = lib.mkDefault innerArgs.config.hardware.enableRedistributableFirmware;
|
||||
};
|
||||
|
||||
services = {
|
||||
xserver.videoDrivers = ["nvidia"];
|
||||
power-profiles-daemon.enable = true;
|
||||
|
||||
cardwire = {
|
||||
enable = true;
|
||||
settings.auto_apply_gpu_state = true;
|
||||
};
|
||||
};
|
||||
|
||||
networking.useDHCP = lib.mkDefault true;
|
||||
nixpkgs.config.cudaSupport = true;
|
||||
nixpkgs.hostPlatform = lib.mkDefault system;
|
||||
|
||||
environment.systemPackages = with pkgs; [
|
||||
nvtopPackages.full
|
||||
];
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,5 +1,4 @@
|
||||
{ config, ... }:
|
||||
{
|
||||
{config, ...}: {
|
||||
flake.modules.homeManager.sirius = {
|
||||
imports = with config.flake.modules.homeManager; [
|
||||
desktop
|
||||
@@ -45,7 +44,7 @@
|
||||
position = "bottom";
|
||||
hostname = "canopus";
|
||||
activate_on_startup = true;
|
||||
ips = [ "192.168.8.2" ];
|
||||
ips = ["192.168.8.2"];
|
||||
}
|
||||
];
|
||||
};
|
||||
|
||||
@@ -2,12 +2,12 @@ tux-password: ENC[AES256_GCM,data:JWQVd2MYX2U4UP4II62ixG9hWI5MtgHAFhl8aCmyrYPl1H
|
||||
gemini-api-key: ENC[AES256_GCM,data:Y9YgXp/tB3Q1Rb5YMsZLgWCq+bdeIjsXAVeO3Yh7nZ8MwDH7d5De,iv:FIXxJCn6JDYsHIoNn8f8Un3z9ZPVbxdjR48Ux88poRg=,tag:bMJ4i69HTspnhzsrsxkbrw==,type:str]
|
||||
openrouter-api-key: ENC[AES256_GCM,data:HfZgZz4NyCLLM9woTZp2I6JGOlVcFblw2OMjx8k0TG5ZU2ycBCF6bKqp3wFibUxXcHy+nIfjI82fkLeSyIaGILRLYCJCc8BHKw==,iv:umUcn8MRaj7JXo6IFrGMXOu+jsFSCEikMxsQxfaFS/Q=,tag:l2s61C4EpJoKv8cc9nYGFA==,type:str]
|
||||
opencode-go-api-key: ENC[AES256_GCM,data:BGERcZg5Jpnznc4cXeYFMhPk9kKBkd9GvIuQBV9TW3JE1utgrLLYK6mKNCQqrEStRFiO2jUUnBm3opUNL4SuEHFLpw==,iv:fgFAwx6z9yruK27PvAJX/Q2CS9gU+LJ5zMUK/f/rzpo=,tag:BPu3M+jppPB8sLoLmfuY/Q==,type:str]
|
||||
zai-coding-plan-api-key: ENC[AES256_GCM,data:u5RHaBq5WHit+GjcKYnr6vN7jkputBtt3G0lCNBciMgBnBzIcZd/JjJcNaKXfbal5w==,iv:x+mG1aoct7yfm4Hvu1mMqBq8MiF8UZbQ8SFjA99qTIw=,tag:9cEIO2tuhqE6df2M2N/R+g==,type:str]
|
||||
netbird-key: ENC[AES256_GCM,data:qXAnRnLM2TlzpOvWG4exJv0+pUvpe0FpRN5xOWx3+KNt+yhq,iv:X+yl4o1RSYMCMWdVXo1hpzy+6IdKXUpsKPtYNSiHiCY=,tag:I8HbnD5iw6EJ1TdsNrhvfw==,type:str]
|
||||
vicinae-json: ENC[AES256_GCM,data:JjxolEgS6uakqR4eHOx3VyrOO5kaL4dj1jcEiLWsrktCU32UB7OmP1kJEVomA1rZjODpFHL89+FRpcNFspTFrc365WlANE81RLg/M2Ja1MiLYaDFNcBGtqMX9Yc1muor53Xl7t+rTSvDIj1oE1L7xPPcjCLfwC5QDzJjCBWj9FhCxnU5BwvoJNv9vgA6xnkzAOYSPZK/ihULMD0DxyqOUEa5ECGX62OPM9Gbr7jEviaItYzOOxaRs/yQVqizodGGl/BcK6fPqvOYSxip9ABYRVSI9ZvysY7ofAkeX91ardPwVG5VvEYfxZwBvGFjV7ZfTzVkK+BiUUNrvciAETHqwkjHftPpfJjxWsgLr8lbOA==,iv:HjDE/sqVDnxeww7r2upxH57rc1+LpuMKnhhyGXoc1Ms=,tag:d2kZeWkg17eVoNACIQ3Q9A==,type:str]
|
||||
sops:
|
||||
age:
|
||||
- recipient: age14vktfes95f33vuefwnmuvryas7az04u76dsgyhfvsx73czkvmp2q7njkl4
|
||||
enc: |
|
||||
- enc: |
|
||||
-----BEGIN AGE ENCRYPTED FILE-----
|
||||
YWdlLWVuY3J5cHRpb24ub3JnL3YxCi0+IFgyNTUxOSBQNGdHcDc4bTFkR0EyZlUr
|
||||
eXovR1lyeTZJTDg5R281MFFuMHVwOXZXYzNvCkpIT1g3K05WUUswaEVjVVJWQkJq
|
||||
@@ -15,8 +15,8 @@ sops:
|
||||
Z0JwWWR0STUybjVhSXdDR3NiKzV1eDQK22HmMuyqYaR/eGuALkAPB1Y5bN2KwIt3
|
||||
pamM8vbnjB//hXoyrv4vsoDk9WzLGFGjgiw2qsM2HQgzQqtrwF1/1A==
|
||||
-----END AGE ENCRYPTED FILE-----
|
||||
- recipient: age1maxsx5tq2h3d92rfyl8ekcdan5gu5cpch4qs3c56cu7qag02xgvs3h0gqc
|
||||
enc: |
|
||||
recipient: age14vktfes95f33vuefwnmuvryas7az04u76dsgyhfvsx73czkvmp2q7njkl4
|
||||
- enc: |
|
||||
-----BEGIN AGE ENCRYPTED FILE-----
|
||||
YWdlLWVuY3J5cHRpb24ub3JnL3YxCi0+IFgyNTUxOSA1N3ZBd1pHODFtZkZxaHNP
|
||||
OXlXUzVFS0ZIam1IWVkxNldOdTEwY0s4aUNZCjVlcnF1aXJxUUlQSXhteXJ6OU1W
|
||||
@@ -24,7 +24,8 @@ sops:
|
||||
M3JocWZJeXFxenhXOENBVWpvNkd3bm8KqhNLzCyEAI643jGWpZF/uTchHmBj8ozU
|
||||
HtpOzKsshif66D0XOHeJQfQamJI4TyKsj3Sk3j9rstsLmN2lxTRGHg==
|
||||
-----END AGE ENCRYPTED FILE-----
|
||||
lastmodified: "2026-05-10T00:35:50Z"
|
||||
mac: ENC[AES256_GCM,data:u27zQ1PPnWy5Parbh/1DkVP3ICmHnLZJKaLbN3dZEVONgqOWi32LV3t0iNhtLWwVnzFPBusRWahQiqAkUdnQtrXF0OtjPCpLuIw86xB75QPGbet0GZlLNb8/xPshChZe4v520csdJMWiy3vYeKrk8LxMSViAGhmhYK2a5NbGhzI=,iv:/9vePmvCNqoP0kx24fP3HfCjS2FkjBmI5B+SycvKKW4=,tag:gE1/DnLolwhoyfMJYejGIQ==,type:str]
|
||||
recipient: age1maxsx5tq2h3d92rfyl8ekcdan5gu5cpch4qs3c56cu7qag02xgvs3h0gqc
|
||||
lastmodified: "2026-09-16T14:20:48Z"
|
||||
mac: ENC[AES256_GCM,data:i2I6vo/tKTLq44Tu6vI2Cqp0EqQPbwuuRM2WUflD58UCr7huXIKnKrxmB1Hz/fdmpZPiCZ2dSlmOh733fKFclRmpHJLScYRX4+lFXEzToYExZlybVergxC6Cr4IaiB+A/HZIkW6iKK/ULr2mtXYNCqQgDQw8BgJuV2M/bAMM/V4=,iv:9akzmVH4CMMdDS5aukeLOxncMLKfvQCw2BYl36WAfOM=,tag:4F26bqEI8fEtNugqjHCUOg==,type:str]
|
||||
unencrypted_suffix: _unencrypted
|
||||
version: 3.12.2
|
||||
version: 3.13.3
|
||||
|
||||
@@ -1,56 +1,51 @@
|
||||
{ config, ... }:
|
||||
{
|
||||
flake.modules.nixOnDroid.vega =
|
||||
{
|
||||
pkgs,
|
||||
userEmail,
|
||||
...
|
||||
}:
|
||||
{
|
||||
imports = with config.flake.modules.nixOnDroid; [
|
||||
networking
|
||||
{config, ...}: {
|
||||
flake.modules.nixOnDroid.vega = {
|
||||
pkgs,
|
||||
userEmail,
|
||||
...
|
||||
}: {
|
||||
imports = with config.flake.modules.nixOnDroid; [
|
||||
networking
|
||||
];
|
||||
|
||||
# @TODO: Broken currently
|
||||
# android-integration.am.enable = true;
|
||||
# android-integration.termux-open-url.enable = true;
|
||||
# android-integration.xdg-open.enable = true;
|
||||
# android-integration.termux-setup-storage.enable = true;
|
||||
# android-integration.termux-reload-settings.enable = true;
|
||||
|
||||
terminal.font = let
|
||||
firacode = pkgs.nerd-fonts.fira-code;
|
||||
fontPath = "share/fonts/truetype/NerdFonts/FiraCode/FiraCodeNerdFont-Regular.ttf";
|
||||
in "${firacode}/${fontPath}";
|
||||
|
||||
time.timeZone = "Asia/Kolkata";
|
||||
|
||||
tnix.networking.openssh = {
|
||||
enable = true;
|
||||
ports = [8033];
|
||||
authorizedKeys = [
|
||||
"ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIL+OzPUe2ECPC929DqpkM39tl/vdNAXfsRnmrGfR+X3D ${userEmail}"
|
||||
];
|
||||
|
||||
# @TODO: Broken currently
|
||||
# android-integration.am.enable = true;
|
||||
# android-integration.termux-open-url.enable = true;
|
||||
# android-integration.xdg-open.enable = true;
|
||||
# android-integration.termux-setup-storage.enable = true;
|
||||
# android-integration.termux-reload-settings.enable = true;
|
||||
|
||||
terminal.font =
|
||||
let
|
||||
firacode = pkgs.nerd-fonts.fira-code;
|
||||
fontPath = "share/fonts/truetype/NerdFonts/FiraCode/FiraCodeNerdFont-Regular.ttf";
|
||||
in
|
||||
"${firacode}/${fontPath}";
|
||||
|
||||
time.timeZone = "Asia/Kolkata";
|
||||
|
||||
tnix.networking.openssh = {
|
||||
enable = true;
|
||||
ports = [ 8033 ];
|
||||
authorizedKeys = [
|
||||
"ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIL+OzPUe2ECPC929DqpkM39tl/vdNAXfsRnmrGfR+X3D ${userEmail}"
|
||||
];
|
||||
};
|
||||
|
||||
user = {
|
||||
uid = 10481;
|
||||
gid = 10481;
|
||||
shell = "${pkgs.zsh}/bin/zsh";
|
||||
};
|
||||
|
||||
environment.etcBackupExtension = ".backup";
|
||||
environment.motd = "";
|
||||
environment.packages = with pkgs; [
|
||||
ncurses
|
||||
procps
|
||||
util-linux
|
||||
rsync
|
||||
gnutar
|
||||
];
|
||||
|
||||
system.stateVersion = "24.05";
|
||||
};
|
||||
|
||||
user = {
|
||||
uid = 10481;
|
||||
gid = 10481;
|
||||
shell = "${pkgs.zsh}/bin/zsh";
|
||||
};
|
||||
|
||||
environment.etcBackupExtension = ".backup";
|
||||
environment.motd = "";
|
||||
environment.packages = with pkgs; [
|
||||
ncurses
|
||||
procps
|
||||
util-linux
|
||||
rsync
|
||||
gnutar
|
||||
];
|
||||
|
||||
system.stateVersion = "24.05";
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,5 +1,4 @@
|
||||
{ lib, ... }:
|
||||
{
|
||||
{lib, ...}: {
|
||||
flake.modules.homeManager.vega = {
|
||||
# @TODO: Broken currently - By default it's enabled by neovim module
|
||||
programs.vim.enable = lib.mkForce false;
|
||||
|
||||
@@ -1,50 +1,44 @@
|
||||
{ config, ... }:
|
||||
{
|
||||
flake.modules.nixos.vps =
|
||||
{
|
||||
hostName,
|
||||
...
|
||||
}:
|
||||
{
|
||||
imports = with config.flake.modules.nixos; [
|
||||
boot
|
||||
networking
|
||||
virtualisation
|
||||
services
|
||||
];
|
||||
{config, ...}: {
|
||||
flake.modules.nixos.vps = {hostName, ...}: {
|
||||
imports = with config.flake.modules.nixos; [
|
||||
boot
|
||||
networking
|
||||
virtualisation
|
||||
services
|
||||
];
|
||||
|
||||
tnix = {
|
||||
boot = {
|
||||
legacy.enable = true;
|
||||
tnix = {
|
||||
boot = {
|
||||
legacy.enable = true;
|
||||
|
||||
impermanence = {
|
||||
enable = true;
|
||||
impermanence = {
|
||||
enable = true;
|
||||
|
||||
home = {
|
||||
directories = [
|
||||
".local/share/nvim"
|
||||
".local/share/zsh"
|
||||
".local/share/zoxide"
|
||||
".local/state/lazygit"
|
||||
];
|
||||
};
|
||||
home = {
|
||||
directories = [
|
||||
".local/share/nvim"
|
||||
".local/share/zsh"
|
||||
".local/share/zoxide"
|
||||
".local/state/lazygit"
|
||||
];
|
||||
};
|
||||
};
|
||||
|
||||
networking.openssh.enable = true;
|
||||
|
||||
virtualisation = {
|
||||
docker.enable = true;
|
||||
};
|
||||
};
|
||||
|
||||
# --- Networking ---
|
||||
networking = {
|
||||
hostName = hostName;
|
||||
networkmanager.enable = true;
|
||||
firewall.enable = false;
|
||||
};
|
||||
networking.openssh.enable = true;
|
||||
|
||||
system.stateVersion = "26.05";
|
||||
virtualisation = {
|
||||
docker.enable = true;
|
||||
};
|
||||
};
|
||||
|
||||
# --- Networking ---
|
||||
networking = {
|
||||
hostName = hostName;
|
||||
networkmanager.enable = true;
|
||||
firewall.enable = false;
|
||||
};
|
||||
|
||||
system.stateVersion = "26.05";
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,22 +1,23 @@
|
||||
{ inputs, ... }:
|
||||
{
|
||||
flake.modules.nixos.vps =
|
||||
{ config, lib, ... }:
|
||||
let
|
||||
hasOptinPersistence = config.tnix.boot.impermanence.enable;
|
||||
isLegacy = config.tnix.boot.legacy.enable;
|
||||
in
|
||||
{
|
||||
imports = [
|
||||
inputs.disko.nixosModules.disko
|
||||
];
|
||||
{inputs, ...}: {
|
||||
flake.modules.nixos.vps = {
|
||||
config,
|
||||
lib,
|
||||
...
|
||||
}: let
|
||||
hasOptinPersistence = config.tnix.boot.impermanence.enable;
|
||||
isLegacy = config.tnix.boot.legacy.enable;
|
||||
in {
|
||||
imports = [
|
||||
inputs.disko.nixosModules.disko
|
||||
];
|
||||
|
||||
disko.devices.disk.primary = {
|
||||
device = "/dev/sda";
|
||||
type = "disk";
|
||||
content = {
|
||||
type = "gpt";
|
||||
partitions = {
|
||||
disko.devices.disk.primary = {
|
||||
device = "/dev/sda";
|
||||
type = "disk";
|
||||
content = {
|
||||
type = "gpt";
|
||||
partitions =
|
||||
{
|
||||
ESP = {
|
||||
size = "1G";
|
||||
type = "EF00";
|
||||
@@ -36,36 +37,37 @@
|
||||
content = {
|
||||
type = "btrfs";
|
||||
# Base subvolumes that always exist
|
||||
subvolumes = {
|
||||
"/root" = {
|
||||
mountOptions = [
|
||||
"compress=zstd"
|
||||
"noatime"
|
||||
"space_cache=v2"
|
||||
];
|
||||
mountpoint = "/";
|
||||
subvolumes =
|
||||
{
|
||||
"/root" = {
|
||||
mountOptions = [
|
||||
"compress=zstd"
|
||||
"noatime"
|
||||
"space_cache=v2"
|
||||
];
|
||||
mountpoint = "/";
|
||||
};
|
||||
"/nix" = {
|
||||
mountOptions = [
|
||||
"compress=zstd"
|
||||
"noatime"
|
||||
"noacl"
|
||||
"space_cache=v2"
|
||||
];
|
||||
mountpoint = "/nix";
|
||||
};
|
||||
}
|
||||
# Conditionally merge /persist only when impermanence is enabled
|
||||
// lib.optionalAttrs hasOptinPersistence {
|
||||
"/persist" = {
|
||||
mountOptions = [
|
||||
"compress=zstd"
|
||||
"noatime"
|
||||
"space_cache=v2"
|
||||
];
|
||||
mountpoint = "/persist";
|
||||
};
|
||||
};
|
||||
"/nix" = {
|
||||
mountOptions = [
|
||||
"compress=zstd"
|
||||
"noatime"
|
||||
"noacl"
|
||||
"space_cache=v2"
|
||||
];
|
||||
mountpoint = "/nix";
|
||||
};
|
||||
}
|
||||
# Conditionally merge /persist only when impermanence is enabled
|
||||
// lib.optionalAttrs hasOptinPersistence {
|
||||
"/persist" = {
|
||||
mountOptions = [
|
||||
"compress=zstd"
|
||||
"noatime"
|
||||
"space_cache=v2"
|
||||
];
|
||||
mountpoint = "/persist";
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
@@ -76,7 +78,7 @@
|
||||
type = "EF02";
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,17 +1,15 @@
|
||||
{
|
||||
flake.modules.nixos.vps =
|
||||
{
|
||||
lib,
|
||||
modulesPath,
|
||||
system,
|
||||
...
|
||||
}:
|
||||
{
|
||||
imports = [
|
||||
(modulesPath + "/profiles/qemu-guest.nix")
|
||||
];
|
||||
flake.modules.nixos.vps = {
|
||||
lib,
|
||||
modulesPath,
|
||||
system,
|
||||
...
|
||||
}: {
|
||||
imports = [
|
||||
(modulesPath + "/profiles/qemu-guest.nix")
|
||||
];
|
||||
|
||||
networking.useDHCP = lib.mkDefault true;
|
||||
nixpkgs.hostPlatform = lib.mkDefault system;
|
||||
};
|
||||
networking.useDHCP = lib.mkDefault true;
|
||||
nixpkgs.hostPlatform = lib.mkDefault system;
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,71 +1,71 @@
|
||||
{ inputs, ... }:
|
||||
{
|
||||
flake.modules.nixos.boot =
|
||||
{
|
||||
config,
|
||||
lib,
|
||||
userName,
|
||||
...
|
||||
}:
|
||||
let
|
||||
cfg = config.tnix.boot;
|
||||
in
|
||||
{
|
||||
imports = [
|
||||
inputs.impermanence.nixosModules.impermanence
|
||||
];
|
||||
{inputs, ...}: {
|
||||
flake.modules.nixos.boot = {
|
||||
config,
|
||||
lib,
|
||||
userName,
|
||||
...
|
||||
}: let
|
||||
cfg = config.tnix.boot;
|
||||
in {
|
||||
imports = [
|
||||
inputs.impermanence.nixosModules.impermanence
|
||||
];
|
||||
|
||||
options.tnix.boot.impermanence = {
|
||||
enable = lib.mkEnableOption "Enable impermanence";
|
||||
options.tnix.boot.impermanence = {
|
||||
enable = lib.mkEnableOption "Enable impermanence";
|
||||
|
||||
directories = lib.mkOption {
|
||||
type = lib.types.listOf lib.types.str;
|
||||
default = [ ];
|
||||
};
|
||||
|
||||
files = lib.mkOption {
|
||||
type = lib.types.listOf lib.types.str;
|
||||
default = [ ];
|
||||
};
|
||||
directories = lib.mkOption {
|
||||
type = lib.types.listOf lib.types.str;
|
||||
default = [];
|
||||
};
|
||||
|
||||
options.tnix.boot.impermanence.home = {
|
||||
directories = lib.mkOption {
|
||||
type = lib.types.listOf lib.types.str;
|
||||
default = [ ];
|
||||
};
|
||||
files = lib.mkOption {
|
||||
type = lib.types.listOf lib.types.str;
|
||||
default = [];
|
||||
};
|
||||
};
|
||||
|
||||
files = lib.mkOption {
|
||||
type = lib.types.listOf lib.types.str;
|
||||
default = [ ];
|
||||
};
|
||||
options.tnix.boot.impermanence.home = {
|
||||
directories = lib.mkOption {
|
||||
type = lib.types.listOf lib.types.str;
|
||||
default = [];
|
||||
};
|
||||
|
||||
config = lib.mkIf cfg.impermanence.enable {
|
||||
programs.fuse.userAllowOther = true;
|
||||
fileSystems."/persist".neededForBoot = true;
|
||||
environment.persistence."/persist" = {
|
||||
hideMounts = true;
|
||||
directories = [
|
||||
files = lib.mkOption {
|
||||
type = lib.types.listOf lib.types.str;
|
||||
default = [];
|
||||
};
|
||||
};
|
||||
|
||||
config = lib.mkIf cfg.impermanence.enable {
|
||||
programs.fuse.userAllowOther = true;
|
||||
fileSystems."/persist".neededForBoot = true;
|
||||
environment.persistence."/persist" = {
|
||||
hideMounts = true;
|
||||
directories =
|
||||
[
|
||||
"/var/log"
|
||||
"/var/lib"
|
||||
"/etc/NetworkManager/system-connections"
|
||||
]
|
||||
++ cfg.impermanence.directories;
|
||||
|
||||
files = [
|
||||
files =
|
||||
[
|
||||
"/etc/machine-id"
|
||||
"/etc/ssh/ssh_host_ed25519_key"
|
||||
"/etc/ssh/ssh_host_ed25519_key.pub"
|
||||
"/etc/ssh/ssh_host_rsa_key"
|
||||
"/etc/ssh/ssh_host_rsa_key.pub"
|
||||
"/etc/ly/save.txt"
|
||||
]
|
||||
++ cfg.impermanence.files;
|
||||
};
|
||||
};
|
||||
|
||||
home-manager.users.${userName} = {
|
||||
home.persistence."/persist" = {
|
||||
directories = [
|
||||
home-manager.users.${userName} = {
|
||||
home.persistence."/persist" = {
|
||||
directories =
|
||||
[
|
||||
"Downloads"
|
||||
"Music"
|
||||
"Wallpapers"
|
||||
@@ -77,46 +77,46 @@
|
||||
]
|
||||
++ cfg.impermanence.home.directories;
|
||||
|
||||
files = cfg.impermanence.home.files;
|
||||
};
|
||||
files = cfg.impermanence.home.files;
|
||||
};
|
||||
};
|
||||
|
||||
boot.initrd.systemd = {
|
||||
enable = true;
|
||||
boot.initrd.systemd = {
|
||||
enable = true;
|
||||
|
||||
services.wipe-my-fs = {
|
||||
wantedBy = [ "initrd.target" ];
|
||||
after = [ "initrd-root-device.target" ];
|
||||
before = [ "sysroot.mount" ];
|
||||
unitConfig.DefaultDependencies = "no";
|
||||
serviceConfig.Type = "oneshot";
|
||||
script = ''
|
||||
mkdir /btrfs_tmp
|
||||
mount /dev/disk/by-partlabel/disk-primary-root /btrfs_tmp
|
||||
services.wipe-my-fs = {
|
||||
wantedBy = ["initrd.target"];
|
||||
after = ["initrd-root-device.target"];
|
||||
before = ["sysroot.mount"];
|
||||
unitConfig.DefaultDependencies = "no";
|
||||
serviceConfig.Type = "oneshot";
|
||||
script = ''
|
||||
mkdir /btrfs_tmp
|
||||
mount /dev/disk/by-partlabel/disk-primary-root /btrfs_tmp
|
||||
|
||||
if [[ -e /btrfs_tmp/root ]]; then
|
||||
mkdir -p /btrfs_tmp/old_roots
|
||||
timestamp=$(date --date="@$(stat -c %Y /btrfs_tmp/root)" "+%Y-%m-%-d_%H:%M:%S")
|
||||
mv /btrfs_tmp/root "/btrfs_tmp/old_roots/$timestamp"
|
||||
fi
|
||||
if [[ -e /btrfs_tmp/root ]]; then
|
||||
mkdir -p /btrfs_tmp/old_roots
|
||||
timestamp=$(date --date="@$(stat -c %Y /btrfs_tmp/root)" "+%Y-%m-%-d_%H:%M:%S")
|
||||
mv /btrfs_tmp/root "/btrfs_tmp/old_roots/$timestamp"
|
||||
fi
|
||||
|
||||
delete_subvolume_recursively() {
|
||||
IFS=$'\n'
|
||||
for i in $(btrfs subvolume list -o "$1" | cut -f 9- -d ' '); do
|
||||
delete_subvolume_recursively "/btrfs_tmp/$i"
|
||||
done
|
||||
btrfs subvolume delete "$1"
|
||||
}
|
||||
delete_subvolume_recursively() {
|
||||
IFS=$'\n'
|
||||
for i in $(btrfs subvolume list -o "$1" | cut -f 9- -d ' '); do
|
||||
delete_subvolume_recursively "/btrfs_tmp/$i"
|
||||
done
|
||||
btrfs subvolume delete "$1"
|
||||
}
|
||||
|
||||
for i in $(find /btrfs_tmp/old_roots/ -maxdepth 1 -mtime +30); do
|
||||
delete_subvolume_recursively "$i"
|
||||
done
|
||||
for i in $(find /btrfs_tmp/old_roots/ -maxdepth 1 -mtime +30); do
|
||||
delete_subvolume_recursively "$i"
|
||||
done
|
||||
|
||||
btrfs subvolume create /btrfs_tmp/root
|
||||
umount /btrfs_tmp
|
||||
'';
|
||||
};
|
||||
btrfs subvolume create /btrfs_tmp/root
|
||||
umount /btrfs_tmp
|
||||
'';
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,31 +1,32 @@
|
||||
{
|
||||
flake.modules.nixos.boot =
|
||||
{ config, lib, ... }:
|
||||
let
|
||||
cfg = config.tnix.boot;
|
||||
in
|
||||
{
|
||||
options.tnix.boot.legacy = {
|
||||
enable = lib.mkEnableOption "legacy boot (GRUB) instead of systemd-boot";
|
||||
};
|
||||
|
||||
config = lib.mkMerge [
|
||||
{
|
||||
boot.binfmt.emulatedSystems = [ "aarch64-linux" ];
|
||||
|
||||
boot.loader = {
|
||||
timeout = 1;
|
||||
efi.canTouchEfiVariables = true;
|
||||
};
|
||||
}
|
||||
|
||||
(lib.mkIf (!cfg.legacy.enable && !cfg.secure-boot.enable) {
|
||||
boot.loader.systemd-boot.enable = true;
|
||||
})
|
||||
|
||||
(lib.mkIf cfg.legacy.enable {
|
||||
boot.loader.grub.enable = true;
|
||||
})
|
||||
];
|
||||
flake.modules.nixos.boot = {
|
||||
config,
|
||||
lib,
|
||||
...
|
||||
}: let
|
||||
cfg = config.tnix.boot;
|
||||
in {
|
||||
options.tnix.boot.legacy = {
|
||||
enable = lib.mkEnableOption "legacy boot (GRUB) instead of systemd-boot";
|
||||
};
|
||||
|
||||
config = lib.mkMerge [
|
||||
{
|
||||
boot.binfmt.emulatedSystems = ["aarch64-linux"];
|
||||
|
||||
boot.loader = {
|
||||
timeout = 1;
|
||||
efi.canTouchEfiVariables = true;
|
||||
};
|
||||
}
|
||||
|
||||
(lib.mkIf (!cfg.legacy.enable && !cfg.secure-boot.enable) {
|
||||
boot.loader.systemd-boot.enable = true;
|
||||
})
|
||||
|
||||
(lib.mkIf cfg.legacy.enable {
|
||||
boot.loader.grub.enable = true;
|
||||
})
|
||||
];
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,12 +1,10 @@
|
||||
{
|
||||
flake.modules.nixos.boot =
|
||||
{ pkgs, ... }:
|
||||
{
|
||||
boot = {
|
||||
consoleLogLevel = 0;
|
||||
initrd.verbose = false;
|
||||
kernelPackages = pkgs.linuxPackages_zen;
|
||||
supportedFilesystems = [ "ntfs" ];
|
||||
};
|
||||
flake.modules.nixos.boot = {pkgs, ...}: {
|
||||
boot = {
|
||||
consoleLogLevel = 0;
|
||||
initrd.verbose = false;
|
||||
kernelPackages = pkgs.linuxPackages_zen;
|
||||
supportedFilesystems = ["ntfs"];
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,43 +1,39 @@
|
||||
{ inputs, ... }:
|
||||
{
|
||||
flake.modules.nixos.boot =
|
||||
{
|
||||
config,
|
||||
lib,
|
||||
pkgs,
|
||||
...
|
||||
}:
|
||||
let
|
||||
cfg = config.tnix.boot;
|
||||
in
|
||||
{
|
||||
imports = [ inputs.lanzaboote.nixosModules.lanzaboote ];
|
||||
{inputs, ...}: {
|
||||
flake.modules.nixos.boot = {
|
||||
config,
|
||||
lib,
|
||||
pkgs,
|
||||
...
|
||||
}: let
|
||||
cfg = config.tnix.boot;
|
||||
in {
|
||||
imports = [inputs.lanzaboote.nixosModules.lanzaboote];
|
||||
|
||||
options.tnix.boot.secure-boot = {
|
||||
enable = lib.mkEnableOption "Enable secure-boot";
|
||||
};
|
||||
options.tnix.boot.secure-boot = {
|
||||
enable = lib.mkEnableOption "Enable secure-boot";
|
||||
};
|
||||
|
||||
config = lib.mkIf cfg.secure-boot.enable {
|
||||
assertions = [
|
||||
{
|
||||
assertion = !cfg.legacy.enable;
|
||||
message = "secure-boot and legacy boot (GRUB) cannot be enabled at the same time";
|
||||
}
|
||||
];
|
||||
config = lib.mkIf cfg.secure-boot.enable {
|
||||
assertions = [
|
||||
{
|
||||
assertion = !cfg.legacy.enable;
|
||||
message = "secure-boot and legacy boot (GRUB) cannot be enabled at the same time";
|
||||
}
|
||||
];
|
||||
|
||||
environment.systemPackages = [ pkgs.sbctl ];
|
||||
environment.systemPackages = [pkgs.sbctl];
|
||||
|
||||
# Lanzaboote replaces systemd-boot, so force it off
|
||||
boot.loader.systemd-boot.enable = lib.mkForce false;
|
||||
# Lanzaboote replaces systemd-boot, so force it off
|
||||
boot.loader.systemd-boot.enable = lib.mkForce false;
|
||||
|
||||
boot.lanzaboote = {
|
||||
enable = true;
|
||||
autoGenerateKeys.enable = true;
|
||||
autoEnrollKeys.enable = true;
|
||||
boot.lanzaboote = {
|
||||
enable = true;
|
||||
autoGenerateKeys.enable = true;
|
||||
autoEnrollKeys.enable = true;
|
||||
|
||||
configurationLimit = 10;
|
||||
pkiBundle = "/var/lib/sbctl";
|
||||
};
|
||||
configurationLimit = 10;
|
||||
pkiBundle = "/var/lib/sbctl";
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
5
modules/nixos/core/env.nix
Normal file
5
modules/nixos/core/env.nix
Normal file
@@ -0,0 +1,5 @@
|
||||
{
|
||||
flake.modules.nixos.core = {...}: {
|
||||
environment.enableAllTerminfo = true;
|
||||
};
|
||||
}
|
||||
@@ -1,37 +1,38 @@
|
||||
{ inputs, config, ... }:
|
||||
{
|
||||
flake.modules.nixos.core =
|
||||
{
|
||||
hostName,
|
||||
userName,
|
||||
userEmail,
|
||||
...
|
||||
}:
|
||||
{
|
||||
imports = [
|
||||
inputs.home-manager.nixosModules.home-manager
|
||||
];
|
||||
inputs,
|
||||
config,
|
||||
...
|
||||
}: {
|
||||
flake.modules.nixos.core = {
|
||||
hostName,
|
||||
userName,
|
||||
userEmail,
|
||||
...
|
||||
}: {
|
||||
imports = [
|
||||
inputs.home-manager.nixosModules.home-manager
|
||||
];
|
||||
|
||||
home-manager = {
|
||||
backupFileExtension = "bak";
|
||||
useGlobalPkgs = true;
|
||||
useUserPackages = true;
|
||||
extraSpecialArgs = {
|
||||
inherit
|
||||
inputs
|
||||
hostName
|
||||
userName
|
||||
userEmail
|
||||
;
|
||||
};
|
||||
home-manager = {
|
||||
backupFileExtension = "bak";
|
||||
useGlobalPkgs = true;
|
||||
useUserPackages = true;
|
||||
extraSpecialArgs = {
|
||||
inherit
|
||||
inputs
|
||||
hostName
|
||||
userName
|
||||
userEmail
|
||||
;
|
||||
};
|
||||
|
||||
users.${userName} = {
|
||||
imports = [
|
||||
config.flake.modules.homeManager.core
|
||||
config.flake.modules.homeManager.shell
|
||||
config.flake.modules.homeManager.${hostName}
|
||||
];
|
||||
};
|
||||
users.${userName} = {
|
||||
imports = [
|
||||
config.flake.modules.homeManager.core
|
||||
config.flake.modules.homeManager.shell
|
||||
config.flake.modules.homeManager.${hostName}
|
||||
];
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,20 +1,18 @@
|
||||
{
|
||||
flake.modules.nixos.core =
|
||||
{
|
||||
config,
|
||||
userName,
|
||||
...
|
||||
}:
|
||||
{
|
||||
programs.nh = {
|
||||
enable = true;
|
||||
flake.modules.nixos.core = {
|
||||
config,
|
||||
userName,
|
||||
...
|
||||
}: {
|
||||
programs.nh = {
|
||||
enable = true;
|
||||
|
||||
clean = {
|
||||
enable = !config.nix.gc.automatic;
|
||||
dates = "weekly";
|
||||
};
|
||||
|
||||
flake = "/home/${userName}/Projects/nixos-config";
|
||||
clean = {
|
||||
enable = !config.nix.gc.automatic;
|
||||
dates = "weekly";
|
||||
};
|
||||
|
||||
flake = "/home/${userName}/Projects/nixos-config";
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,6 +1,5 @@
|
||||
{ inputs, ... }:
|
||||
{
|
||||
flake.modules.nixos.core = { pkgs, ... }: {
|
||||
{inputs, ...}: {
|
||||
flake.modules.nixos.core = {pkgs, ...}: {
|
||||
imports = [
|
||||
inputs.nix-index-database.nixosModules.default
|
||||
];
|
||||
|
||||
18
modules/nixos/core/nix-ld.nix
Normal file
18
modules/nixos/core/nix-ld.nix
Normal file
@@ -0,0 +1,18 @@
|
||||
{...}: {
|
||||
flake.modules.nixos.core = {
|
||||
config,
|
||||
lib,
|
||||
...
|
||||
}:
|
||||
with lib; let
|
||||
cfg = config.tnix.programs.nix-ld;
|
||||
in {
|
||||
options.tnix.programs.nix-ld = {
|
||||
enable = mkEnableOption "nix-ld";
|
||||
};
|
||||
|
||||
config = mkIf cfg.enable {
|
||||
programs.nix-ld.enable = true;
|
||||
};
|
||||
};
|
||||
}
|
||||
@@ -1,88 +1,86 @@
|
||||
{
|
||||
flake.modules.nixos.core =
|
||||
{ userName, ... }:
|
||||
{
|
||||
nix = {
|
||||
channel.enable = false;
|
||||
flake.modules.nixos.core = {userName, ...}: {
|
||||
nix = {
|
||||
channel.enable = false;
|
||||
|
||||
gc = {
|
||||
automatic = true;
|
||||
options = "--delete-older-than 7d";
|
||||
dates = "weekly";
|
||||
persistent = true;
|
||||
};
|
||||
gc = {
|
||||
automatic = true;
|
||||
options = "--delete-older-than 7d";
|
||||
dates = "weekly";
|
||||
persistent = true;
|
||||
};
|
||||
|
||||
optimise.automatic = true;
|
||||
optimise.automatic = true;
|
||||
|
||||
settings = {
|
||||
extra-platforms = [
|
||||
"aarch64-linux"
|
||||
"arm-linux"
|
||||
];
|
||||
settings = {
|
||||
extra-platforms = [
|
||||
"aarch64-linux"
|
||||
"arm-linux"
|
||||
];
|
||||
|
||||
experimental-features = [
|
||||
"nix-command"
|
||||
"flakes"
|
||||
];
|
||||
experimental-features = [
|
||||
"nix-command"
|
||||
"flakes"
|
||||
];
|
||||
|
||||
max-jobs = "auto";
|
||||
max-jobs = "auto";
|
||||
|
||||
# Make legacy nix commands use the XDG base directories instead of creating directories in $HOME.
|
||||
use-xdg-base-directories = true;
|
||||
# Make legacy nix commands use the XDG base directories instead of creating directories in $HOME.
|
||||
use-xdg-base-directories = true;
|
||||
|
||||
# The maximum number of parallel TCP connections used to fetch files from binary caches and by other downloads.
|
||||
# It defaults to 25. 0 means no limit.
|
||||
http-connections = 128;
|
||||
# The maximum number of parallel TCP connections used to fetch files from binary caches and by other downloads.
|
||||
# It defaults to 25. 0 means no limit.
|
||||
http-connections = 128;
|
||||
|
||||
# This option defines the maximum number of substitution jobs that Nix will try to run in
|
||||
# parallel. The default is 16. The minimum value one can choose is 1 and lower values will be
|
||||
# interpreted as 1.
|
||||
max-substitution-jobs = 128;
|
||||
# This option defines the maximum number of substitution jobs that Nix will try to run in
|
||||
# parallel. The default is 16. The minimum value one can choose is 1 and lower values will be
|
||||
# interpreted as 1.
|
||||
max-substitution-jobs = 128;
|
||||
|
||||
# The number of lines of the tail of the log to show if a build fails.
|
||||
log-lines = 25;
|
||||
# The number of lines of the tail of the log to show if a build fails.
|
||||
log-lines = 25;
|
||||
|
||||
# When free disk space in /nix/store drops below min-free during a build, Nix performs a
|
||||
# garbage-collection until max-free bytes are available or there is no more garbage.
|
||||
# A value of 0 (the default) disables this feature.
|
||||
min-free = 128000000; # 128 MB
|
||||
max-free = 1000000000; # 1 GB
|
||||
# When free disk space in /nix/store drops below min-free during a build, Nix performs a
|
||||
# garbage-collection until max-free bytes are available or there is no more garbage.
|
||||
# A value of 0 (the default) disables this feature.
|
||||
min-free = 128000000; # 128 MB
|
||||
max-free = 1000000000; # 1 GB
|
||||
|
||||
# Prevent garbage collection from altering nix-shells managed by nix-direnv
|
||||
# https://github.com/nix-community/nix-direnv#installation
|
||||
keep-outputs = true;
|
||||
keep-derivations = true;
|
||||
# Prevent garbage collection from altering nix-shells managed by nix-direnv
|
||||
# https://github.com/nix-community/nix-direnv#installation
|
||||
keep-outputs = true;
|
||||
keep-derivations = true;
|
||||
|
||||
# If set to true, Nix will keep building derivations even if some fail. The default is false.
|
||||
keep-going = true;
|
||||
# If set to true, Nix will keep building derivations even if some fail. The default is false.
|
||||
keep-going = true;
|
||||
|
||||
# Automatically detect files in the store that have identical contents, and replaces
|
||||
# them with hard links to a single copy. This saves disk space.
|
||||
auto-optimise-store = true;
|
||||
# Automatically detect files in the store that have identical contents, and replaces
|
||||
# them with hard links to a single copy. This saves disk space.
|
||||
auto-optimise-store = true;
|
||||
|
||||
# Whether to warn about dirty Git/Mercurial trees.
|
||||
warn-dirty = false;
|
||||
# Whether to warn about dirty Git/Mercurial trees.
|
||||
warn-dirty = false;
|
||||
|
||||
# The timeout (in seconds) for establishing connections in the binary cache substituter.
|
||||
# It corresponds to curl’s –connect-timeout option. A value of 0 means no limit.
|
||||
connect-timeout = 5;
|
||||
# The timeout (in seconds) for establishing connections in the binary cache substituter.
|
||||
# It corresponds to curl’s –connect-timeout option. A value of 0 means no limit.
|
||||
connect-timeout = 5;
|
||||
|
||||
# Allow the use of cachix
|
||||
trusted-users = [
|
||||
"root"
|
||||
"${userName}"
|
||||
];
|
||||
allowed-users = [
|
||||
"root"
|
||||
"${userName}"
|
||||
];
|
||||
# Allow the use of cachix
|
||||
trusted-users = [
|
||||
"root"
|
||||
"${userName}"
|
||||
];
|
||||
allowed-users = [
|
||||
"root"
|
||||
"${userName}"
|
||||
];
|
||||
|
||||
builders-use-substitutes = true;
|
||||
builders-use-substitutes = true;
|
||||
|
||||
# If set to true, Nix will fall back to building from source if a binary substitute
|
||||
# fails. This is equivalent to the –fallback flag. The default is false.
|
||||
fallback = true;
|
||||
};
|
||||
# If set to true, Nix will fall back to building from source if a binary substitute
|
||||
# fails. This is equivalent to the –fallback flag. The default is false.
|
||||
fallback = true;
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,5 +1,4 @@
|
||||
{ inputs, ... }:
|
||||
{
|
||||
{inputs, ...}: {
|
||||
flake.modules.nixos.core = {
|
||||
nixpkgs = {
|
||||
config = {
|
||||
|
||||
@@ -1,25 +1,21 @@
|
||||
{ inputs, ... }:
|
||||
{
|
||||
flake.modules.nixos.core =
|
||||
{
|
||||
config,
|
||||
pkgs,
|
||||
...
|
||||
}:
|
||||
let
|
||||
isEd25519 = k: k.type == "ed25519";
|
||||
getKeyPath = k: k.path;
|
||||
keys = builtins.filter isEd25519 config.services.openssh.hostKeys;
|
||||
in
|
||||
{
|
||||
imports = [ inputs.sops-nix.nixosModules.sops ];
|
||||
{inputs, ...}: {
|
||||
flake.modules.nixos.core = {
|
||||
config,
|
||||
pkgs,
|
||||
...
|
||||
}: let
|
||||
isEd25519 = k: k.type == "ed25519";
|
||||
getKeyPath = k: k.path;
|
||||
keys = builtins.filter isEd25519 config.services.openssh.hostKeys;
|
||||
in {
|
||||
imports = [inputs.sops-nix.nixosModules.sops];
|
||||
|
||||
sops.age = {
|
||||
sshKeyPaths = map getKeyPath keys;
|
||||
keyFile = "/var/lib/sops-nix/key.txt";
|
||||
generateKey = true;
|
||||
};
|
||||
|
||||
environment.systemPackages = with pkgs; [ sops ];
|
||||
sops.age = {
|
||||
sshKeyPaths = map getKeyPath keys;
|
||||
keyFile = "/var/lib/sops-nix/key.txt";
|
||||
generateKey = true;
|
||||
};
|
||||
|
||||
environment.systemPackages = with pkgs; [sops];
|
||||
};
|
||||
}
|
||||
|
||||
@@ -33,6 +33,10 @@
|
||||
"wezterm.cachix.org-1:kAbhjYUC9qvblTE+s7S+kl5XM1zVa4skO+E/1IDWdH0="
|
||||
"cache.nixos-cuda.org:74DUi4Ye579gUqzH4ziL9IyiJBlDpMRn9MBN8oNan9M="
|
||||
];
|
||||
extra-substituters = ["https://cache.numtide.com"];
|
||||
extra-trusted-public-keys = [
|
||||
"niks3.numtide.com-1:DTx8wZduET09hRmMtKdQDxNNthLQETkc/yaX7M4qK0g="
|
||||
];
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,51 +1,48 @@
|
||||
{
|
||||
flake.modules.nixos.core =
|
||||
{
|
||||
pkgs,
|
||||
lib,
|
||||
config,
|
||||
userName,
|
||||
userEmail,
|
||||
...
|
||||
}:
|
||||
let
|
||||
hasPasswordSecret = lib.hasAttrByPath [ "sops" "secrets" "tux-password" ] config;
|
||||
in
|
||||
{
|
||||
programs.zsh.enable = true;
|
||||
flake.modules.nixos.core = {
|
||||
pkgs,
|
||||
lib,
|
||||
config,
|
||||
userName,
|
||||
userEmail,
|
||||
...
|
||||
}: let
|
||||
hasPasswordSecret = lib.hasAttrByPath ["sops" "secrets" "tux-password"] config;
|
||||
in {
|
||||
programs.zsh.enable = true;
|
||||
|
||||
time.timeZone = "Asia/Kolkata";
|
||||
i18n = {
|
||||
defaultLocale = "en_US.UTF-8";
|
||||
extraLocaleSettings = lib.genAttrs [
|
||||
"LC_ADDRESS"
|
||||
"LC_IDENTIFICATION"
|
||||
"LC_MEASUREMENT"
|
||||
"LC_MONETARY"
|
||||
"LC_NAME"
|
||||
"LC_NUMERIC"
|
||||
"LC_PAPER"
|
||||
"LC_TELEPHONE"
|
||||
"LC_TIME"
|
||||
] (_: "en_IN");
|
||||
};
|
||||
time.timeZone = "Asia/Kolkata";
|
||||
i18n = {
|
||||
defaultLocale = "en_US.UTF-8";
|
||||
extraLocaleSettings = lib.genAttrs [
|
||||
"LC_ADDRESS"
|
||||
"LC_IDENTIFICATION"
|
||||
"LC_MEASUREMENT"
|
||||
"LC_MONETARY"
|
||||
"LC_NAME"
|
||||
"LC_NUMERIC"
|
||||
"LC_PAPER"
|
||||
"LC_TELEPHONE"
|
||||
"LC_TIME"
|
||||
] (_: "en_IN");
|
||||
};
|
||||
|
||||
users = {
|
||||
mutableUsers = false;
|
||||
defaultUserShell = pkgs.zsh;
|
||||
users.${userName} = {
|
||||
hashedPasswordFile = lib.mkIf hasPasswordSecret config.sops.secrets.tux-password.path;
|
||||
initialPassword = lib.mkIf (!hasPasswordSecret) userName;
|
||||
isNormalUser = true;
|
||||
extraGroups = [
|
||||
"networkmanager"
|
||||
"wheel"
|
||||
"storage"
|
||||
];
|
||||
openssh.authorizedKeys.keys = [
|
||||
"ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIL+OzPUe2ECPC929DqpkM39tl/vdNAXfsRnmrGfR+X3D ${userEmail}"
|
||||
];
|
||||
};
|
||||
users = {
|
||||
mutableUsers = false;
|
||||
defaultUserShell = pkgs.zsh;
|
||||
users.${userName} = {
|
||||
hashedPasswordFile = lib.mkIf hasPasswordSecret config.sops.secrets.tux-password.path;
|
||||
initialPassword = lib.mkIf (!hasPasswordSecret) userName;
|
||||
isNormalUser = true;
|
||||
extraGroups = [
|
||||
"networkmanager"
|
||||
"wheel"
|
||||
"storage"
|
||||
];
|
||||
openssh.authorizedKeys.keys = [
|
||||
"ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIL+OzPUe2ECPC929DqpkM39tl/vdNAXfsRnmrGfR+X3D ${userEmail}"
|
||||
];
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,11 +1,9 @@
|
||||
{
|
||||
flake.modules.nixos.desktop =
|
||||
{ pkgs, ... }:
|
||||
{
|
||||
fonts.packages = with pkgs.nerd-fonts; [
|
||||
fira-code
|
||||
jetbrains-mono
|
||||
bigblue-terminal
|
||||
];
|
||||
};
|
||||
flake.modules.nixos.desktop = {pkgs, ...}: {
|
||||
fonts.packages = with pkgs.nerd-fonts; [
|
||||
fira-code
|
||||
jetbrains-mono
|
||||
bigblue-terminal
|
||||
];
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,13 +1,11 @@
|
||||
{
|
||||
flake.modules.nixos.desktop =
|
||||
{ pkgs, ... }:
|
||||
{
|
||||
programs.gpu-screen-recorder = {
|
||||
enable = true;
|
||||
};
|
||||
|
||||
environment.systemPackages = with pkgs; [
|
||||
gpu-screen-recorder-gtk
|
||||
];
|
||||
flake.modules.nixos.desktop = {pkgs, ...}: {
|
||||
programs.gpu-screen-recorder = {
|
||||
enable = true;
|
||||
};
|
||||
|
||||
environment.systemPackages = with pkgs; [
|
||||
gpu-screen-recorder-gtk
|
||||
];
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,11 +1,9 @@
|
||||
{
|
||||
flake.modules.nixos.desktop =
|
||||
{ pkgs, ... }:
|
||||
{
|
||||
programs.hyprland = {
|
||||
enable = true;
|
||||
package = pkgs.hyprland-git.hyprland;
|
||||
portalPackage = pkgs.hyprland-git.xdg-desktop-portal-hyprland;
|
||||
};
|
||||
flake.modules.nixos.desktop = {pkgs, ...}: {
|
||||
programs.hyprland = {
|
||||
enable = true;
|
||||
package = pkgs.hyprland-git.hyprland;
|
||||
portalPackage = pkgs.hyprland-git.xdg-desktop-portal-hyprland;
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,36 +1,30 @@
|
||||
{
|
||||
inputs,
|
||||
...
|
||||
}:
|
||||
{
|
||||
flake.modules.nixos.desktop =
|
||||
{
|
||||
pkgs,
|
||||
lib,
|
||||
...
|
||||
}:
|
||||
{
|
||||
imports = [
|
||||
inputs.mango.nixosModules.mango
|
||||
{inputs, ...}: {
|
||||
flake.modules.nixos.desktop = {
|
||||
pkgs,
|
||||
lib,
|
||||
...
|
||||
}: {
|
||||
imports = [
|
||||
inputs.mango.nixosModules.mango
|
||||
];
|
||||
|
||||
programs.mango.enable = true;
|
||||
|
||||
xdg.portal = {
|
||||
enable = lib.mkDefault true;
|
||||
extraPortals = with pkgs; [
|
||||
hyprland-git.xdg-desktop-portal-hyprland
|
||||
xdg-desktop-portal-wlr
|
||||
xdg-desktop-portal-gtk
|
||||
];
|
||||
|
||||
programs.mango.enable = true;
|
||||
|
||||
xdg.portal = {
|
||||
enable = lib.mkDefault true;
|
||||
extraPortals = with pkgs; [
|
||||
hyprland-git.xdg-desktop-portal-hyprland
|
||||
xdg-desktop-portal-wlr
|
||||
xdg-desktop-portal-gtk
|
||||
config.mango = {
|
||||
default = lib.mkForce [
|
||||
"hyprland"
|
||||
"gtk"
|
||||
];
|
||||
config.mango = {
|
||||
default = lib.mkForce [
|
||||
"hyprland"
|
||||
"gtk"
|
||||
];
|
||||
"org.freedesktop.impl.portal.ScreenCast" = lib.mkForce [ "hyprland" ];
|
||||
"org.freedesktop.impl.portal.ScreenShot" = lib.mkForce [ "hyprland" ];
|
||||
};
|
||||
"org.freedesktop.impl.portal.ScreenCast" = lib.mkForce ["hyprland"];
|
||||
"org.freedesktop.impl.portal.ScreenShot" = lib.mkForce ["hyprland"];
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,7 +1,5 @@
|
||||
{
|
||||
flake.modules.nixos.desktop =
|
||||
{ pkgs, ... }:
|
||||
{
|
||||
environment.systemPackages = with pkgs; [ brightnessctl ];
|
||||
};
|
||||
flake.modules.nixos.desktop = {pkgs, ...}: {
|
||||
environment.systemPackages = with pkgs; [brightnessctl];
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,15 +1,14 @@
|
||||
{
|
||||
flake.modules.nixos.desktop =
|
||||
{ pkgs, ... }:
|
||||
{
|
||||
programs.obs-studio = {
|
||||
enable = true;
|
||||
enableVirtualCamera = true;
|
||||
plugins = with pkgs.obs-studio-plugins; [
|
||||
obs-vaapi
|
||||
wlrobs
|
||||
obs-source-record
|
||||
];
|
||||
};
|
||||
flake.modules.nixos.desktop = {pkgs, ...}: {
|
||||
programs.obs-studio = {
|
||||
enable = true;
|
||||
enableVirtualCamera = true;
|
||||
plugins = with pkgs.obs-studio-plugins; [
|
||||
obs-vaapi
|
||||
wlrobs
|
||||
obs-source-record
|
||||
obs-advanced-masks
|
||||
];
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,18 +1,16 @@
|
||||
{
|
||||
flake.modules.nixos.desktop =
|
||||
{ pkgs, ... }:
|
||||
{
|
||||
services = {
|
||||
gvfs.enable = true;
|
||||
tumbler.enable = true;
|
||||
};
|
||||
|
||||
programs.thunar = {
|
||||
enable = true;
|
||||
plugins = with pkgs; [
|
||||
thunar-archive-plugin
|
||||
thunar-volman
|
||||
];
|
||||
};
|
||||
flake.modules.nixos.desktop = {pkgs, ...}: {
|
||||
services = {
|
||||
gvfs.enable = true;
|
||||
tumbler.enable = true;
|
||||
};
|
||||
|
||||
programs.thunar = {
|
||||
enable = true;
|
||||
plugins = with pkgs; [
|
||||
thunar-archive-plugin
|
||||
thunar-volman
|
||||
];
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,7 +0,0 @@
|
||||
{
|
||||
flake.modules.nixos.desktop =
|
||||
{ pkgs, ... }:
|
||||
{
|
||||
environment.systemPackages = with pkgs; [ tpanel ];
|
||||
};
|
||||
}
|
||||
5
modules/nixos/desktop/tshell.nix
Normal file
5
modules/nixos/desktop/tshell.nix
Normal file
@@ -0,0 +1,5 @@
|
||||
{
|
||||
flake.modules.nixos.desktop = {pkgs, ...}: {
|
||||
environment.systemPackages = with pkgs; [tshell];
|
||||
};
|
||||
}
|
||||
@@ -1,11 +1,9 @@
|
||||
{
|
||||
flake.modules.nixos.gaming =
|
||||
{ pkgs, ... }:
|
||||
{
|
||||
programs.steam = {
|
||||
enable = true;
|
||||
protontricks.enable = true;
|
||||
extraCompatPackages = with pkgs; [ proton-ge-bin ];
|
||||
};
|
||||
flake.modules.nixos.gaming = {pkgs, ...}: {
|
||||
programs.steam = {
|
||||
enable = true;
|
||||
protontricks.enable = true;
|
||||
extraCompatPackages = with pkgs; [proton-ge-bin];
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,5 +1,5 @@
|
||||
{
|
||||
flake.modules.nixos.hardware = {
|
||||
flake.modules.nixos.hardware = {pkgs, ...}: {
|
||||
security.rtkit.enable = true;
|
||||
|
||||
services.pipewire = {
|
||||
@@ -9,5 +9,10 @@
|
||||
pulse.enable = true;
|
||||
wireplumber.enable = true;
|
||||
};
|
||||
|
||||
environment.systemPackages = with pkgs; [
|
||||
alsa-utils
|
||||
pavucontrol
|
||||
];
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,5 +1,5 @@
|
||||
{
|
||||
flake.modules.nixos.hardware = { pkgs, ... }: {
|
||||
flake.modules.nixos.hardware = {pkgs, ...}: {
|
||||
hardware.bluetooth = {
|
||||
enable = true;
|
||||
};
|
||||
|
||||
@@ -1,16 +1,13 @@
|
||||
{
|
||||
flake.modules.nixos.networking =
|
||||
{
|
||||
config,
|
||||
lib,
|
||||
hostName,
|
||||
...
|
||||
}:
|
||||
with lib;
|
||||
let
|
||||
flake.modules.nixos.networking = {
|
||||
config,
|
||||
lib,
|
||||
hostName,
|
||||
...
|
||||
}:
|
||||
with lib; let
|
||||
cfg = config.tnix.networking.netbird-client;
|
||||
in
|
||||
{
|
||||
in {
|
||||
options.tnix.networking.netbird-client = {
|
||||
enable = mkEnableOption "Enable netbird client";
|
||||
};
|
||||
|
||||
@@ -1,15 +1,12 @@
|
||||
{
|
||||
flake.modules.nixos.networking =
|
||||
{
|
||||
config,
|
||||
lib,
|
||||
...
|
||||
}:
|
||||
with lib;
|
||||
let
|
||||
flake.modules.nixos.networking = {
|
||||
config,
|
||||
lib,
|
||||
...
|
||||
}:
|
||||
with lib; let
|
||||
cfg = config.tnix.networking.newt;
|
||||
in
|
||||
{
|
||||
in {
|
||||
options.tnix.networking.newt = {
|
||||
enable = mkEnableOption "Newt";
|
||||
|
||||
|
||||
@@ -1,25 +1,22 @@
|
||||
{
|
||||
flake.modules.nixos.networking =
|
||||
{
|
||||
config,
|
||||
lib,
|
||||
...
|
||||
}:
|
||||
with lib;
|
||||
let
|
||||
flake.modules.nixos.networking = {
|
||||
config,
|
||||
lib,
|
||||
...
|
||||
}:
|
||||
with lib; let
|
||||
cfg = config.tnix.networking.openssh;
|
||||
|
||||
# Sops needs acess to the keys before the persist dirs are even mounted; so
|
||||
# just persisting the keys won't work, we must point at /persist
|
||||
hasOptinPersistence = config.tnix.boot.impermanence.enable;
|
||||
in
|
||||
{
|
||||
in {
|
||||
options.tnix.networking.openssh = {
|
||||
enable = mkEnableOption "Enable OpenSSH server";
|
||||
|
||||
ports = mkOption {
|
||||
type = types.listOf types.port;
|
||||
default = [ 22 ];
|
||||
default = [22];
|
||||
description = ''
|
||||
Specifies on which ports the SSH daemon listens.
|
||||
'';
|
||||
|
||||
@@ -1,17 +1,14 @@
|
||||
{
|
||||
flake.modules.nixos.services =
|
||||
{
|
||||
config,
|
||||
lib,
|
||||
...
|
||||
}:
|
||||
with lib;
|
||||
let
|
||||
flake.modules.nixos.services = {
|
||||
config,
|
||||
lib,
|
||||
...
|
||||
}:
|
||||
with lib; let
|
||||
cfg = config.tnix.services.aiostreams;
|
||||
port = toString cfg.port;
|
||||
acmeHost = config.tnix.services.nginx.domain;
|
||||
in
|
||||
{
|
||||
in {
|
||||
options.tnix.services.aiostreams = {
|
||||
enable = mkEnableOption "AIOStreams";
|
||||
|
||||
|
||||
95
modules/nixos/services/coder.nix
Normal file
95
modules/nixos/services/coder.nix
Normal file
@@ -0,0 +1,95 @@
|
||||
{
|
||||
flake.modules.nixos.services = {
|
||||
config,
|
||||
lib,
|
||||
options,
|
||||
...
|
||||
}:
|
||||
with lib; let
|
||||
cfg = config.tnix.services.coder;
|
||||
port = toString cfg.port;
|
||||
in {
|
||||
options.tnix.services.coder = {
|
||||
enable = mkEnableOption "Coder";
|
||||
|
||||
host = mkOption {
|
||||
type = types.str;
|
||||
default = "127.0.0.1";
|
||||
description = "Host on which Coder listens";
|
||||
};
|
||||
|
||||
port = mkOption {
|
||||
type = types.port;
|
||||
default = 1116;
|
||||
description = "Port on which Coder listens";
|
||||
};
|
||||
|
||||
environment = options.services.coder.environment;
|
||||
|
||||
domain = mkOption {
|
||||
type = types.str;
|
||||
default = "";
|
||||
description = "Domain on which Coder is available";
|
||||
};
|
||||
|
||||
configureNginx = mkOption {
|
||||
type = types.bool;
|
||||
default = false;
|
||||
description = "Whether to configure Nginx as a reverse proxy for Coder";
|
||||
};
|
||||
|
||||
configurePangolin = mkOption {
|
||||
type = types.bool;
|
||||
default = false;
|
||||
description = "Whether to configure Pangolin as a reverse proxy for Coder";
|
||||
};
|
||||
};
|
||||
|
||||
config = mkIf cfg.enable {
|
||||
users.users.coder.extraGroups = ["docker"];
|
||||
|
||||
services = {
|
||||
coder = {
|
||||
enable = true;
|
||||
accessUrl = "https://${cfg.domain}";
|
||||
listenAddress = "${cfg.host}:${port}";
|
||||
environment = cfg.environment;
|
||||
};
|
||||
|
||||
nginx.virtualHosts.${cfg.domain} = mkIf cfg.configureNginx {
|
||||
forceSSL = acmeHost != "";
|
||||
useACMEHost = mkIf (acmeHost != "") acmeHost;
|
||||
locations."/" = {
|
||||
proxyPass = "http://${cfg.host}:${port}";
|
||||
proxyWebsockets = true;
|
||||
};
|
||||
};
|
||||
|
||||
newt.blueprint.proxy-resources = mkIf cfg.configurePangolin {
|
||||
gitea = {
|
||||
auth = {
|
||||
sso-enabled = false;
|
||||
};
|
||||
full-domain = cfg.domain;
|
||||
name = "coder";
|
||||
protocol = "http";
|
||||
targets = [
|
||||
{
|
||||
hostname = "localhost";
|
||||
method = "http";
|
||||
port = cfg.port;
|
||||
healthcheck = {
|
||||
hostname = "localhost";
|
||||
port = cfg.port;
|
||||
scheme = "http";
|
||||
method = "GET";
|
||||
path = "/";
|
||||
};
|
||||
}
|
||||
];
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
@@ -1,19 +1,16 @@
|
||||
{ inputs, ... }: {
|
||||
flake.modules.nixos.services =
|
||||
{
|
||||
config,
|
||||
lib,
|
||||
pkgs,
|
||||
options,
|
||||
...
|
||||
}:
|
||||
with lib;
|
||||
let
|
||||
{inputs, ...}: {
|
||||
flake.modules.nixos.services = {
|
||||
config,
|
||||
lib,
|
||||
pkgs,
|
||||
options,
|
||||
...
|
||||
}:
|
||||
with lib; let
|
||||
cfg = config.tnix.services.copyparty;
|
||||
port = toString cfg.port;
|
||||
acmeHost = config.tnix.services.nginx.domain;
|
||||
in
|
||||
{
|
||||
in {
|
||||
imports = [
|
||||
inputs.copyparty.nixosModules.default
|
||||
];
|
||||
@@ -75,7 +72,7 @@
|
||||
accounts = cfg.accounts;
|
||||
volumes = cfg.volumes;
|
||||
package = pkgs.copyparty.override {
|
||||
extraPackages = [ pkgs.exiftool ];
|
||||
extraPackages = [pkgs.exiftool];
|
||||
};
|
||||
};
|
||||
|
||||
|
||||
@@ -1,16 +1,13 @@
|
||||
{
|
||||
flake.modules.nixos.services =
|
||||
{
|
||||
config,
|
||||
lib,
|
||||
pkgs,
|
||||
...
|
||||
}:
|
||||
with lib;
|
||||
let
|
||||
flake.modules.nixos.services = {
|
||||
config,
|
||||
lib,
|
||||
pkgs,
|
||||
...
|
||||
}:
|
||||
with lib; let
|
||||
cfg = config.tnix.services.cyber-tux;
|
||||
in
|
||||
{
|
||||
in {
|
||||
options.tnix.services.cyber-tux = {
|
||||
enable = mkEnableOption "CyberTux Discord bot";
|
||||
|
||||
@@ -41,9 +38,9 @@
|
||||
config = mkIf cfg.enable {
|
||||
systemd.services.cyber-tux = {
|
||||
description = "CyberTux Discord bot";
|
||||
after = [ "network-online.target" ];
|
||||
wants = [ "network-online.target" ];
|
||||
wantedBy = [ "multi-user.target" ];
|
||||
after = ["network-online.target"];
|
||||
wants = ["network-online.target"];
|
||||
wantedBy = ["multi-user.target"];
|
||||
|
||||
serviceConfig = {
|
||||
Type = "simple";
|
||||
@@ -83,7 +80,7 @@
|
||||
RestrictRealtime = true;
|
||||
RestrictSUIDSGID = true;
|
||||
SystemCallArchitectures = "native";
|
||||
SystemCallFilter = [ "@system-service" ];
|
||||
SystemCallFilter = ["@system-service"];
|
||||
UMask = "0077";
|
||||
};
|
||||
};
|
||||
@@ -99,7 +96,7 @@
|
||||
};
|
||||
|
||||
users.groups = mkIf (cfg.group == "cyber-tux") {
|
||||
${cfg.group} = { };
|
||||
${cfg.group} = {};
|
||||
};
|
||||
};
|
||||
};
|
||||
|
||||
@@ -1,17 +1,14 @@
|
||||
{
|
||||
flake.modules.nixos.services =
|
||||
{
|
||||
config,
|
||||
lib,
|
||||
...
|
||||
}:
|
||||
with lib;
|
||||
let
|
||||
flake.modules.nixos.services = {
|
||||
config,
|
||||
lib,
|
||||
...
|
||||
}:
|
||||
with lib; let
|
||||
cfg = config.tnix.services.gitea;
|
||||
port = toString cfg.port;
|
||||
acmeHost = config.tnix.services.nginx.domain;
|
||||
in
|
||||
{
|
||||
in {
|
||||
options.tnix.services.gitea = {
|
||||
enable = mkEnableOption "Gitea";
|
||||
|
||||
@@ -109,7 +106,7 @@
|
||||
|
||||
postgresql = {
|
||||
enable = true;
|
||||
ensureDatabases = [ "gitea" ];
|
||||
ensureDatabases = ["gitea"];
|
||||
ensureUsers = [
|
||||
{
|
||||
name = "gitea";
|
||||
|
||||
@@ -1,17 +1,15 @@
|
||||
{ inputs, ... }: {
|
||||
flake.modules.nixos.services =
|
||||
{
|
||||
config,
|
||||
lib,
|
||||
options,
|
||||
userName,
|
||||
...
|
||||
}:
|
||||
with lib;
|
||||
let
|
||||
{inputs, ...}: {
|
||||
flake.modules.nixos.services = {
|
||||
config,
|
||||
lib,
|
||||
pkgs,
|
||||
options,
|
||||
userName,
|
||||
...
|
||||
}:
|
||||
with lib; let
|
||||
cfg = config.tnix.services.hermes-agent;
|
||||
in
|
||||
{
|
||||
in {
|
||||
imports = [
|
||||
inputs.hermes-agent.nixosModules.default
|
||||
];
|
||||
@@ -26,13 +24,22 @@
|
||||
enable = true;
|
||||
settings.model = {
|
||||
provider = "opencode-go";
|
||||
default = "deepseek-v4-flash";
|
||||
default = "deepseek-v4.1-flash";
|
||||
};
|
||||
environmentFiles = cfg.environmentFiles;
|
||||
addToSystemPackages = true;
|
||||
|
||||
extraPlugins = [
|
||||
(pkgs.fetchFromGitHub {
|
||||
owner = "DietrichGebert";
|
||||
repo = "ponytail";
|
||||
rev = "v4.9.0";
|
||||
hash = "sha256-8cYggVltBAlZ/Zj4pl1bOu7mQdZFXCmDGW4RSpvRA+w=";
|
||||
})
|
||||
];
|
||||
};
|
||||
|
||||
users.users.${userName}.extraGroups = [ "hermes" ];
|
||||
users.users.${userName}.extraGroups = ["hermes"];
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,17 +1,14 @@
|
||||
{
|
||||
flake.modules.nixos.services =
|
||||
{
|
||||
config,
|
||||
lib,
|
||||
...
|
||||
}:
|
||||
with lib;
|
||||
let
|
||||
flake.modules.nixos.services = {
|
||||
config,
|
||||
lib,
|
||||
...
|
||||
}:
|
||||
with lib; let
|
||||
cfg = config.tnix.services.mediaflow-proxy;
|
||||
port = toString cfg.port;
|
||||
acmeHost = config.tnix.services.nginx.domain;
|
||||
in
|
||||
{
|
||||
in {
|
||||
options.tnix.services.mediaflow-proxy = {
|
||||
enable = mkEnableOption "MediaFlow Proxy";
|
||||
|
||||
|
||||
@@ -1,16 +1,13 @@
|
||||
{
|
||||
flake.modules.nixos.services =
|
||||
{
|
||||
config,
|
||||
lib,
|
||||
userEmail,
|
||||
...
|
||||
}:
|
||||
with lib;
|
||||
let
|
||||
flake.modules.nixos.services = {
|
||||
config,
|
||||
lib,
|
||||
userEmail,
|
||||
...
|
||||
}:
|
||||
with lib; let
|
||||
cfg = config.tnix.services.nginx;
|
||||
in
|
||||
{
|
||||
in {
|
||||
options.tnix.services.nginx = {
|
||||
enable = mkEnableOption "Nginx";
|
||||
|
||||
@@ -30,7 +27,7 @@
|
||||
"${cfg.domain}" = {
|
||||
group = "nginx";
|
||||
domain = "*.${cfg.domain}";
|
||||
extraDomainNames = [ "${cfg.domain}" ];
|
||||
extraDomainNames = ["${cfg.domain}"];
|
||||
dnsProvider = "cloudflare";
|
||||
credentialFiles = {
|
||||
CLOUDFLARE_EMAIL_FILE = config.sops.secrets."cloudflare-credentials/email".path;
|
||||
@@ -41,7 +38,7 @@
|
||||
};
|
||||
};
|
||||
|
||||
users.users.nginx.extraGroups = [ "acme" ];
|
||||
users.users.nginx.extraGroups = ["acme"];
|
||||
|
||||
services.nginx = {
|
||||
enable = true;
|
||||
|
||||
@@ -1,17 +1,14 @@
|
||||
{
|
||||
flake.modules.nixos.services =
|
||||
{
|
||||
config,
|
||||
lib,
|
||||
userEmail,
|
||||
pkgs,
|
||||
...
|
||||
}:
|
||||
with lib;
|
||||
let
|
||||
flake.modules.nixos.services = {
|
||||
config,
|
||||
lib,
|
||||
userEmail,
|
||||
pkgs,
|
||||
...
|
||||
}:
|
||||
with lib; let
|
||||
cfg = config.tnix.services.pangolin;
|
||||
in
|
||||
{
|
||||
in {
|
||||
options.tnix.services.pangolin = {
|
||||
enable = mkEnableOption "Pangolin";
|
||||
|
||||
@@ -77,7 +74,7 @@
|
||||
|
||||
postgresql = {
|
||||
enable = true;
|
||||
ensureDatabases = [ "pangolin" ];
|
||||
ensureDatabases = ["pangolin"];
|
||||
ensureUsers = [
|
||||
{
|
||||
name = "pangolin";
|
||||
|
||||
24
modules/nixos/services/trok.nix
Normal file
24
modules/nixos/services/trok.nix
Normal file
@@ -0,0 +1,24 @@
|
||||
{inputs, ...}: {
|
||||
flake.modules.nixos.services = {
|
||||
config,
|
||||
lib,
|
||||
...
|
||||
}:
|
||||
with lib; let
|
||||
cfg = config.tnix.services.trok;
|
||||
in {
|
||||
imports = [
|
||||
inputs.trok.nixosModules.default
|
||||
];
|
||||
|
||||
options.tnix.services.trok = {
|
||||
enable = mkEnableOption "trok";
|
||||
};
|
||||
|
||||
config = mkIf cfg.enable {
|
||||
services.trok = {
|
||||
enable = true;
|
||||
};
|
||||
};
|
||||
};
|
||||
}
|
||||
@@ -1,17 +1,14 @@
|
||||
{
|
||||
flake.modules.nixos.services =
|
||||
{
|
||||
config,
|
||||
lib,
|
||||
...
|
||||
}:
|
||||
with lib;
|
||||
let
|
||||
flake.modules.nixos.services = {
|
||||
config,
|
||||
lib,
|
||||
...
|
||||
}:
|
||||
with lib; let
|
||||
cfg = config.tnix.services.uptime-kuma;
|
||||
port = toString cfg.port;
|
||||
acmeHost = config.tnix.services.nginx.domain;
|
||||
in
|
||||
{
|
||||
in {
|
||||
options.tnix.services.uptime-kuma = {
|
||||
enable = mkEnableOption "Uptime Kuma";
|
||||
|
||||
|
||||
@@ -1,17 +1,14 @@
|
||||
{
|
||||
flake.modules.nixos.services =
|
||||
{
|
||||
config,
|
||||
lib,
|
||||
...
|
||||
}:
|
||||
with lib;
|
||||
let
|
||||
flake.modules.nixos.services = {
|
||||
config,
|
||||
lib,
|
||||
...
|
||||
}:
|
||||
with lib; let
|
||||
cfg = config.tnix.services.vaultwarden;
|
||||
port = toString cfg.port;
|
||||
acmeHost = config.tnix.services.nginx.domain;
|
||||
in
|
||||
{
|
||||
in {
|
||||
options.tnix.services.vaultwarden = {
|
||||
enable = mkEnableOption "Vaultwarden";
|
||||
|
||||
@@ -106,7 +103,7 @@
|
||||
|
||||
postgresql = {
|
||||
enable = true;
|
||||
ensureDatabases = [ "vaultwarden" ];
|
||||
ensureDatabases = ["vaultwarden"];
|
||||
ensureUsers = [
|
||||
{
|
||||
name = "vaultwarden";
|
||||
|
||||
@@ -1,118 +1,113 @@
|
||||
{
|
||||
flake.modules.nixos.virtualisation =
|
||||
{
|
||||
config,
|
||||
lib,
|
||||
pkgs,
|
||||
...
|
||||
}:
|
||||
let
|
||||
cfg = config.tnix.virtualisation;
|
||||
in
|
||||
{
|
||||
options.tnix.virtualisation.distrobox = {
|
||||
enable = lib.mkEnableOption "Enable DistroBox";
|
||||
};
|
||||
|
||||
config = lib.mkIf cfg.distrobox.enable {
|
||||
virtualisation.waydroid.enable = true;
|
||||
|
||||
environment.systemPackages = with pkgs; [
|
||||
distrobox
|
||||
|
||||
(writeShellScriptBin "dbox-create" ''
|
||||
#!/usr/bin/env bash
|
||||
|
||||
# 1. Initialize variables
|
||||
IMAGE=""
|
||||
NAME=""
|
||||
|
||||
# Array to hold optional arguments (like volumes)
|
||||
declare -a EXTRA_ARGS
|
||||
|
||||
# 2. Parse arguments
|
||||
while [[ $# -gt 0 ]]; do
|
||||
case $1 in
|
||||
-i|--image)
|
||||
IMAGE="$2"
|
||||
shift 2
|
||||
;;
|
||||
-n|--name)
|
||||
NAME="$2"
|
||||
shift 2
|
||||
;;
|
||||
-p|--profile)
|
||||
echo ":: Profile mode enabled: Mounting Nix store and user profiles (Read-Only)"
|
||||
# Add volume flags to the array
|
||||
EXTRA_ARGS+=( "--volume" "/nix/store:/nix/store:ro" )
|
||||
EXTRA_ARGS+=( "--volume" "/etc/profiles/per-user:/etc/profiles/per-user:ro" )
|
||||
EXTRA_ARGS+=( "--volume" "/etc/static/profiles/per-user:/etc/static/profiles/per-user:ro" )
|
||||
shift 1
|
||||
;;
|
||||
*)
|
||||
echo "Unknown option $1"
|
||||
exit 1
|
||||
;;
|
||||
esac
|
||||
done
|
||||
|
||||
if [ -z "$IMAGE" ] || [ -z "$NAME" ]; then
|
||||
echo "Usage: dbox-create -i <image> -n <name> [-p]"
|
||||
exit 1
|
||||
fi
|
||||
|
||||
# 3. Define the custom home path
|
||||
CUSTOM_HOME="$HOME/Distrobox/$NAME"
|
||||
|
||||
echo "------------------------------------------------"
|
||||
echo "Creating Distrobox: $NAME"
|
||||
echo "Location: $CUSTOM_HOME"
|
||||
echo "------------------------------------------------"
|
||||
|
||||
# 4. Run Distrobox Create
|
||||
# We expand "''${EXTRA_ARGS[@]}" to properly pass the volume arguments
|
||||
${pkgs.distrobox}/bin/distrobox create \
|
||||
--image "$IMAGE" \
|
||||
--name "$NAME" \
|
||||
--home "$CUSTOM_HOME" \
|
||||
"''${EXTRA_ARGS[@]}"
|
||||
|
||||
# Check exit code
|
||||
if [ $? -ne 0 ]; then
|
||||
echo "Error: Distrobox creation failed."
|
||||
exit 1
|
||||
fi
|
||||
|
||||
# 5. Post-Creation: Symlink Config Files
|
||||
echo "--> Linking configurations to $NAME..."
|
||||
|
||||
# Helper function to symlink
|
||||
link_config() {
|
||||
SRC="$1"
|
||||
DEST="$2"
|
||||
DEST_DIR=$(dirname "$DEST")
|
||||
|
||||
# Create parent directory if it doesn't exist
|
||||
mkdir -p "$DEST_DIR"
|
||||
|
||||
if [ -e "$SRC" ]; then
|
||||
# ln -sf: symbolic link, force overwrite
|
||||
ln -sf "$SRC" "$DEST"
|
||||
echo " [LINK] $DEST -> $SRC"
|
||||
else
|
||||
echo " [SKIP] $SRC not found on host"
|
||||
fi
|
||||
}
|
||||
|
||||
# Create Symlinks
|
||||
link_config "$HOME/.zshrc" "$CUSTOM_HOME/.zshrc"
|
||||
link_config "$HOME/.zshenv" "$CUSTOM_HOME/.zshenv"
|
||||
link_config "$HOME/.config/fastfetch" "$CUSTOM_HOME/.config/fastfetch"
|
||||
link_config "$HOME/.config/starship.toml" "$CUSTOM_HOME/.config/starship.toml"
|
||||
|
||||
echo "--> Done! Enter via: distrobox enter $NAME"
|
||||
'')
|
||||
];
|
||||
};
|
||||
flake.modules.nixos.virtualisation = {
|
||||
config,
|
||||
lib,
|
||||
pkgs,
|
||||
...
|
||||
}: let
|
||||
cfg = config.tnix.virtualisation;
|
||||
in {
|
||||
options.tnix.virtualisation.distrobox = {
|
||||
enable = lib.mkEnableOption "Enable DistroBox";
|
||||
};
|
||||
|
||||
config = lib.mkIf cfg.distrobox.enable {
|
||||
environment.systemPackages = with pkgs; [
|
||||
distrobox
|
||||
|
||||
(writeShellScriptBin "dbox-create" ''
|
||||
#!/usr/bin/env bash
|
||||
|
||||
# 1. Initialize variables
|
||||
IMAGE=""
|
||||
NAME=""
|
||||
|
||||
# Array to hold optional arguments (like volumes)
|
||||
declare -a EXTRA_ARGS
|
||||
|
||||
# 2. Parse arguments
|
||||
while [[ $# -gt 0 ]]; do
|
||||
case $1 in
|
||||
-i|--image)
|
||||
IMAGE="$2"
|
||||
shift 2
|
||||
;;
|
||||
-n|--name)
|
||||
NAME="$2"
|
||||
shift 2
|
||||
;;
|
||||
-p|--profile)
|
||||
echo ":: Profile mode enabled: Mounting Nix store and user profiles (Read-Only)"
|
||||
# Add volume flags to the array
|
||||
EXTRA_ARGS+=( "--volume" "/nix/store:/nix/store:ro" )
|
||||
EXTRA_ARGS+=( "--volume" "/etc/profiles/per-user:/etc/profiles/per-user:ro" )
|
||||
EXTRA_ARGS+=( "--volume" "/etc/static/profiles/per-user:/etc/static/profiles/per-user:ro" )
|
||||
shift 1
|
||||
;;
|
||||
*)
|
||||
echo "Unknown option $1"
|
||||
exit 1
|
||||
;;
|
||||
esac
|
||||
done
|
||||
|
||||
if [ -z "$IMAGE" ] || [ -z "$NAME" ]; then
|
||||
echo "Usage: dbox-create -i <image> -n <name> [-p]"
|
||||
exit 1
|
||||
fi
|
||||
|
||||
# 3. Define the custom home path
|
||||
CUSTOM_HOME="$HOME/Distrobox/$NAME"
|
||||
|
||||
echo "------------------------------------------------"
|
||||
echo "Creating Distrobox: $NAME"
|
||||
echo "Location: $CUSTOM_HOME"
|
||||
echo "------------------------------------------------"
|
||||
|
||||
# 4. Run Distrobox Create
|
||||
# We expand "''${EXTRA_ARGS[@]}" to properly pass the volume arguments
|
||||
${pkgs.distrobox}/bin/distrobox create \
|
||||
--image "$IMAGE" \
|
||||
--name "$NAME" \
|
||||
--home "$CUSTOM_HOME" \
|
||||
"''${EXTRA_ARGS[@]}"
|
||||
|
||||
# Check exit code
|
||||
if [ $? -ne 0 ]; then
|
||||
echo "Error: Distrobox creation failed."
|
||||
exit 1
|
||||
fi
|
||||
|
||||
# 5. Post-Creation: Symlink Config Files
|
||||
echo "--> Linking configurations to $NAME..."
|
||||
|
||||
# Helper function to symlink
|
||||
link_config() {
|
||||
SRC="$1"
|
||||
DEST="$2"
|
||||
DEST_DIR=$(dirname "$DEST")
|
||||
|
||||
# Create parent directory if it doesn't exist
|
||||
mkdir -p "$DEST_DIR"
|
||||
|
||||
if [ -e "$SRC" ]; then
|
||||
# ln -sf: symbolic link, force overwrite
|
||||
ln -sf "$SRC" "$DEST"
|
||||
echo " [LINK] $DEST -> $SRC"
|
||||
else
|
||||
echo " [SKIP] $SRC not found on host"
|
||||
fi
|
||||
}
|
||||
|
||||
# Create Symlinks
|
||||
link_config "$HOME/.zshrc" "$CUSTOM_HOME/.zshrc"
|
||||
link_config "$HOME/.zshenv" "$CUSTOM_HOME/.zshenv"
|
||||
link_config "$HOME/.config/fastfetch" "$CUSTOM_HOME/.config/fastfetch"
|
||||
link_config "$HOME/.config/starship.toml" "$CUSTOM_HOME/.config/starship.toml"
|
||||
|
||||
echo "--> Done! Enter via: distrobox enter $NAME"
|
||||
'')
|
||||
];
|
||||
};
|
||||
};
|
||||
}
|
||||
|
||||
Some files were not shown because too many files have changed in this diff Show More
Reference in New Issue
Block a user